Cybersecurity Governance
Effectively manage your cybersecurity and IT GRC
Centralize IT and cyber risks, controls, regulatory requirements, incidents, and action plans in a single platform to strengthen governance and improve oversight.
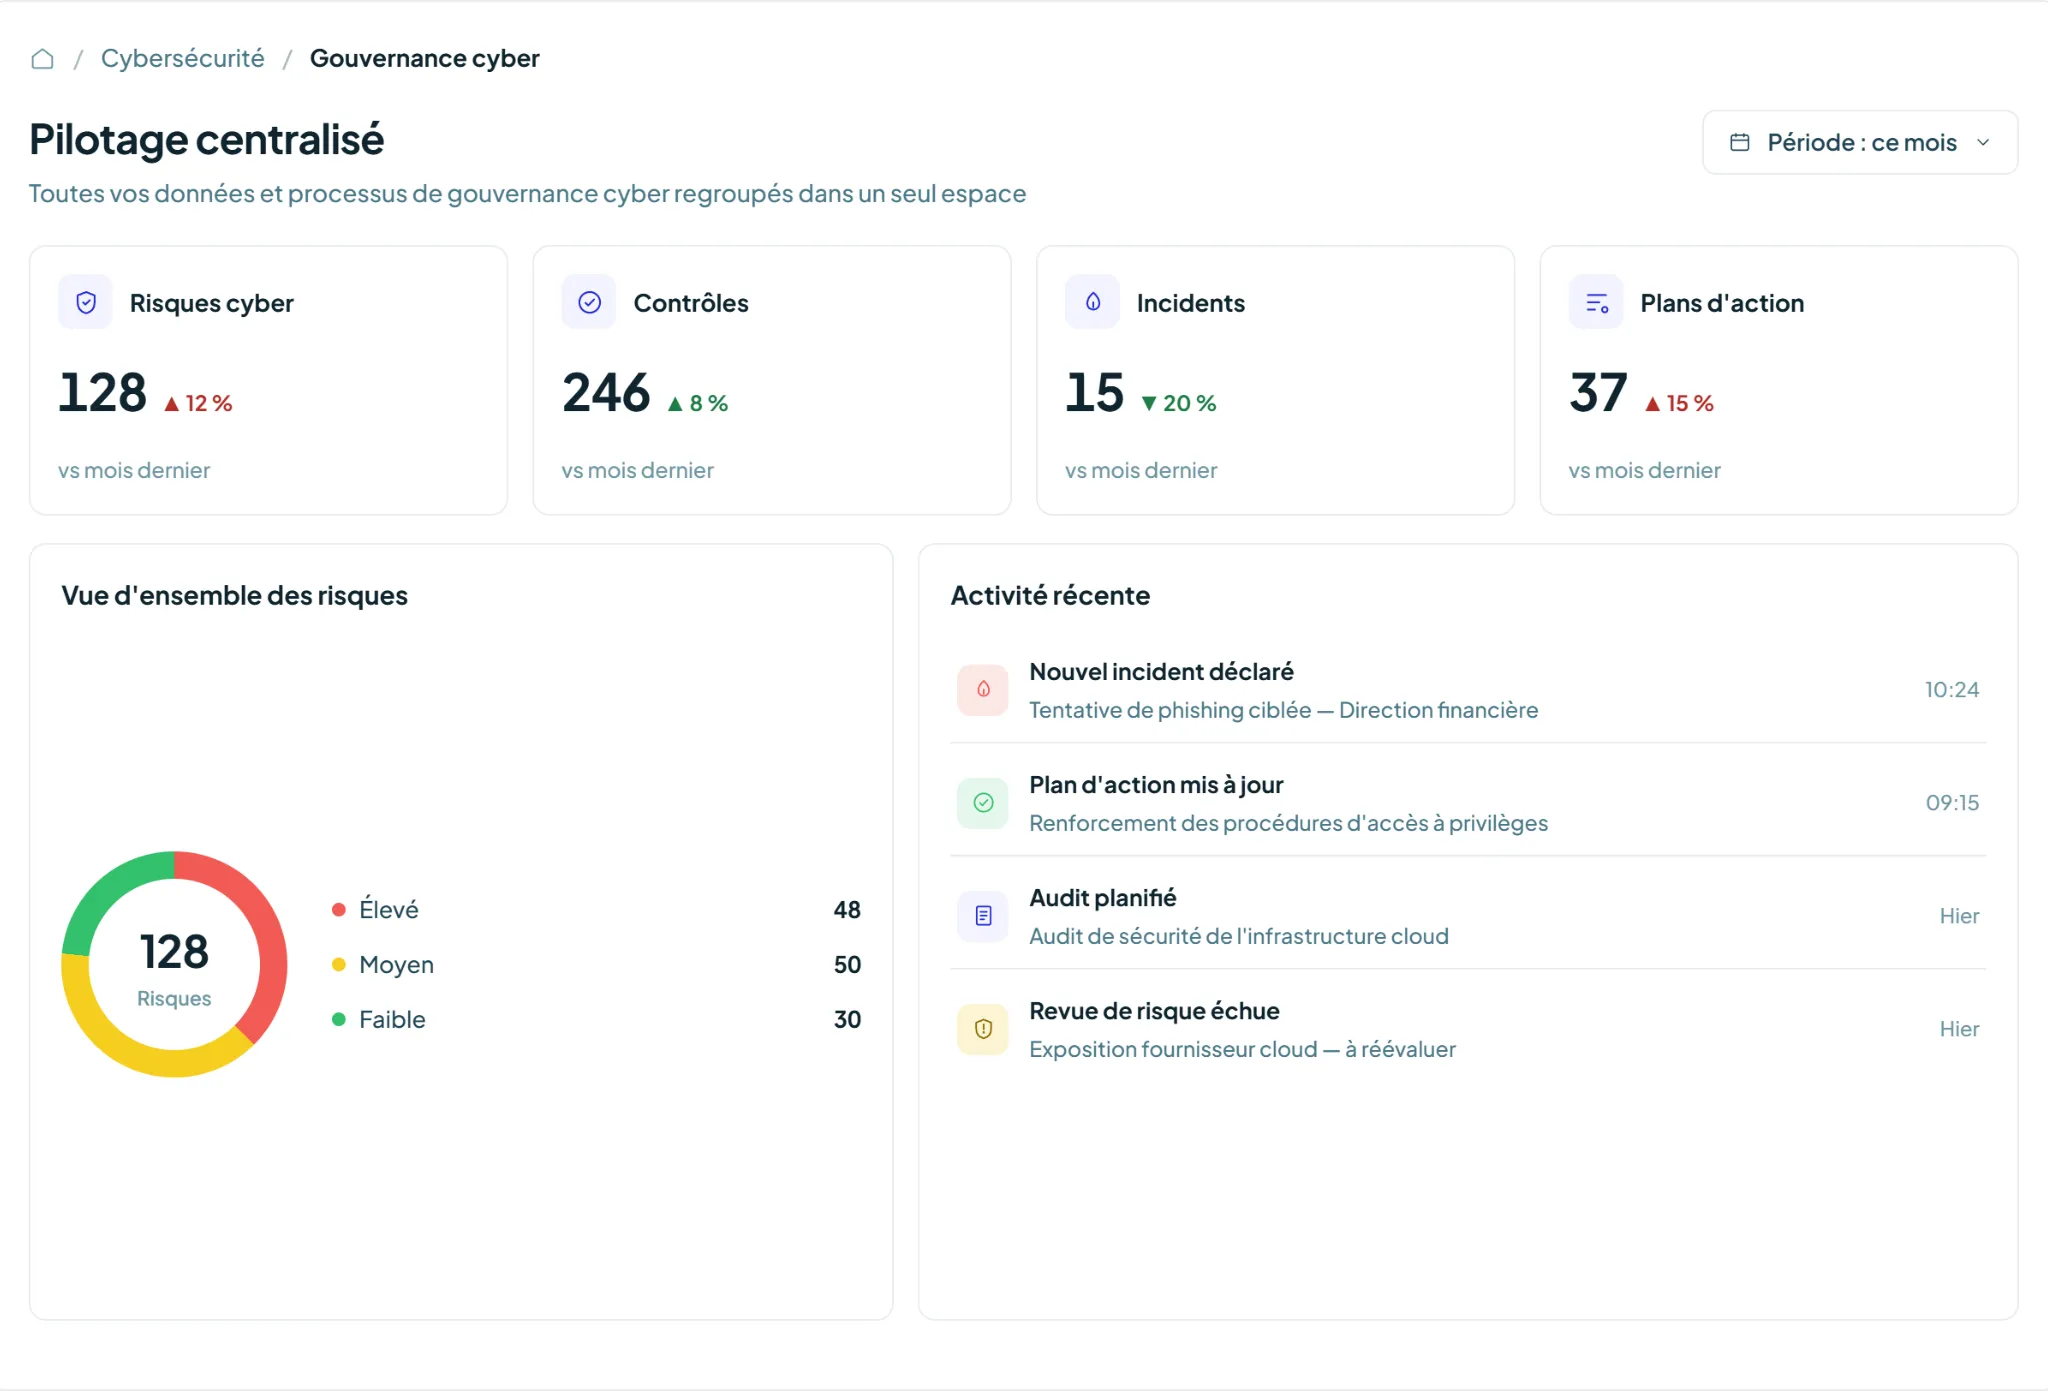
Structure your cybersecurity governance and stay in control of risk
Centralize cyber risks, controls, incidents, and action plans. Manage regulatory requirements and frameworks such as ISO 27001, NIS2, and DORA while making it easier to monitor your control environment and prepare for audits.
Build a unified IT & cyber framework
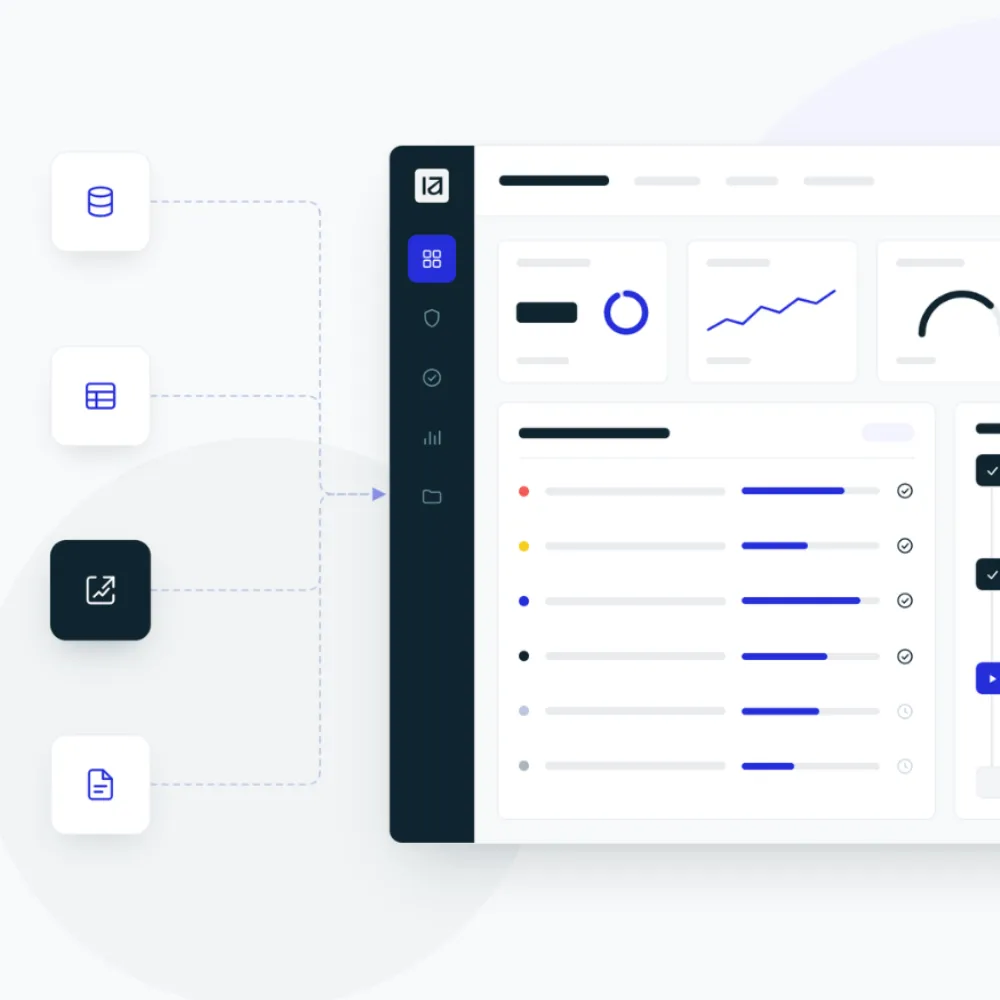
Bring every element of your cybersecurity governance into a single repository: cyber risks, assets, security measures, controls, regulatory requirements, and responsibilities.
Structure the framework around your organization and create a reliable foundation for managing your cybersecurity posture over time.
- Centralized cyber repository
- Flexible framework
- Consolidated view of your cybersecurity program
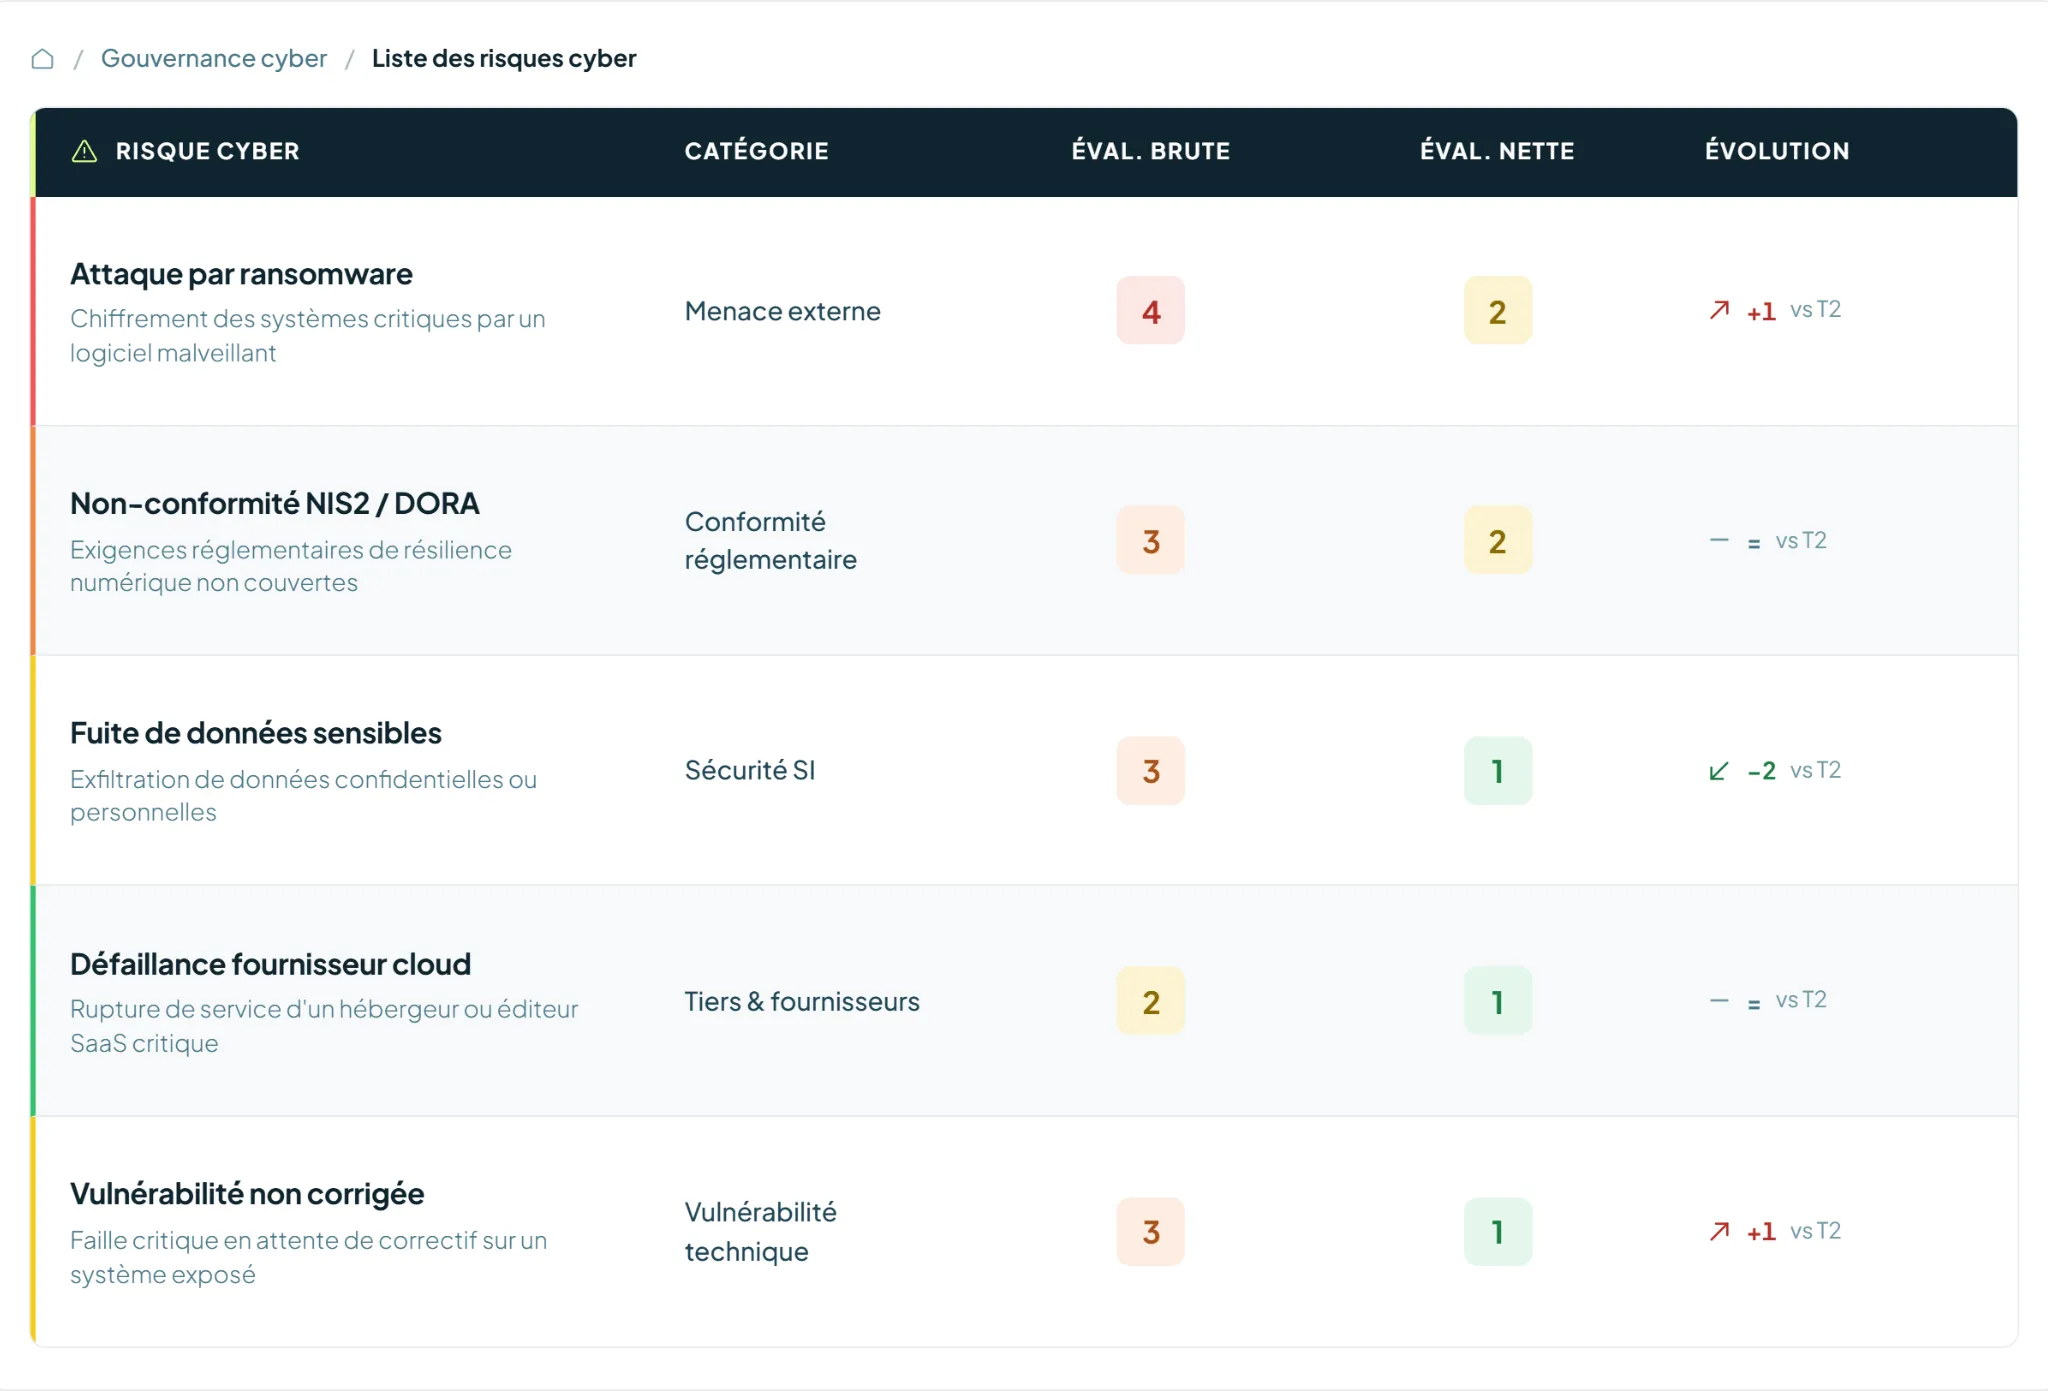
Assess cyber risks and track how they evolve
Identify threats that could affect your organization, assess their criticality using your own criteria, and monitor how risks evolve over time.
Involve the right stakeholders, customize assessment methods, and retain a complete history to support better decision-making.
- Customizable assessments
- Assessment history
- Risk and threat prioritization
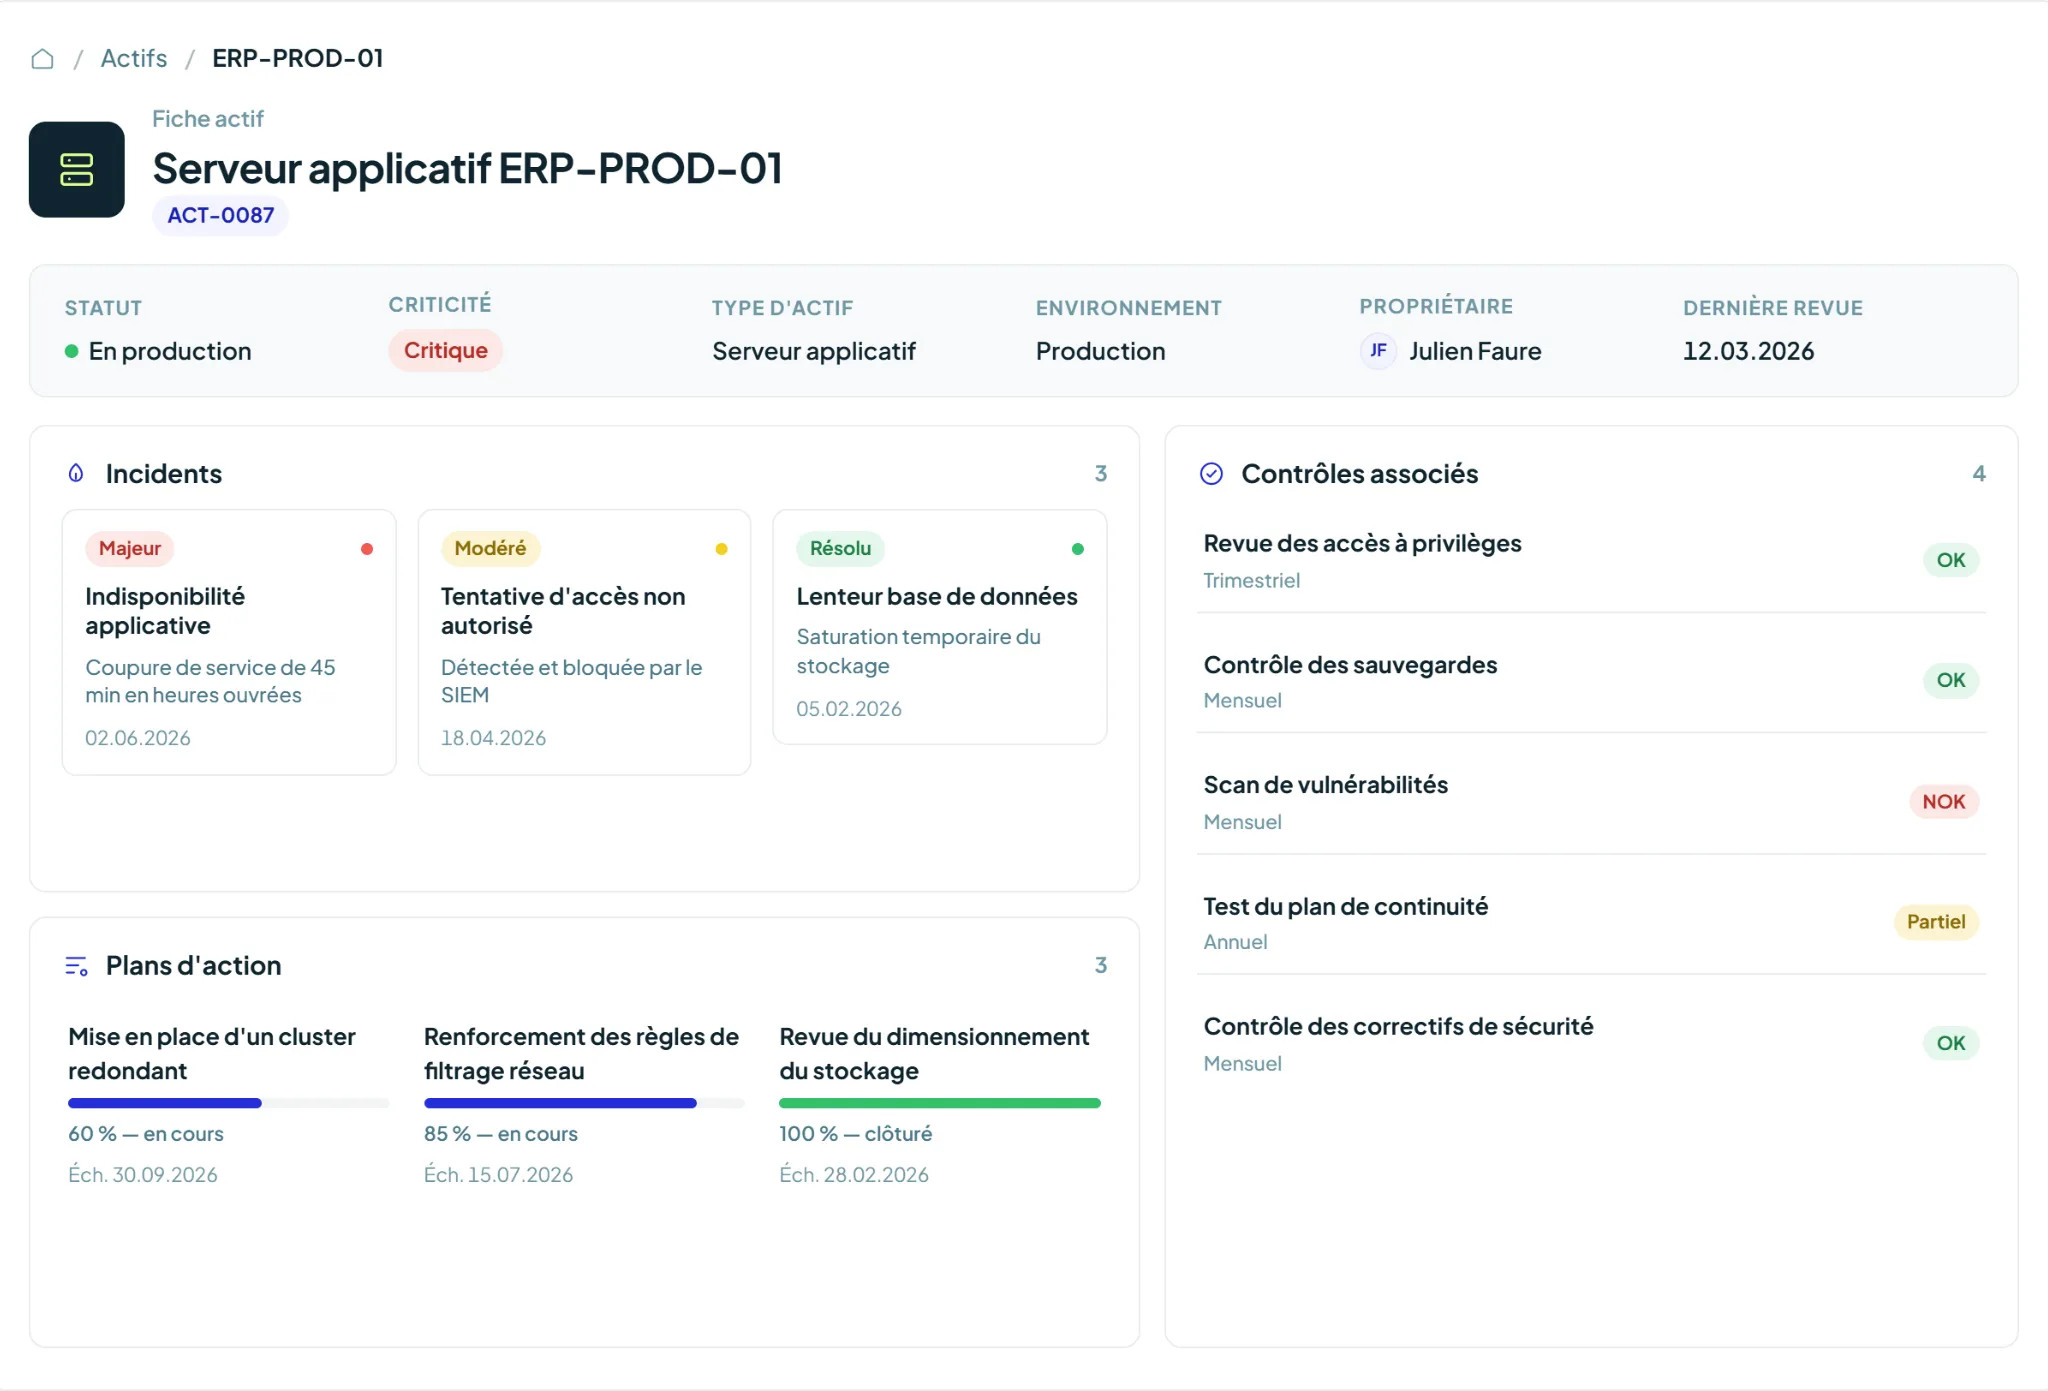
Manage controls, incidents, and action plans
Track cybersecurity controls, centralize incidents, manage action plans, and maintain a complete record of the measures implemented.
Connect every element to gain a clear, end-to-end view of your control environment.
- Cybersecurity control monitoring
- Streamlined incident management
- Centralized action plans
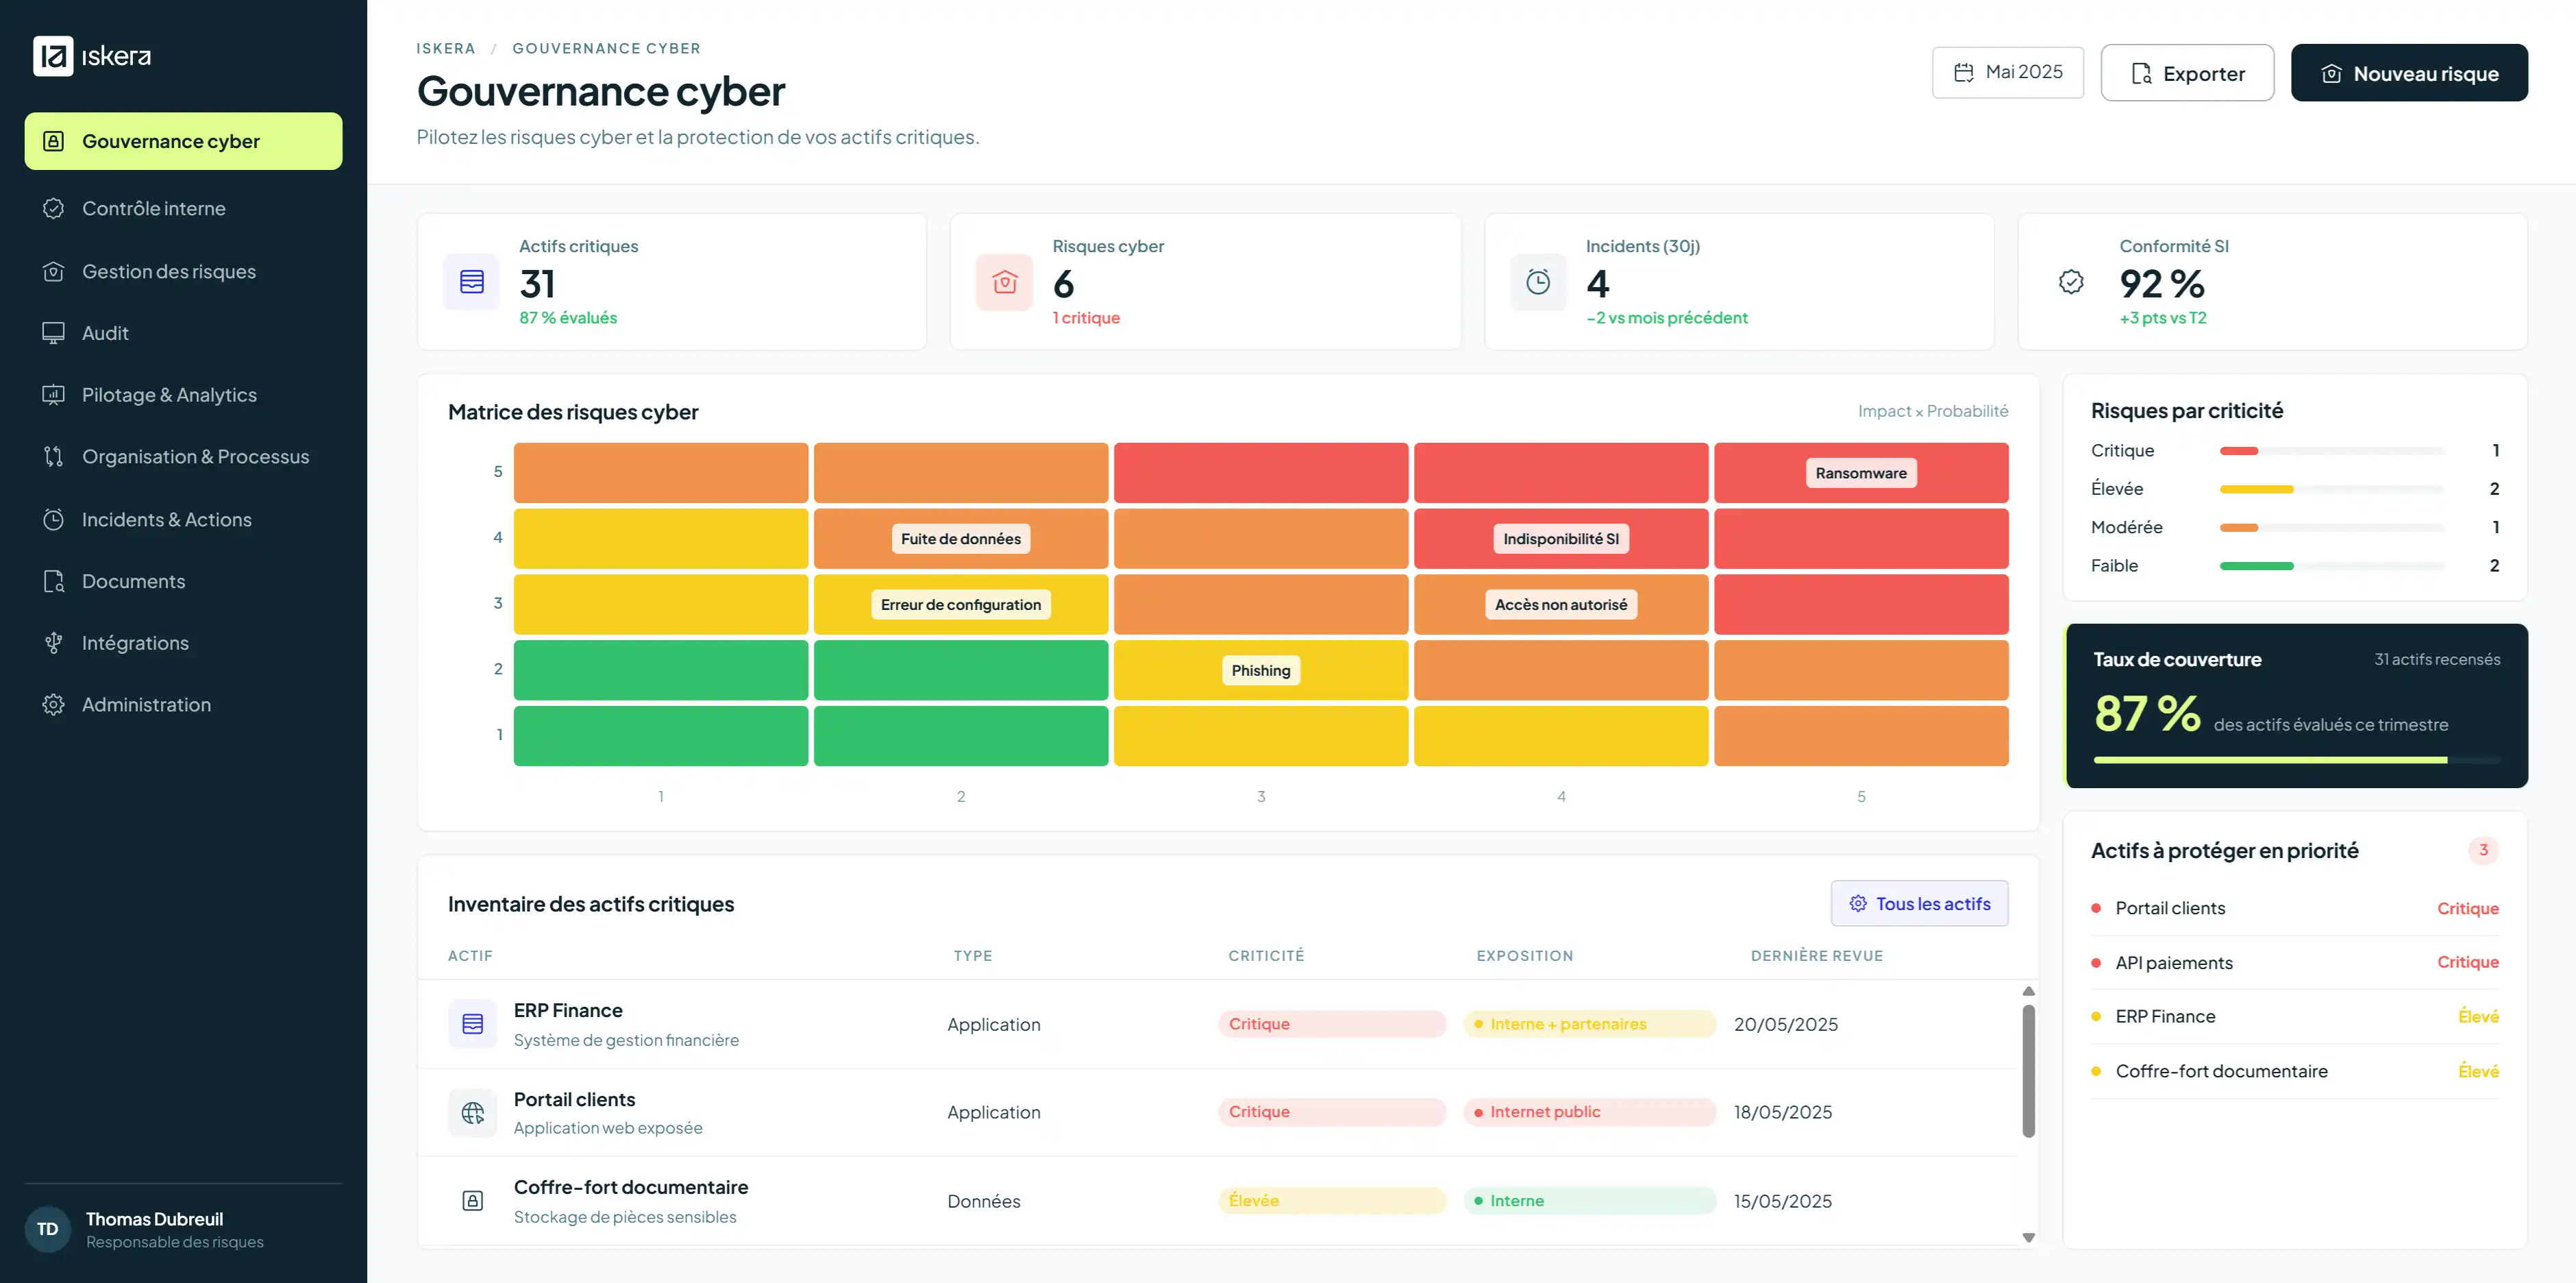
Manage cybersecurity with dashboards and AI
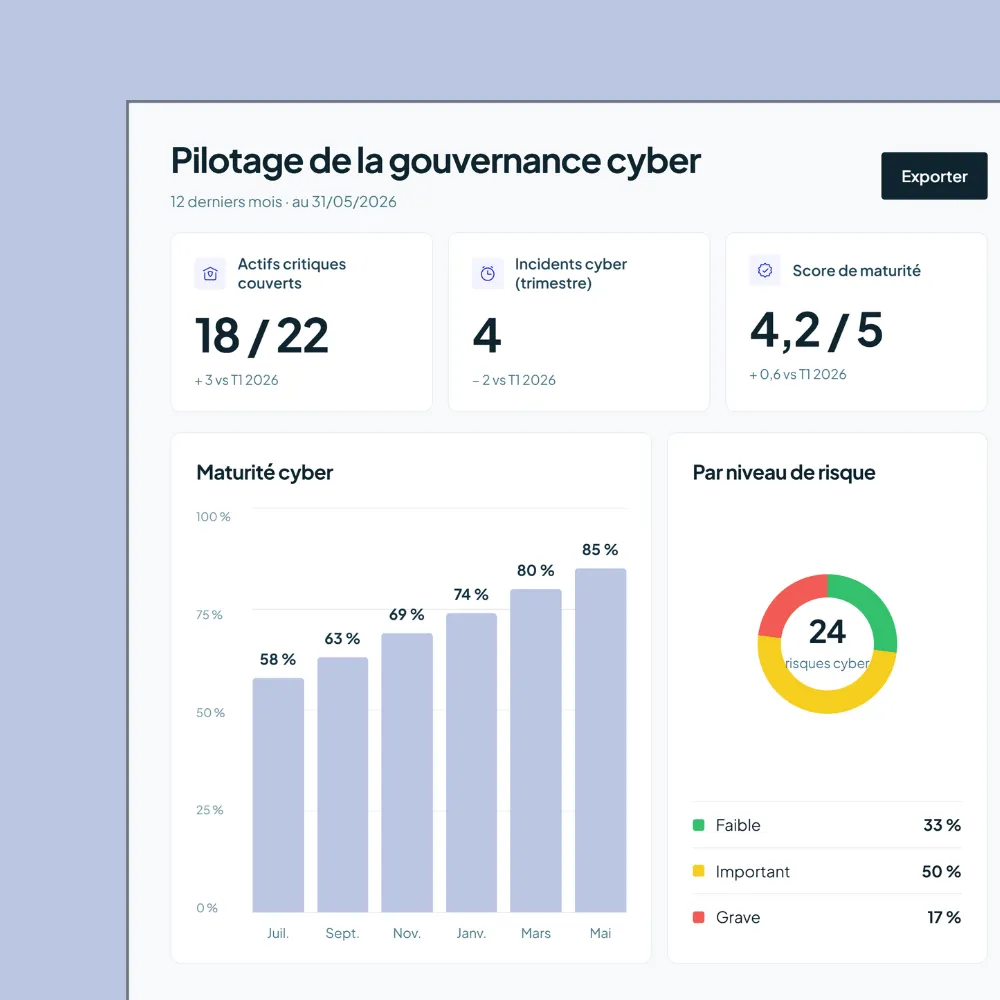
Monitor key cybersecurity indicators through interactive dashboards, automated reporting, and AI-assisted analysis.
Quickly identify priority risks, overdue controls, and actions to take to continuously strengthen your governance.
- Interactive dashboards
- Automated reporting
- AI-assisted analysis
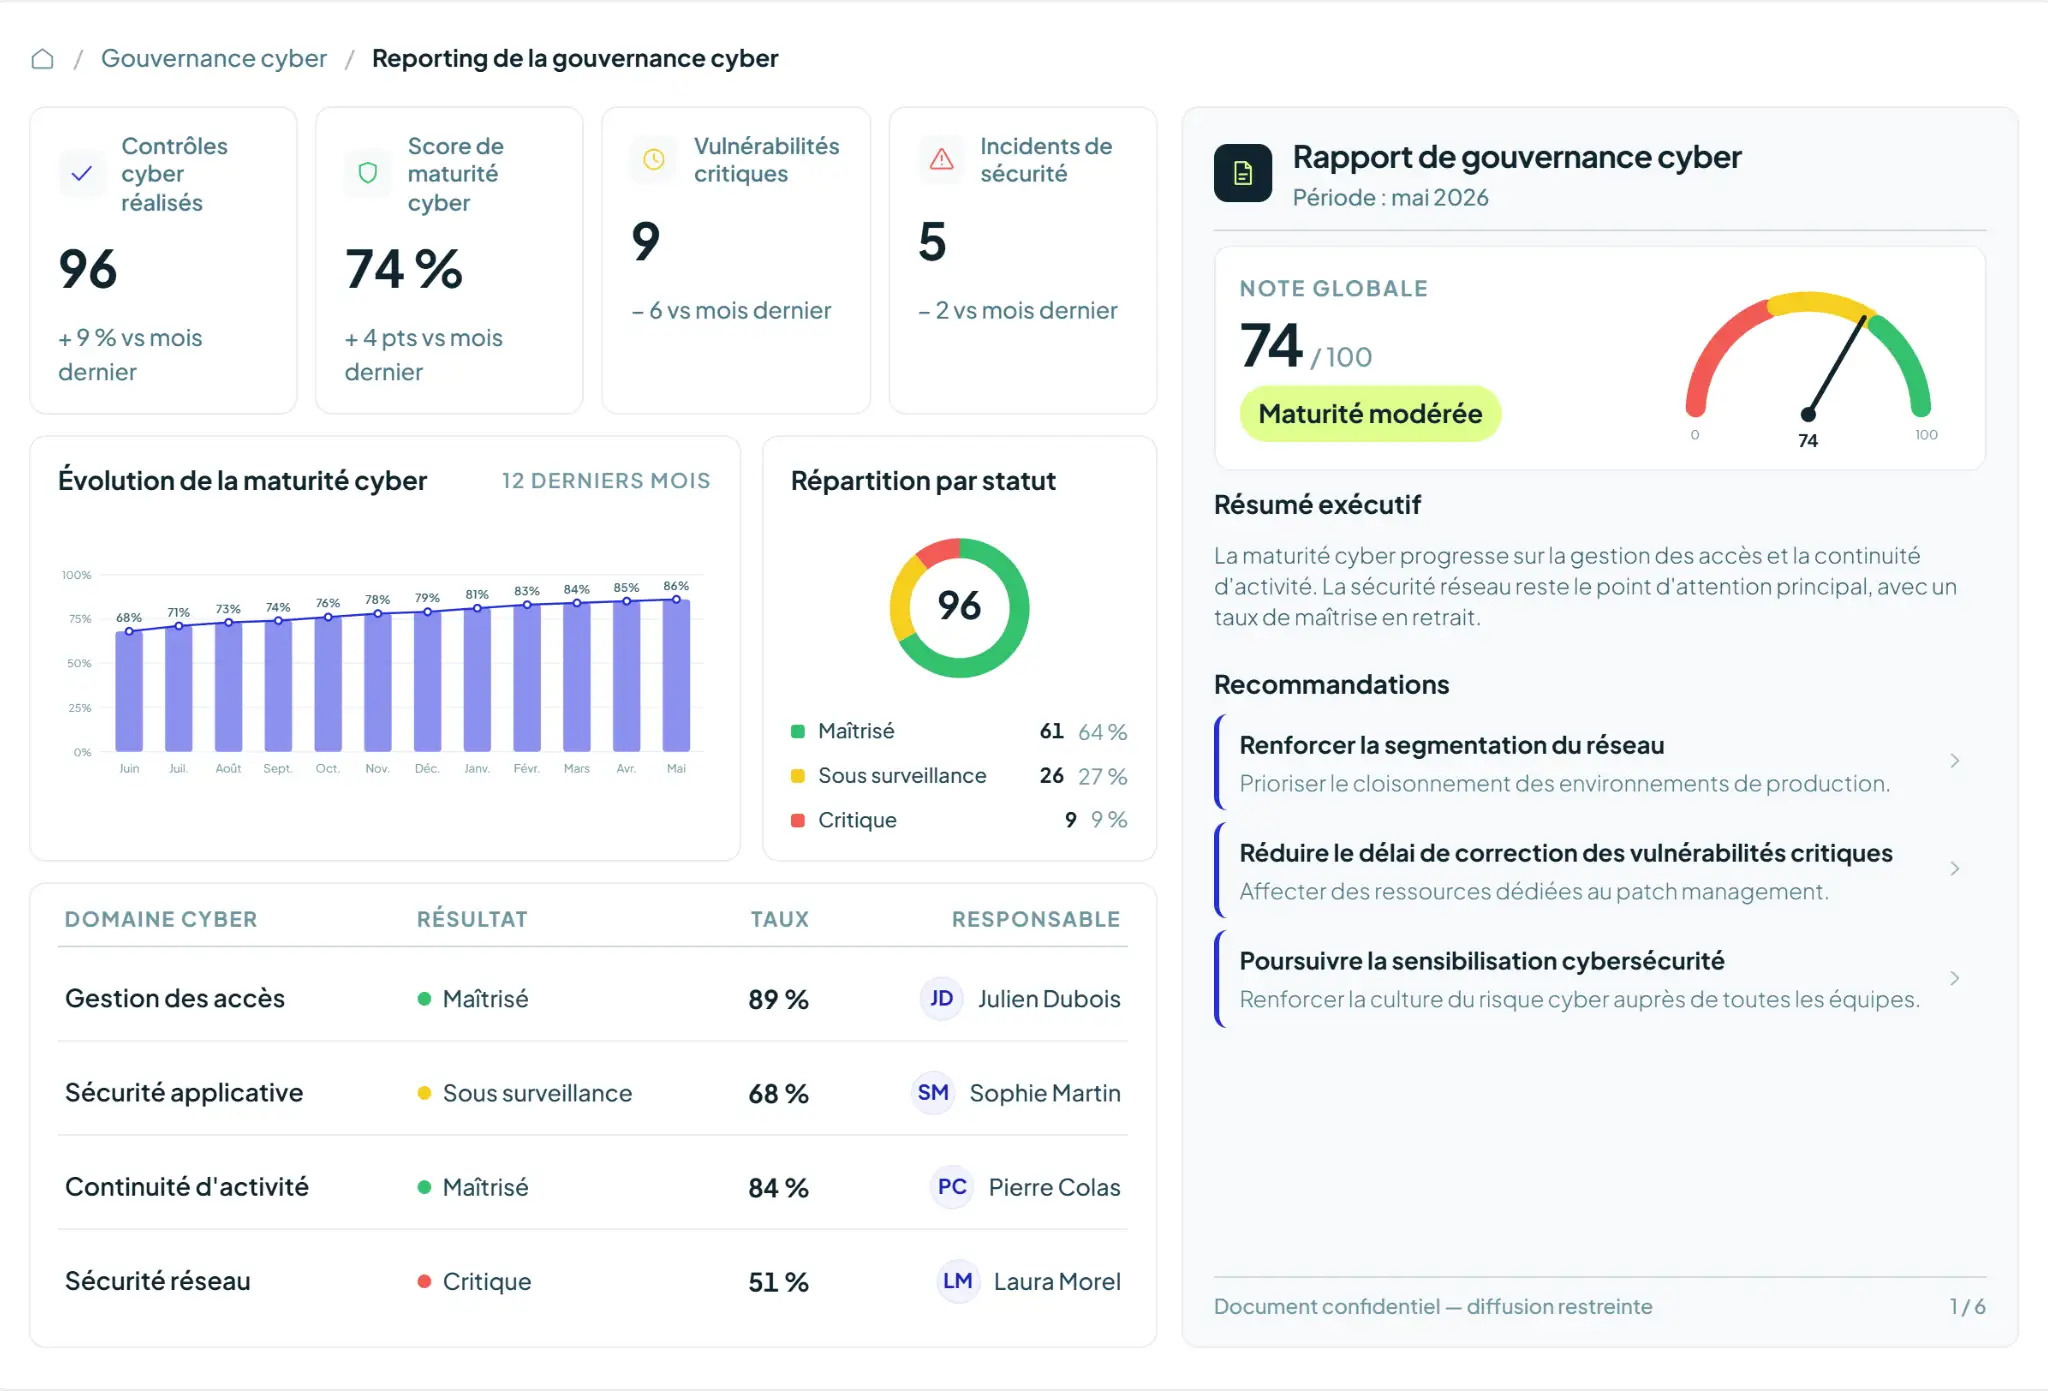
Cybersecurity governance that is more structured, more collaborative, and easier to manage

100%
of your cybersecurity governance framework centralized in a single platform
- 01
Anticipate risks before they become incidents
Gain a clear view of your cyber risk exposure to identify priorities, guide decisions, and reduce risk before incidents occur.
- 02
Strengthen regulatory compliance
Structure your approach to meet requirements from frameworks and regulations such as NIS2, DORA, and ISO 27001. Track actions and maintain complete traceability across your cybersecurity program.
- 03
Improve collaboration across teams
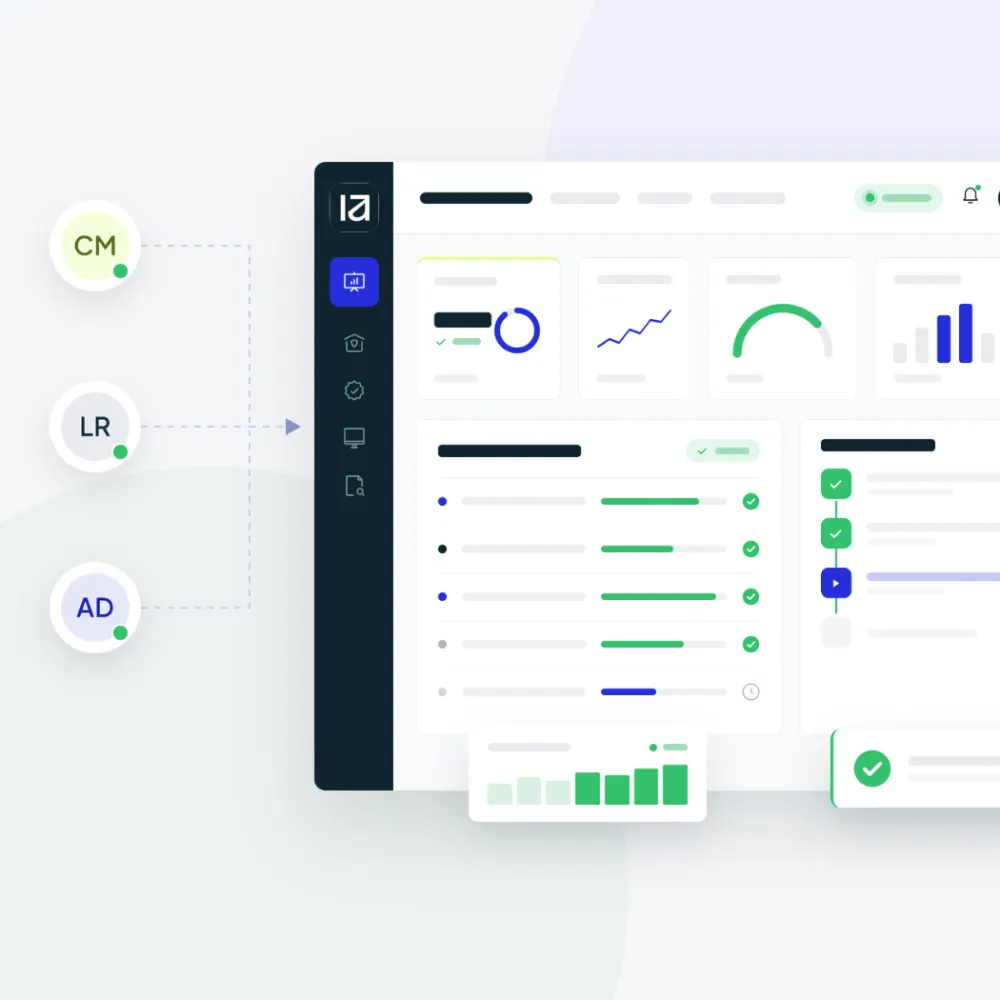
Bring business, IT, cybersecurity, risk, and compliance teams together on one platform. Give everyone a clear view of their responsibilities and the actions required to strengthen risk management.
- 04
Manage cybersecurity governance in real time
Monitor key indicators with interactive dashboards, automated reporting, and AI-assisted analysis. Quickly identify priority risks, overdue controls, incidents, and actions that require attention.
Deploy your cybersecurity governance in 3 steps
Build your governance around a single framework to anticipate risks more effectively and manage cybersecurity over time.
01
Identify and assess cyber risks
Map your assets, identify threats, and assess risks based on their criticality.
Adapt your assessment methods and criteria to your organization's context and priorities.
02
Structure your governance framework
Centralize risks, controls, incidents, action plans, and responsibilities.
Integrate requirements from frameworks such as ISO 27001, NIS2, and DORA to maintain a consistent view of your cybersecurity program.
03
Keep your cybersecurity governance up to date
Monitor controls, reassess risks, and manage action plans over time.
Measure your level of control and prepare more efficiently for audits, certifications, and regulatory deadlines.
Manage your program with comprehensive cybersecurity governance & IT GRC software
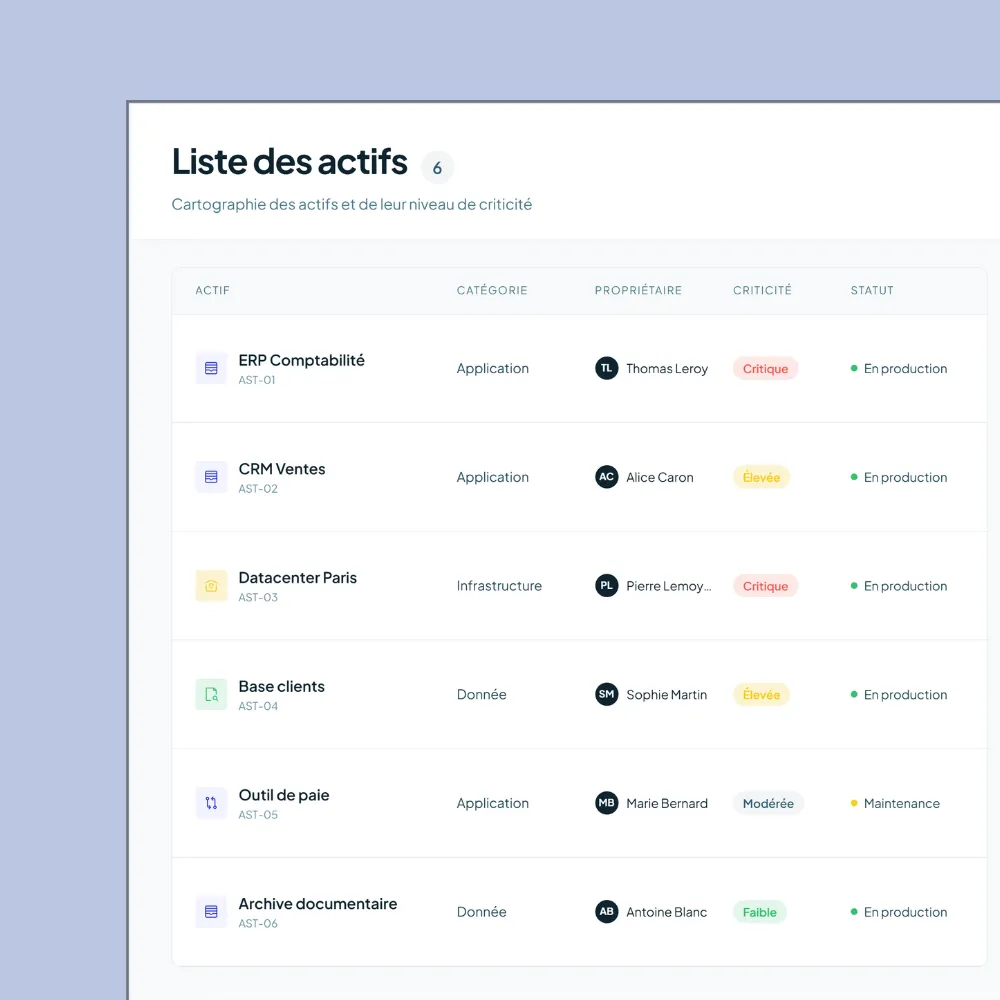
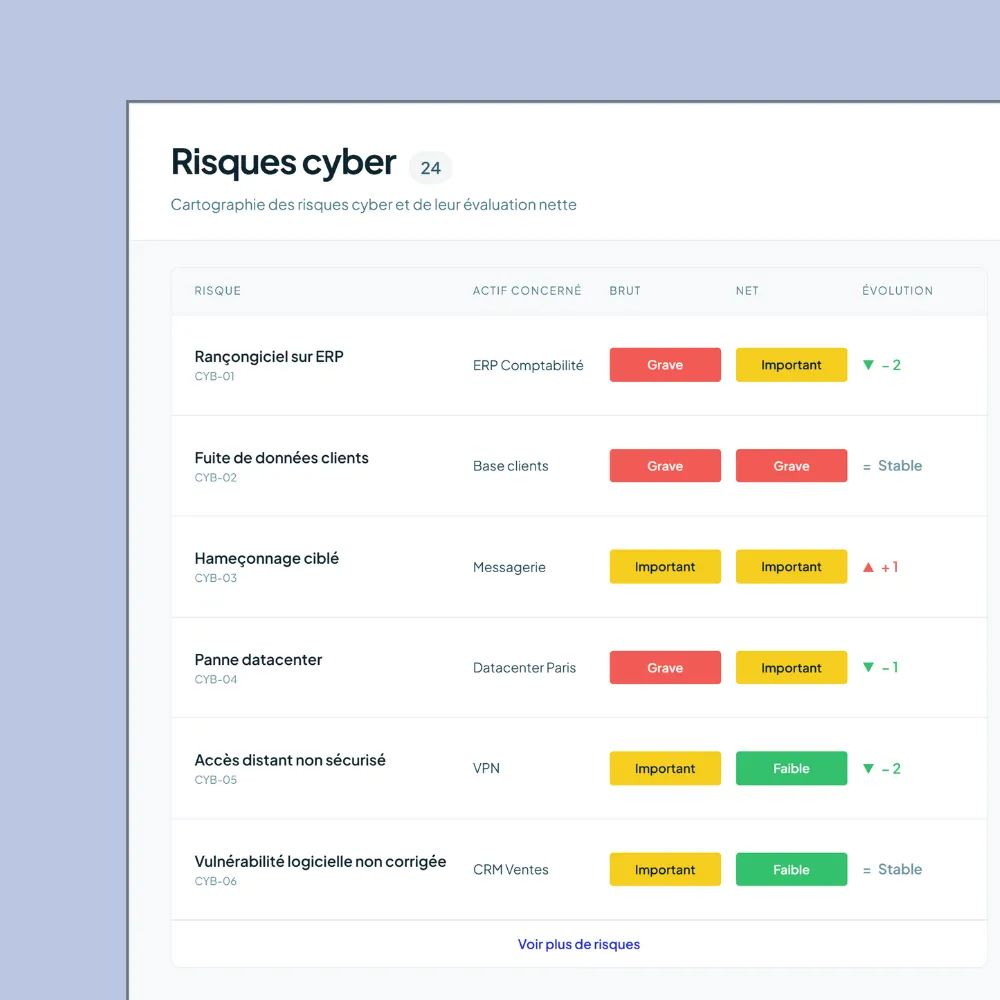
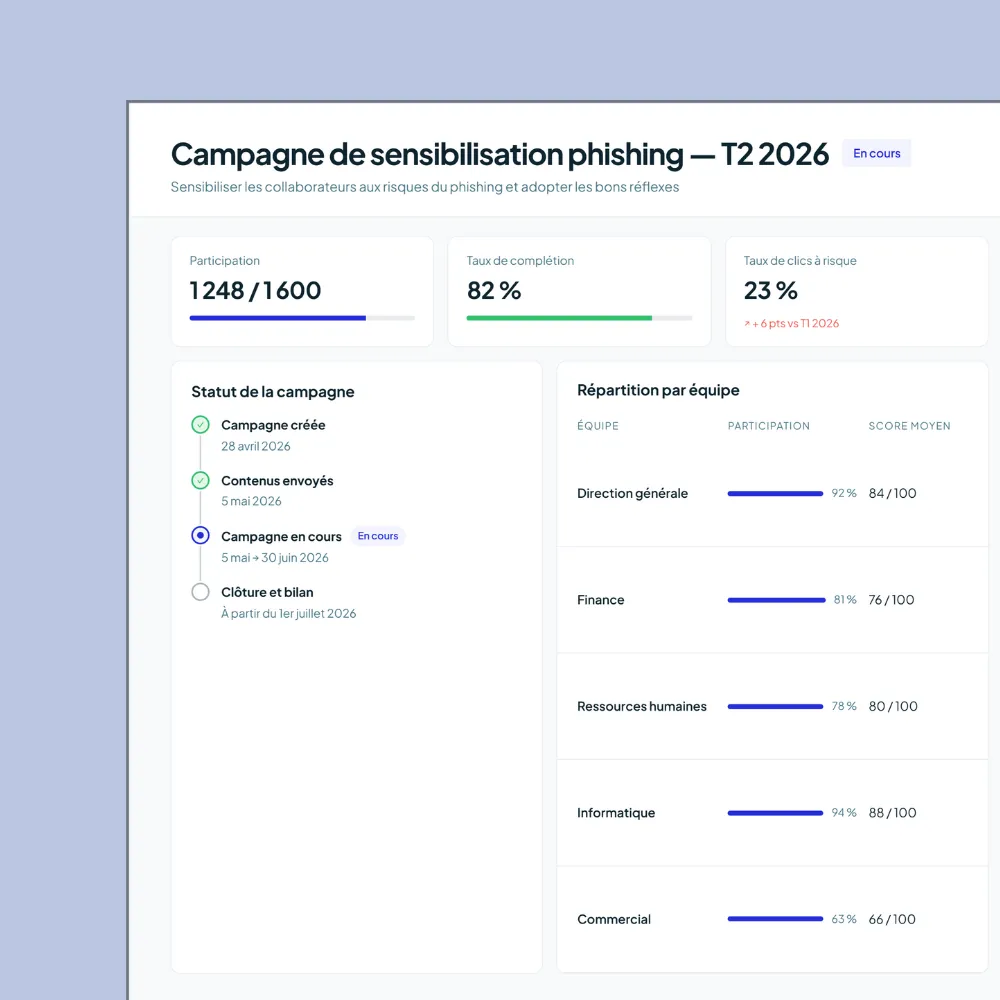
From your existing framework to fully operational cybersecurity governance
OTHER SOLUTIONS
Everything you need to manage risk day to day
Discover other Iskera solutions to connect cybersecurity governance with risk management, internal control, regulatory compliance, and enterprise-wide oversight.
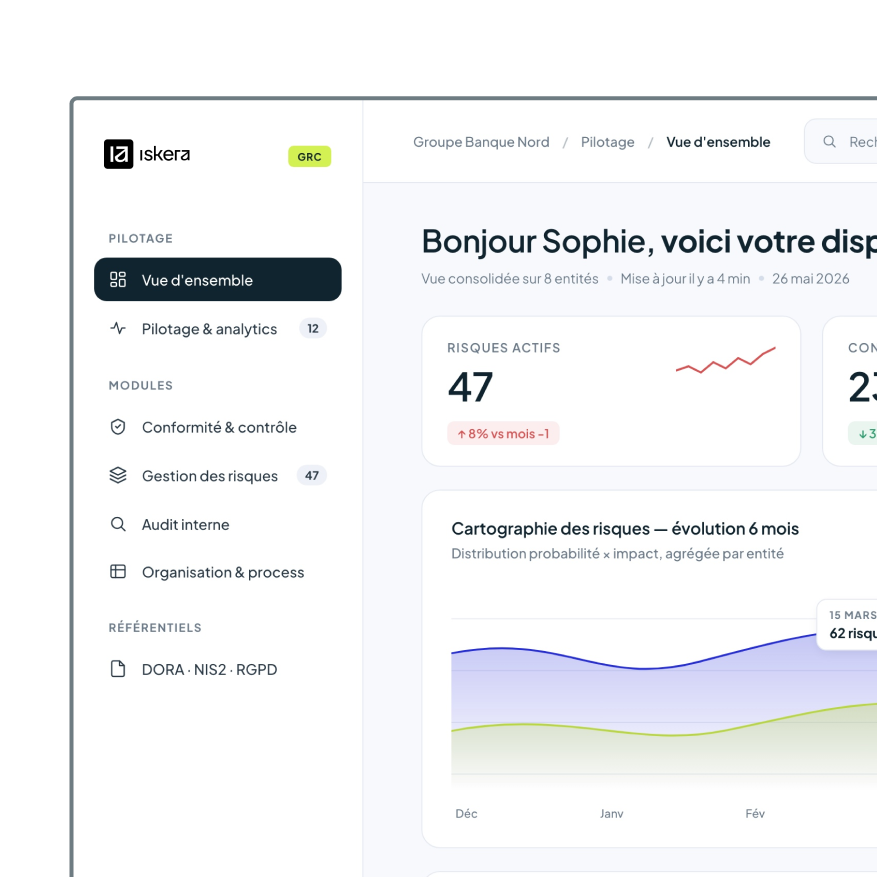
A demo that speaks your language, a clear vision as a result
See how Iskera helps you structure cybersecurity governance, manage cyber risks, coordinate controls, and track regulatory requirements from a single platform.
Latest resources
Frequently asked questions
Cybersecurity governance software helps organizations structure and manage their cybersecurity program from a single platform. It centralizes assets, risks, controls, regulatory requirements, incidents, and action plans to improve visibility, traceability, and decision-making.
Iskera helps organizations manage regulatory and standards-based requirements by centralizing information, controls, evidence, and action plans. The platform can support frameworks and regulations such as ISO 9001, ISO 27001, NIS2, DORA, CSRD, Solvency II, Basel III, and Sapin II.
No. Iskera does not replace technical security solutions such as EDR, SIEM, vulnerability scanners, or firewalls. It provides the governance layer by centralizing risks, controls, incidents, regulatory requirements, and action plans to give teams a consolidated view of the cybersecurity program.
Pricing depends on factors such as the number of users, modules deployed, functional scope, and your organization's requirements. Our team will help define the right setup and provide a tailored quote.