NIS2
Structure your NIS2 framework in a single platform
Centralize requirements, cyber risks, critical assets, incidents, suppliers, controls and continuity plans.
Iskera connects the different parts of your framework so you can monitor your level of control and actions over time.
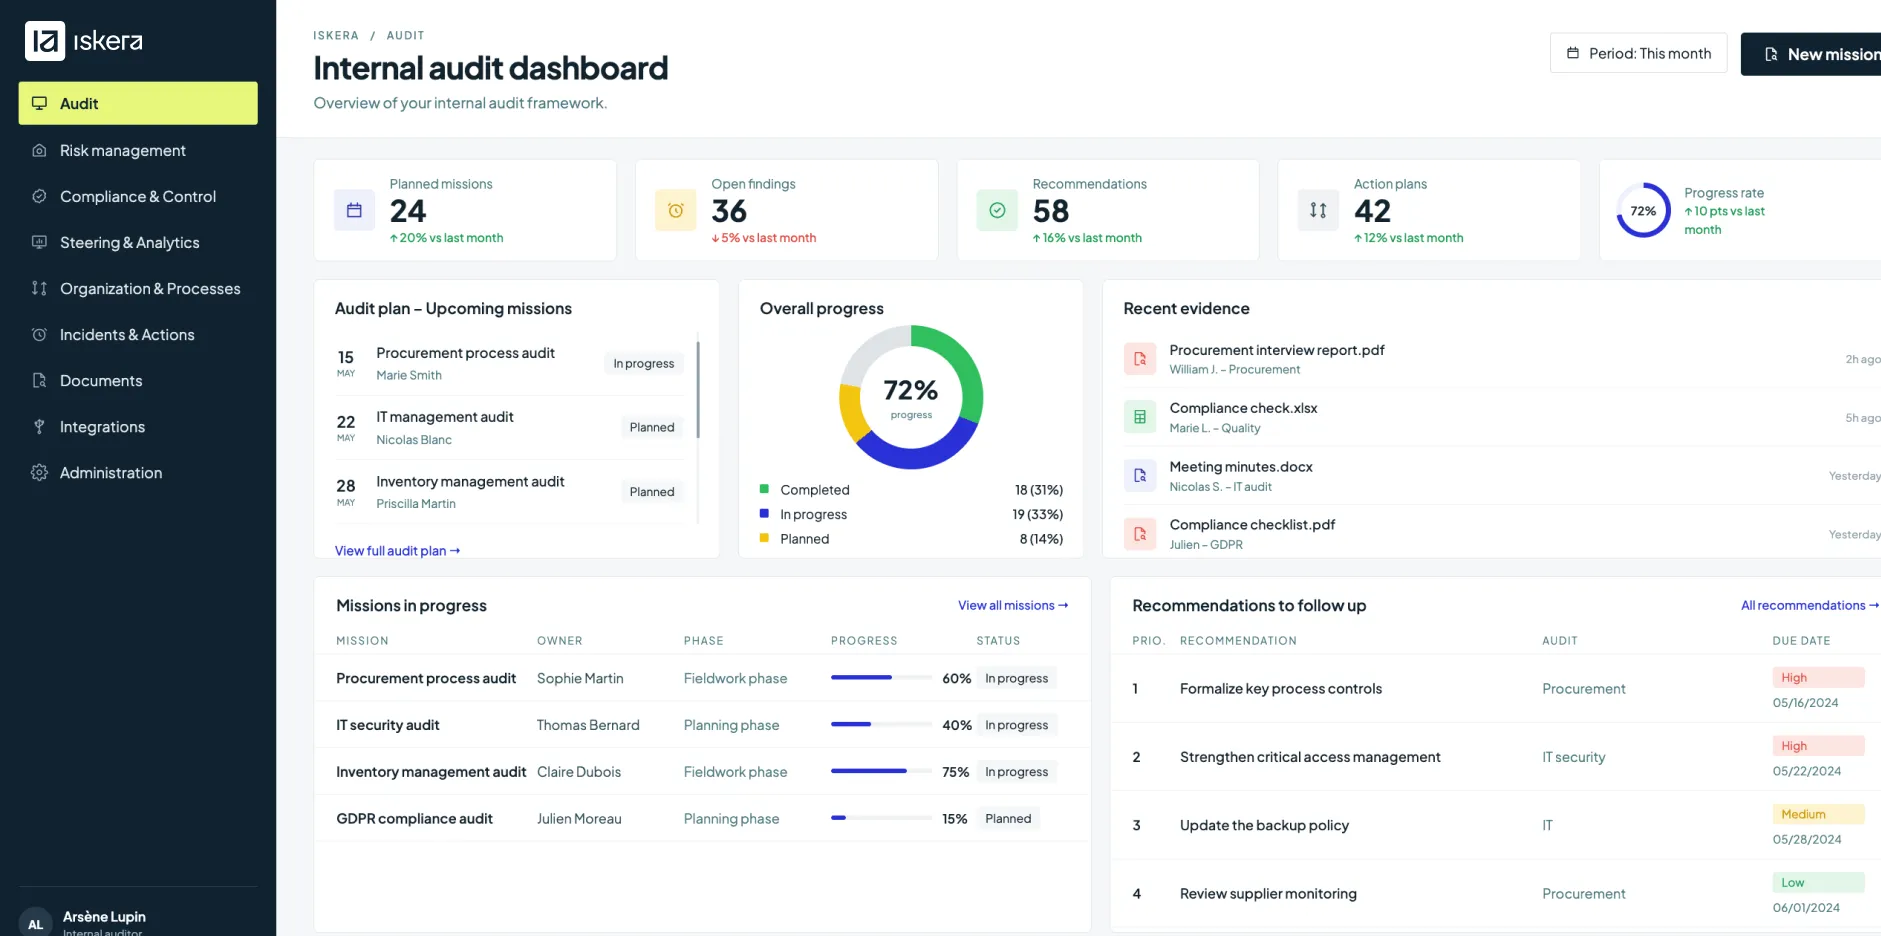
Turn NIS2 requirements into a framework you can manage
NIS2 strengthens cybersecurity requirements for many organizations considered essential or important. The directive requires a structured approach to cyber risk management, incidents, business continuity, supply chain security and governance.
Iskera brings this information together to help you monitor risks, requirements, controls and remediation over time.
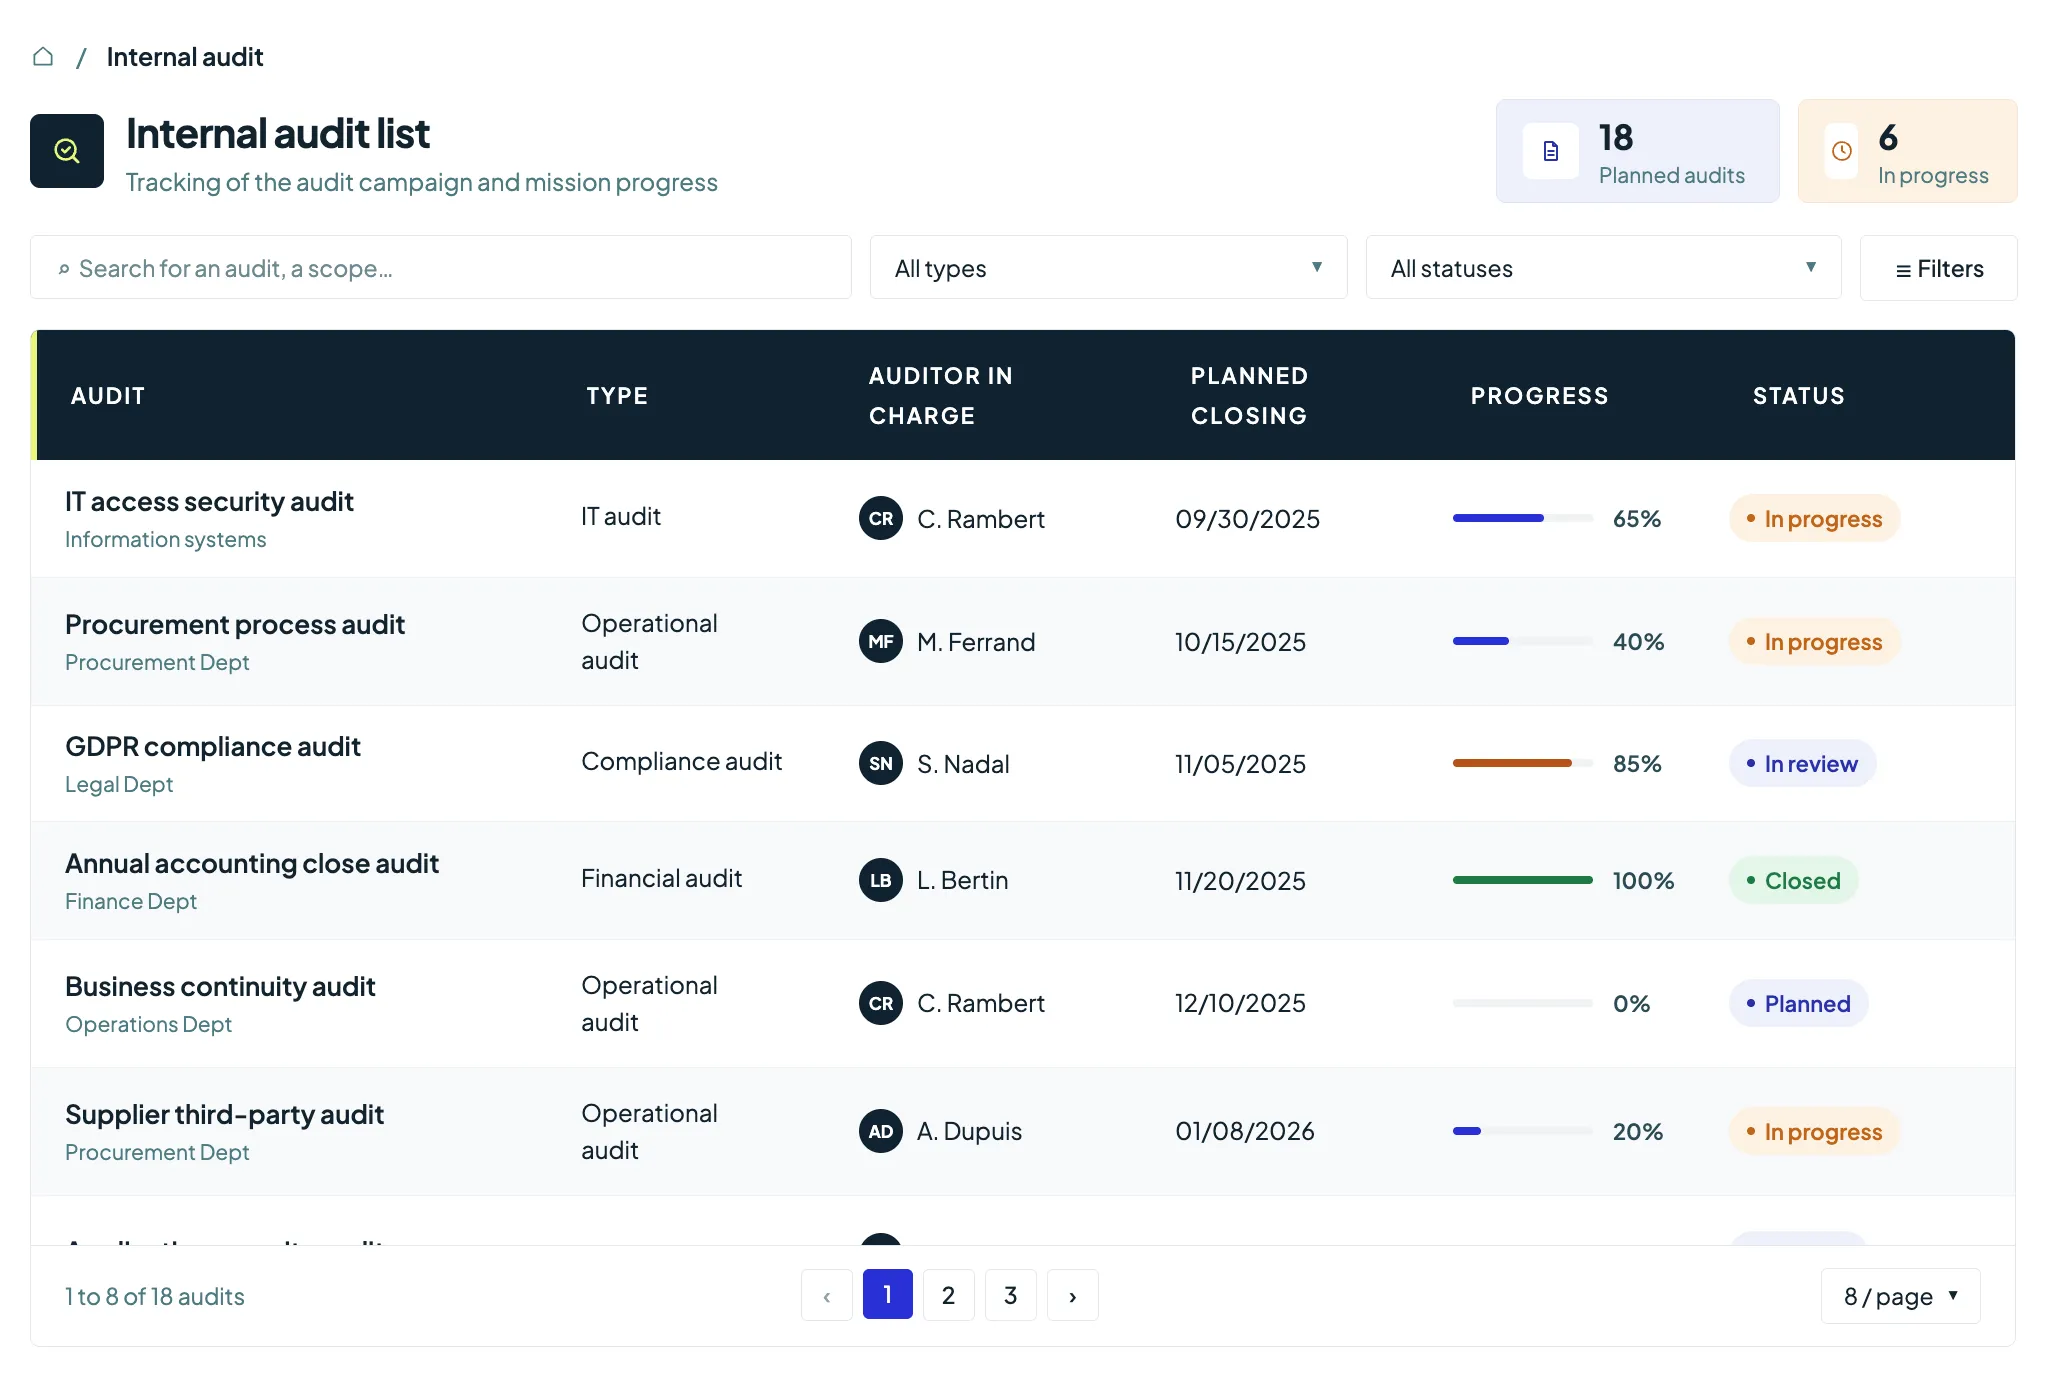
Structure your cyber risk management
Identify risks that could affect your systems, activities and critical services. Link them to assets, processes, controls and owners for a consistent, up-to-date risk map.
- Consolidated view of cyber risks and criticality
- Prioritization of critical assets and activities
- Linked controls and actions
Manage incidents and regulatory reporting
Centralize cybersecurity incidents, assess impacts and maintain a full timeline of events. Organize escalation and significant incident notifications: early warning within 24 hours, notification within 72 hours and, in principle, a final report within one month.
Structurez l'escalade et les notifications des incidents significatifs : alerte précoce sous 24 heures, notification sous 72 heures et, en principe, rapport final dans le mois.
- Rapid response to significant incidents
- Traceability of decisions and actions
- Notification and remediation tracking
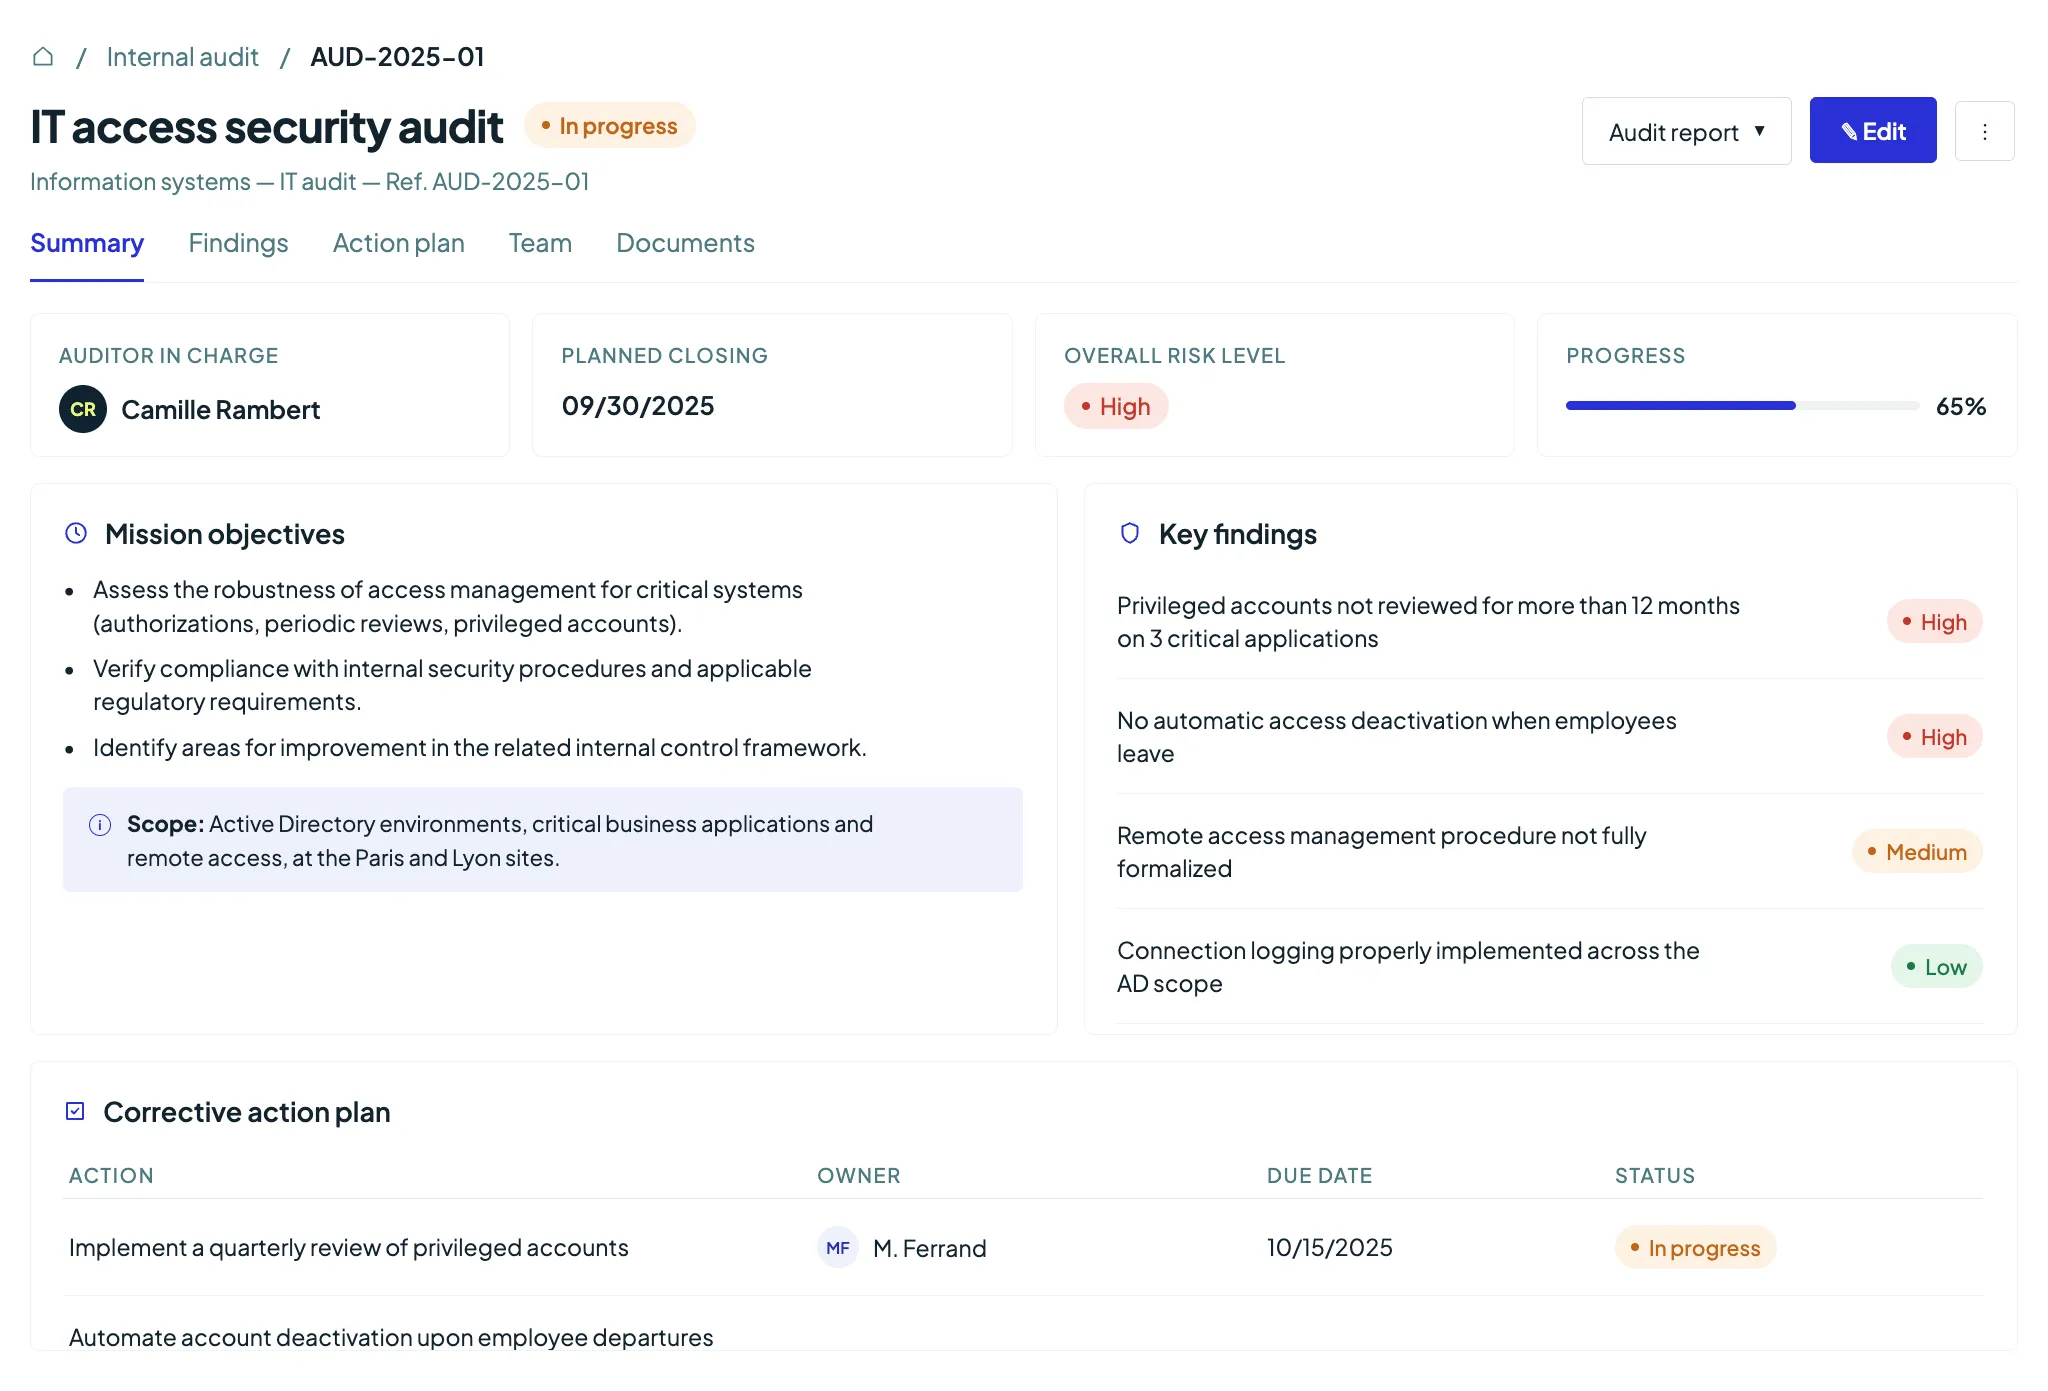
Manage supply chain risks
Identify suppliers and providers your critical activities depend on. Assess their risks and centralize evaluations and documents. Track measures to reduce supply chain exposure in line with NIS2.
Suivez les mesures engagées pour réduire votre exposition aux risques de la chaîne d'approvisionnement, conformément aux exigences de NIS2.
- Visibility of critical suppliers
- Centralized assessments and documents
- Remediation tracking
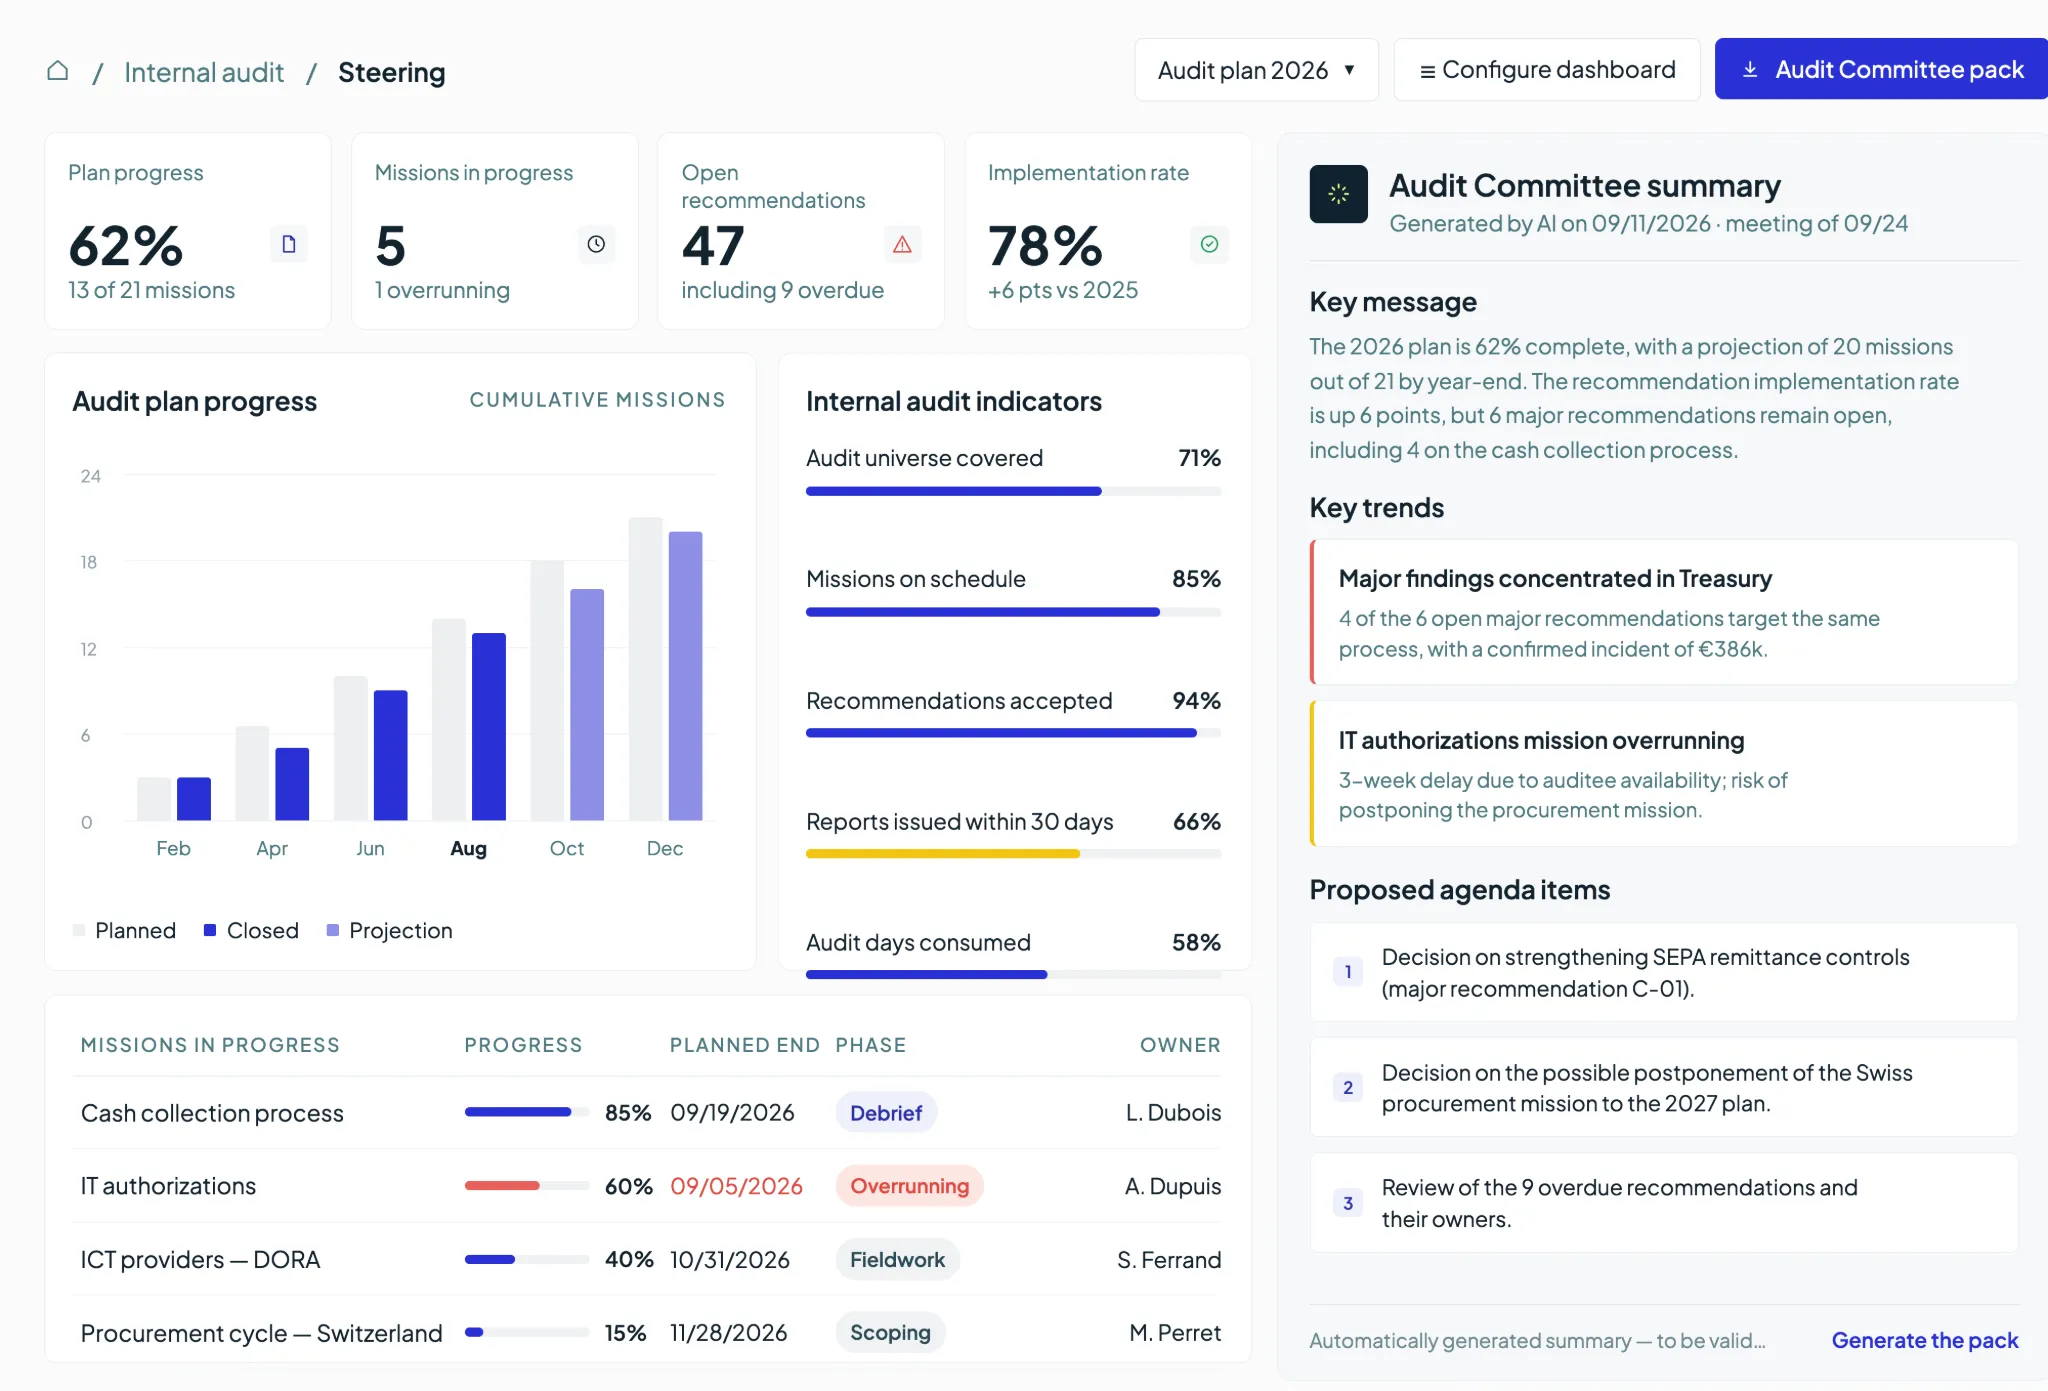
Manage NIS2 compliance over time
Bring requirements, risks, controls, incidents, audits and action plans together in shared dashboards. Identify priority gaps and follow remediation through to resolution to simplify reporting and audits.
Identifiez les écarts prioritaires et suivez leur traitement jusqu'à leur résolution pour faciliter les reportings et les audits.
- Requirements coverage and priority gaps
- Action plans and remediation
- Dashboards and reporting
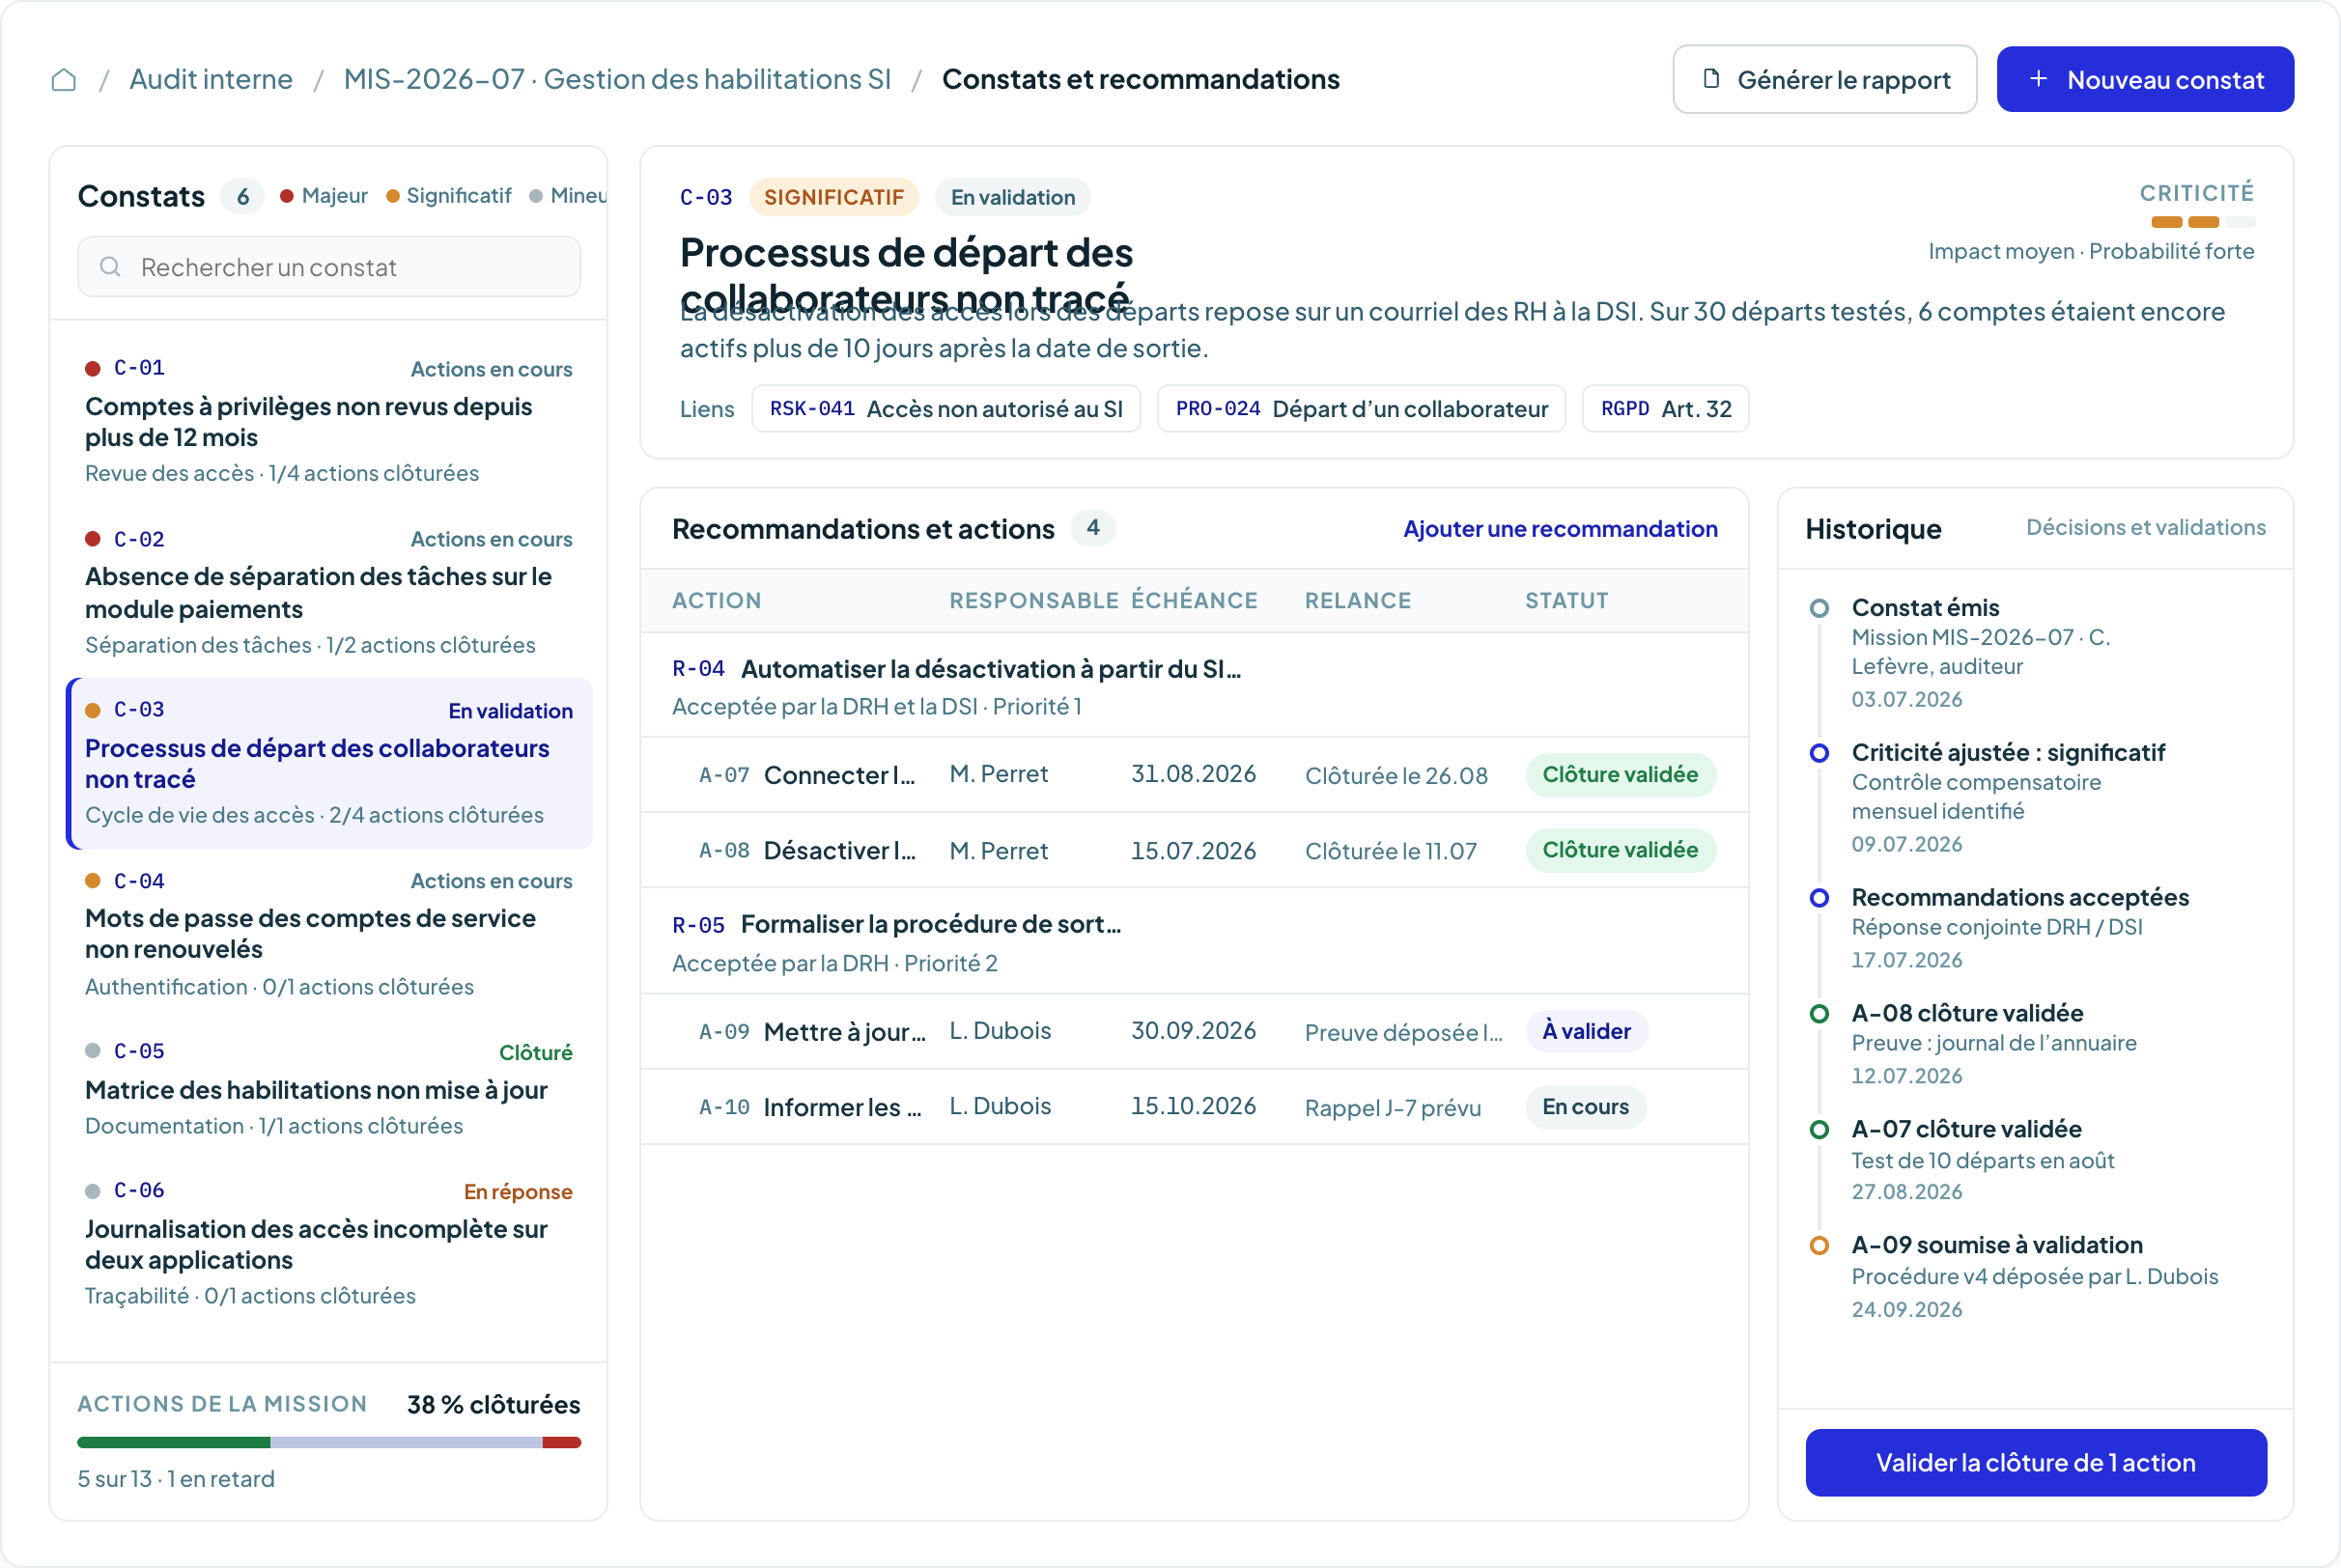
A NIS2 framework that is clearer, more traceable and easier to manage

100%
of your requirements, risks, incidents, third parties, controls and actions brought together in one environment
- 01
Compliance that is easier to demonstrate
Link NIS2 requirements to policies, controls, responsibilities, documents and evidence showing how they are addressed.
- 02
A clear view of your cyber risks
Connect risks, assets, processes and critical activities to identify vulnerabilities requiring priority attention.
- 03
A better-managed supply chain
Centralize suppliers, criticality, assessments and actions taken to reduce associated risks.
- 04
Remediation under control
Bring together gaps from risk assessments, incidents, audits and evaluations and track resolution through to closure.
Build your NIS2 framework in 3 steps
Bring together the elements of your framework to move from fragmented compliance to continuous cyber risk management.
01
Map your framework
Import existing requirements, risks, assets, critical activities, suppliers and controls. Connect them to build a consistent view of your NIS2 framework.
Structurez leurs relations pour disposer d'une représentation cohérente de votre dispositif NIS2.
02
Assess your level of control
Analyze risks, document existing measures and identify gaps between your current framework and applicable requirements.
03
Manage remediation
Prioritize actions, assign responsibilities, track deadlines and consolidate progress in dashboards for teams and management.
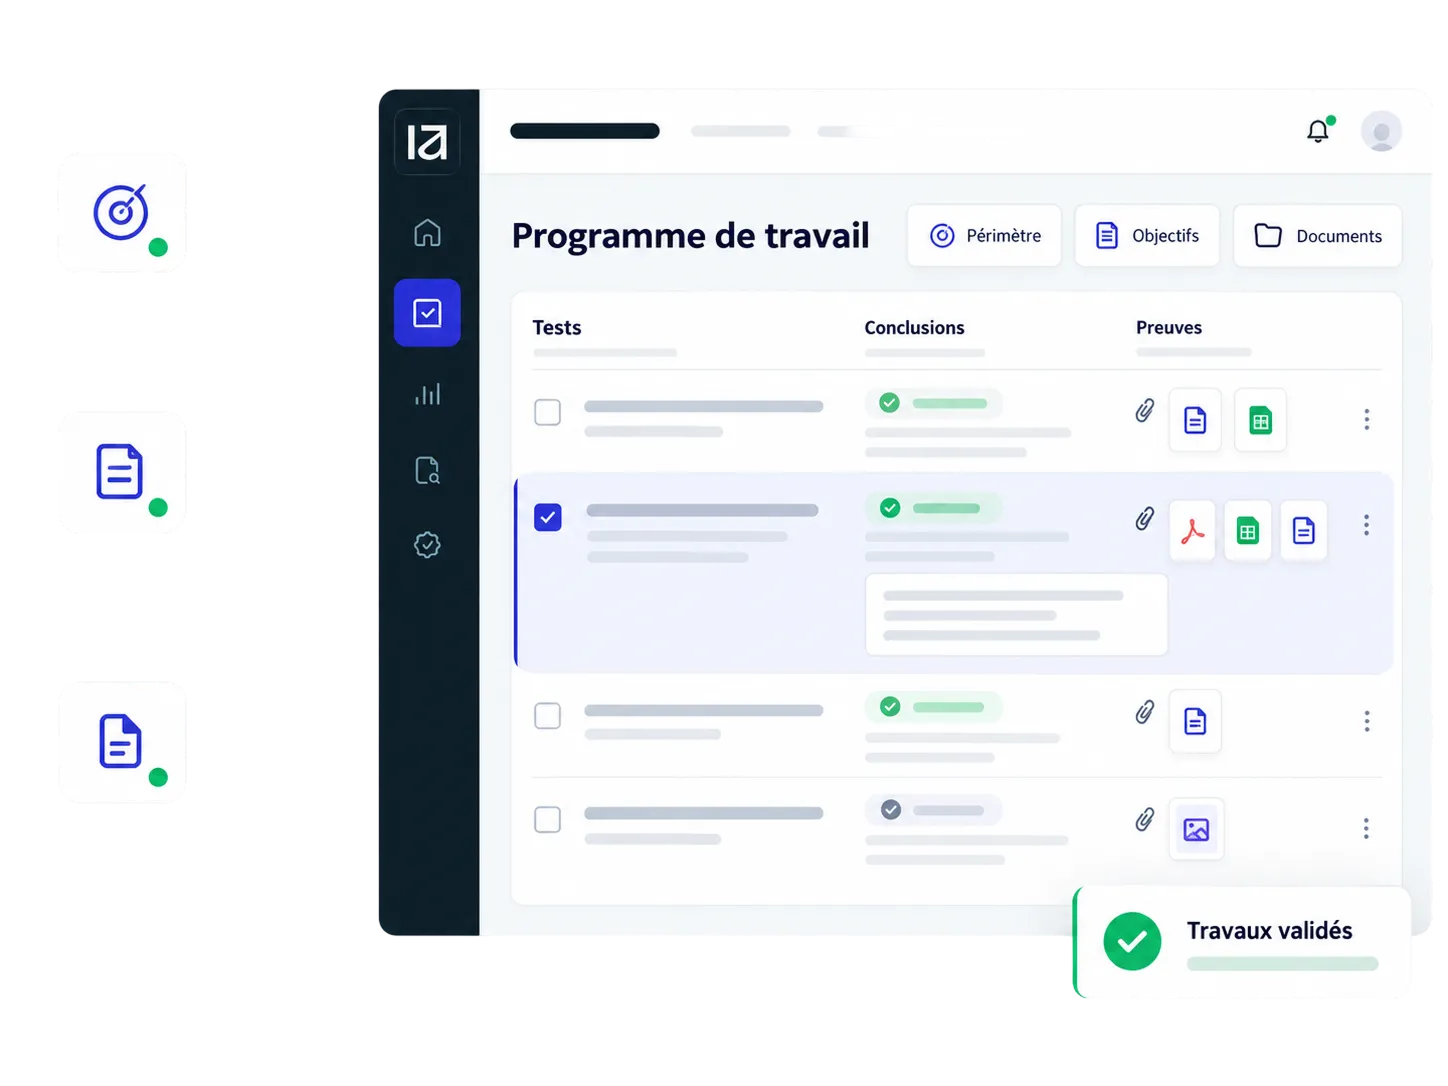
Manage your NIS2 framework day to day
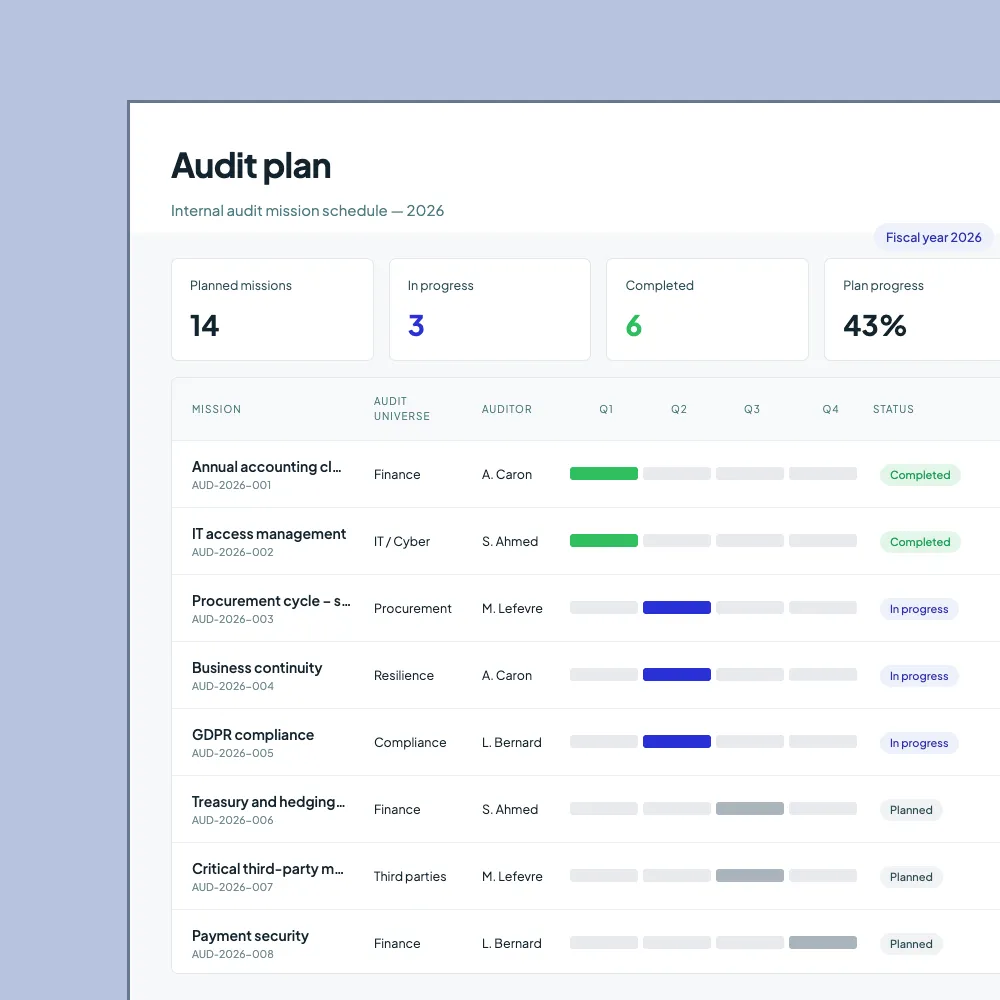
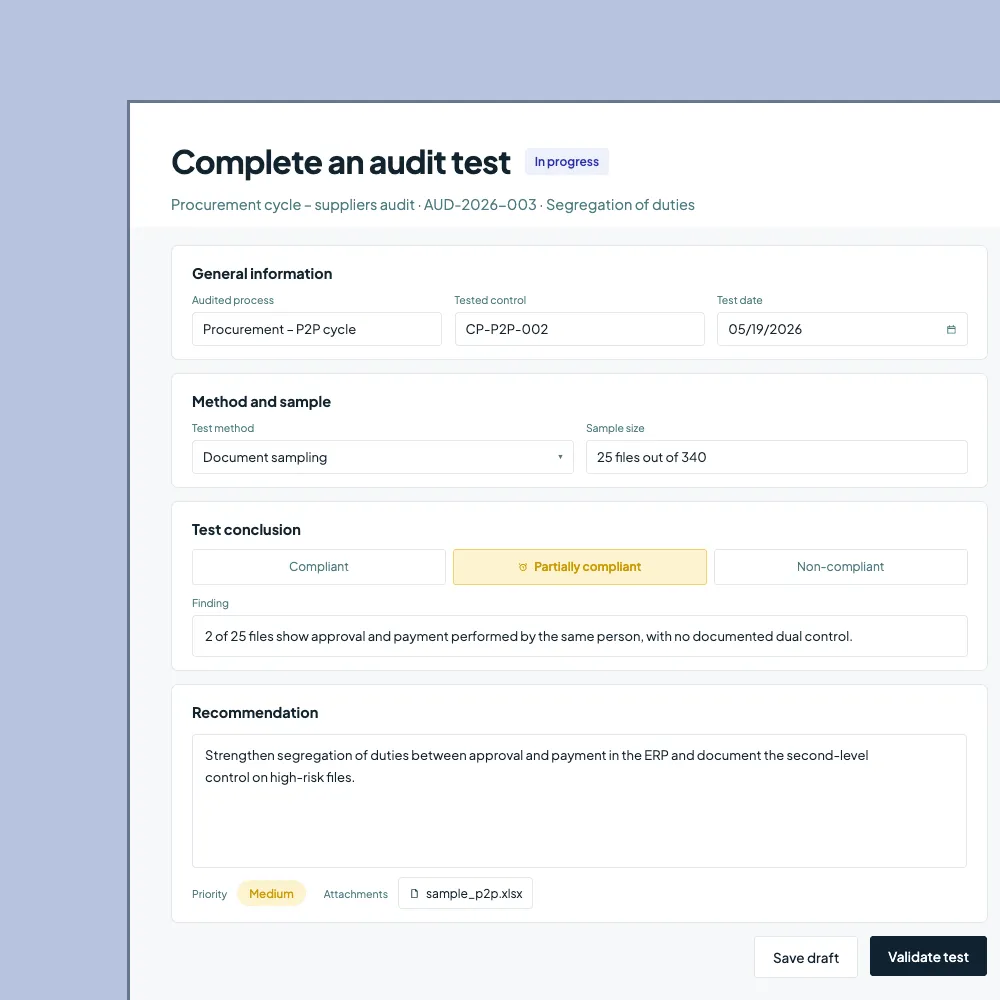
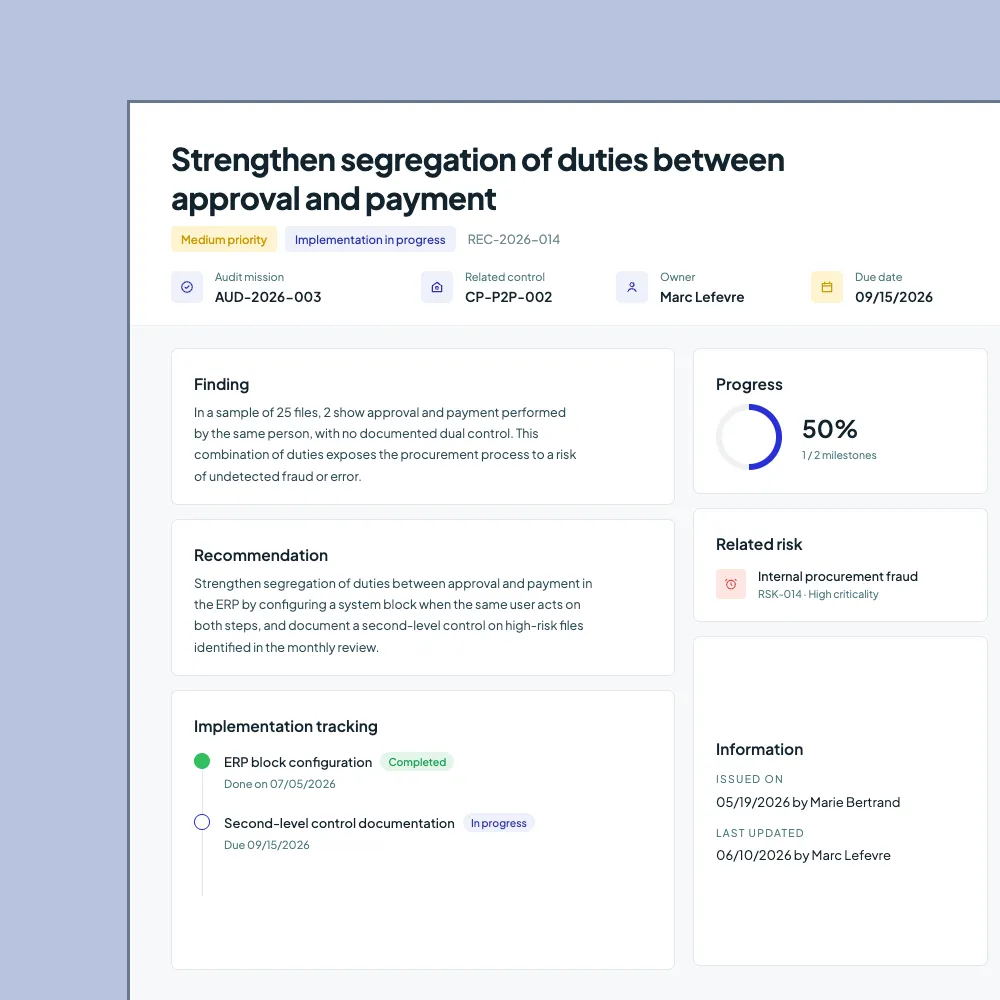
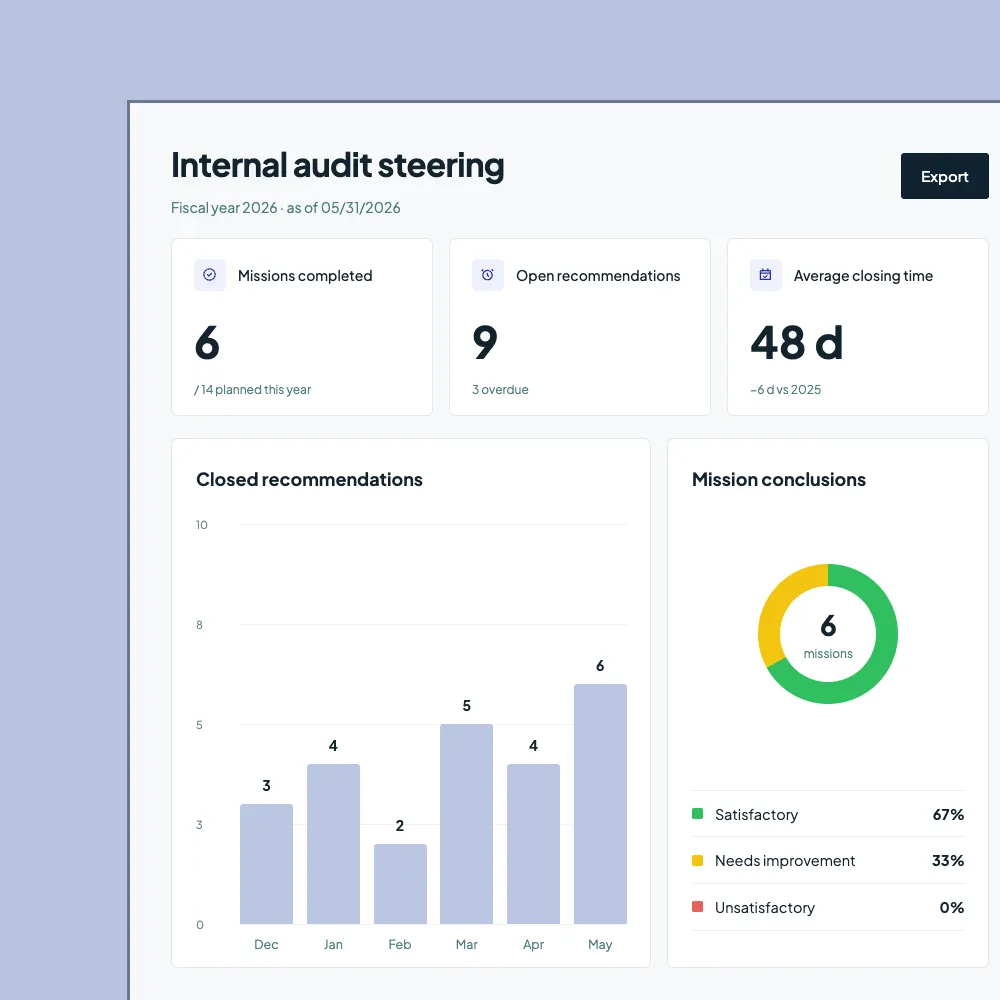
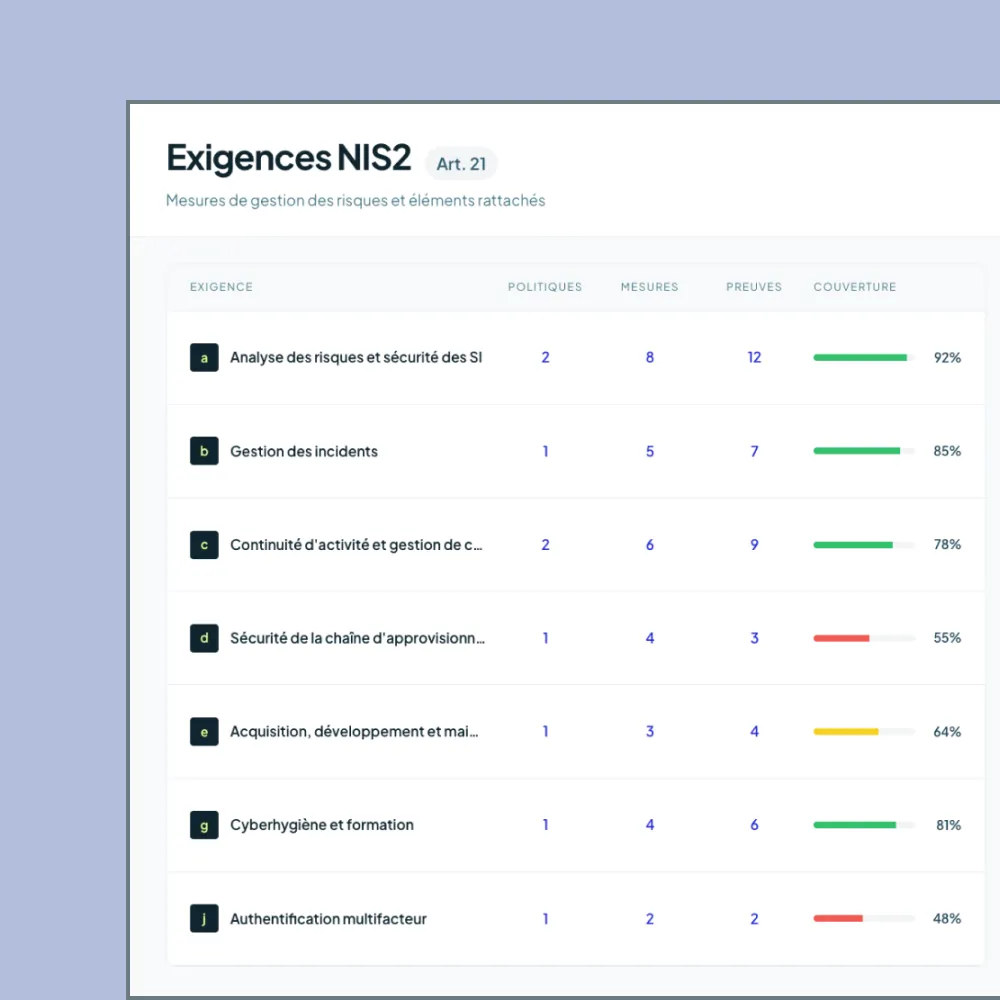
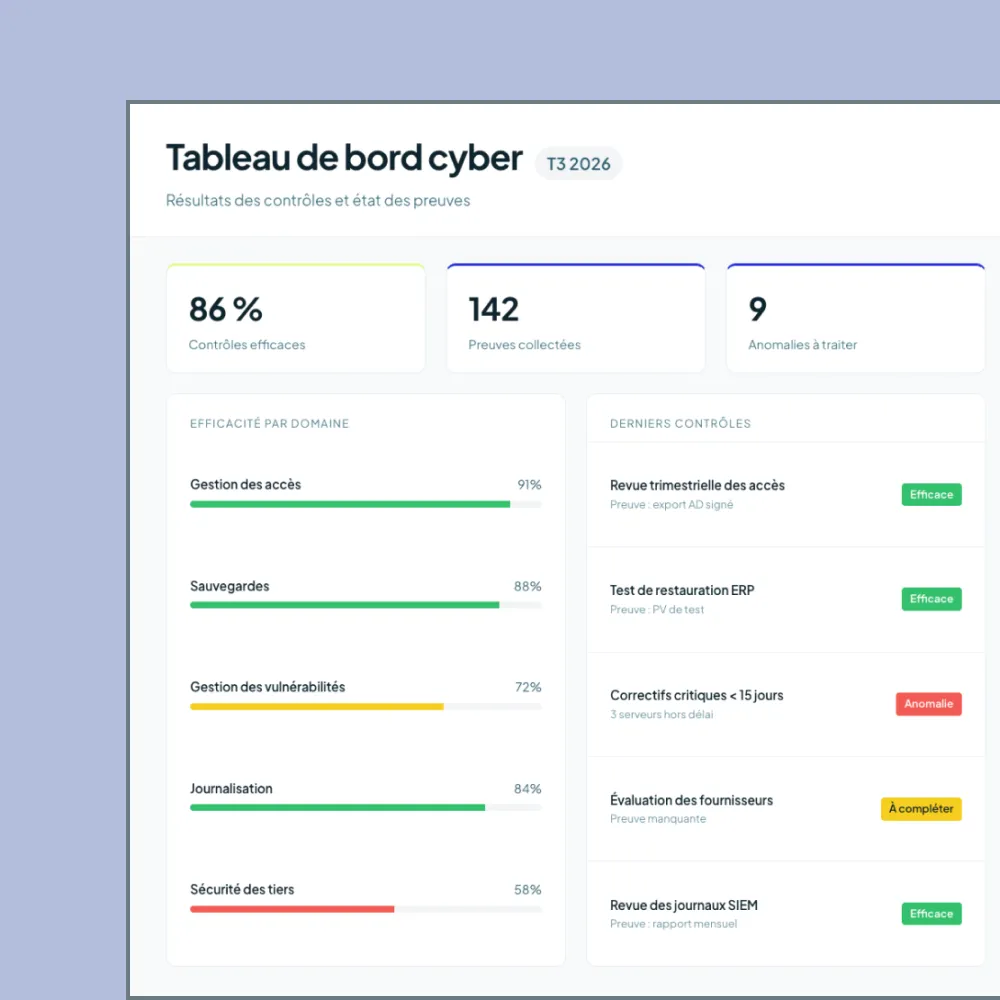
From your current framework to operational NIS2 management
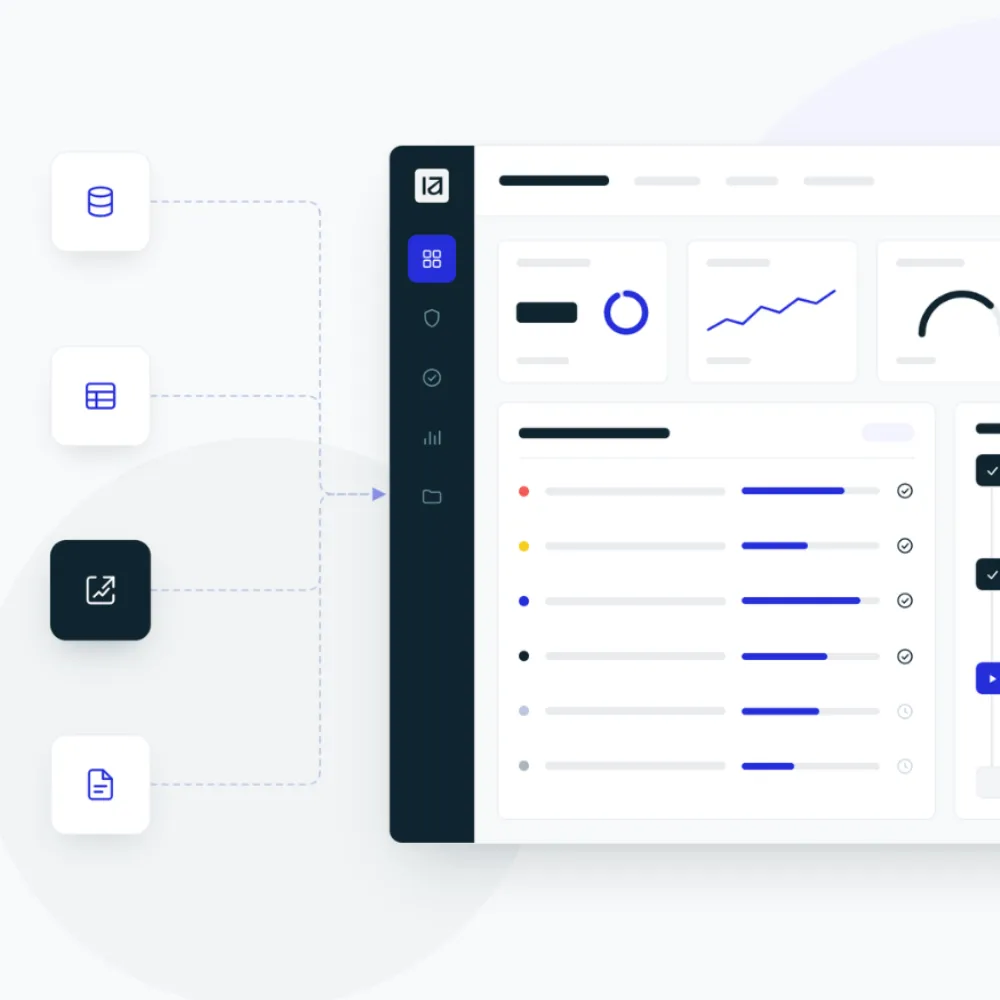
OTHER SOLUTIONS
Connect NIS2 to your wider governance framework
Cybersecurity cannot be managed in silos. Iskera connects NIS2 requirements to the frameworks that help manage cyber risks.
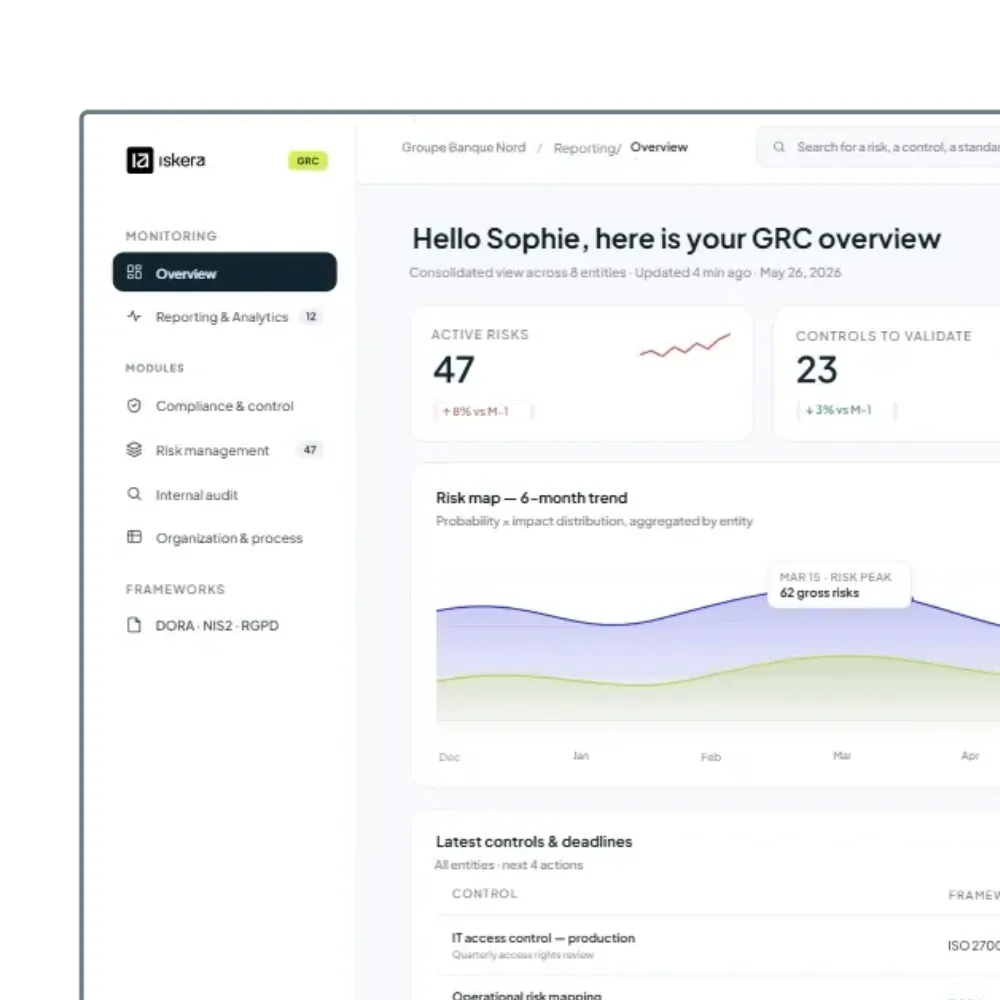
See how Iskera simplifies NIS2 management
See how to centralize requirements, map cyber risks, monitor incidents and suppliers, and manage compliance actions in one platform.
Latest resources
Frequently asked questions
NIS2 is EU Directive 2022/2555, which aims to establish a common high level of cybersecurity across the European Union. It strengthens requirements for cyber risk management, incidents, business continuity, supply chain security and governance.
NIS2 significantly broadens the scope of the first NIS Directive. It covers organizations in sectors including energy, transport, banking, healthcare, water, digital infrastructure, public administration, manufacturing, postal services, waste management, food production and certain digital services. Medium-sized and large organizations in these sectors are generally covered, subject to exceptions and specific rules.
Yes. Iskera lets you centralize suppliers and services, assess their criticality and risks, and track assessments, documents and action plans.
No. Iskera helps structure, document and manage NIS2 governance: risks, requirements, controls, assets, incidents, third parties, continuity and action plans. Technical functions such as intrusion detection, EDR, vulnerability scanning and network protection remain with specialist solutions.
Gaps from risk analysis, controls, audits, incidents or supplier assessments can be turned into actions in Iskera. Each action can have an owner, deadline, status and associated evidence.
For a significant incident, NIS2 requires an early warning within 24 hours of becoming aware, a notification within 72 hours and, in principle, a final report within one month. Notifications and decisions can be documented in Iskera.
The directive covers risk analysis, incident management, business continuity, supply chain security, vulnerability management, assessment of the effectiveness of measures, awareness, cryptography, access and asset management, and stronger authentication.