DORA
Structure your DORA framework in one platform
Centralize ICT risks, incidents, critical providers, controls, continuity plans and remediation actions.
Iskera connects these elements to help you monitor compliance and operational resilience over time.
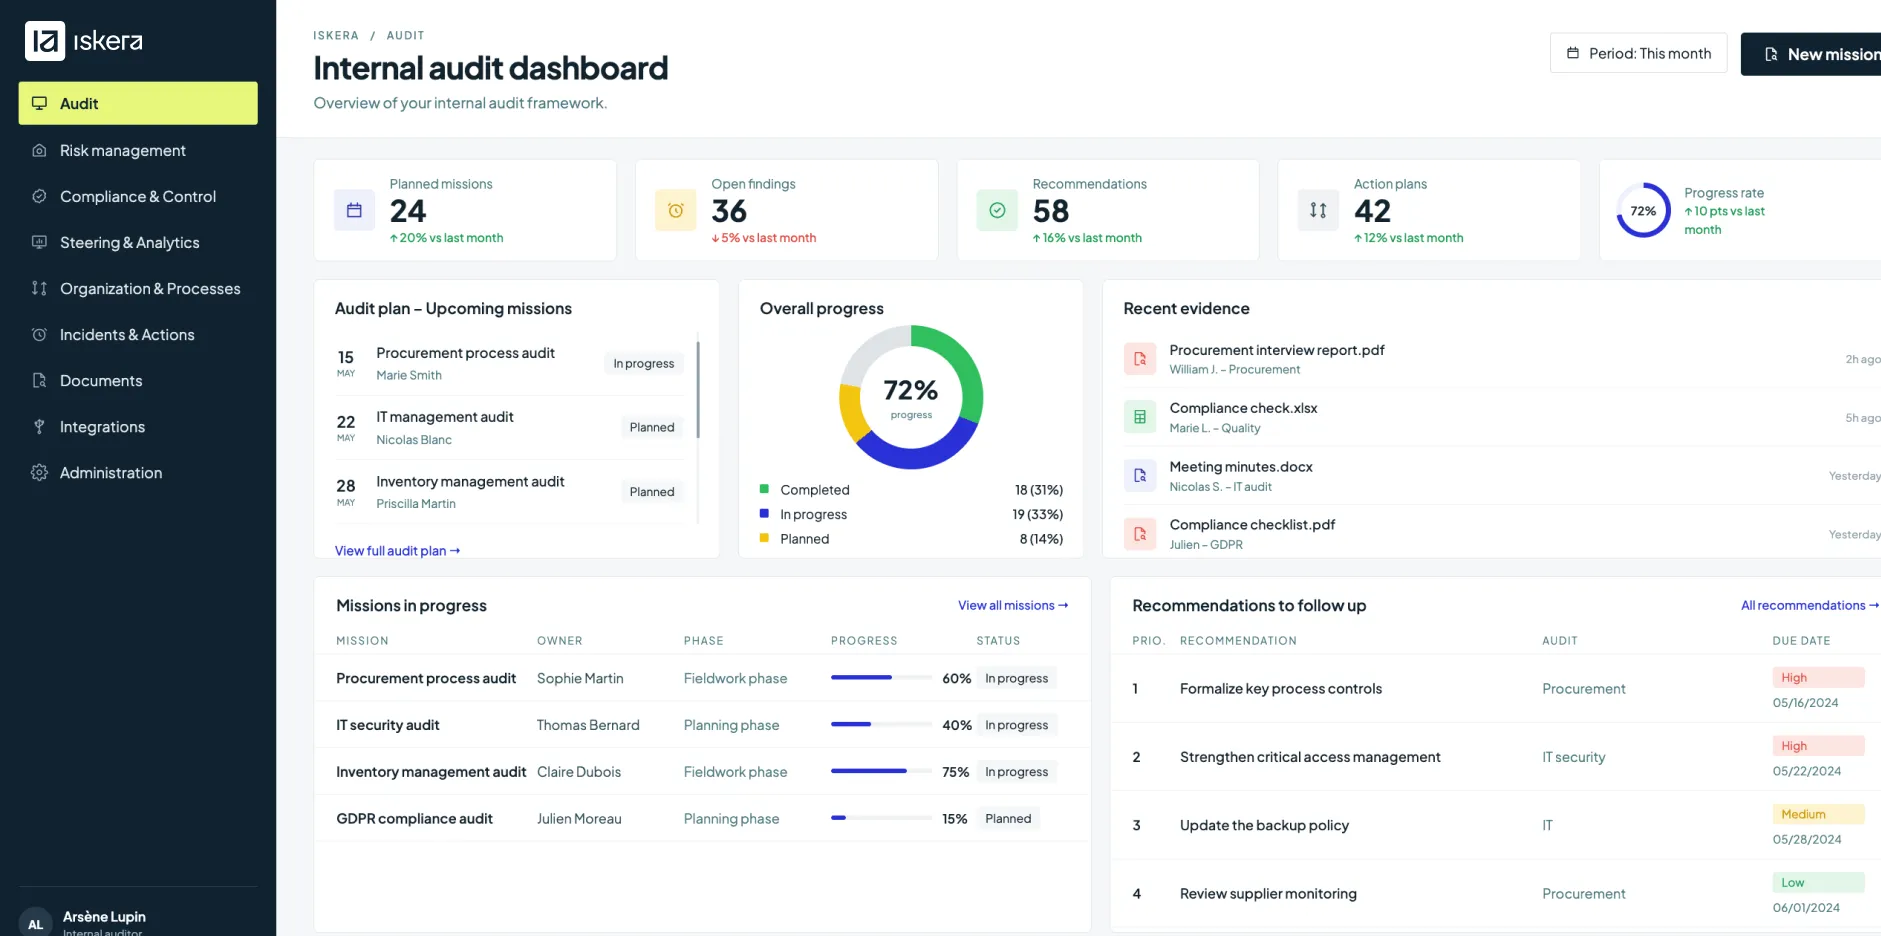
Turn DORA requirements into a framework you can manage
DORA strengthens digital operational resilience requirements for financial institutions. ICT risks, incidents, continuity, resilience testing and dependencies on technology providers must form part of a structured, documented framework monitored over time.
Iskera brings these elements together. Link every requirement to its risks, assets, providers, controls, incidents, evidence and action plans to gain a clear view of your level of control.
Structure your ICT risk management framework
Centralize digital risks and link them to the activities, assets, processes and critical functions they may affect. Document mitigation measures and monitor your exposure over time.
- ICT risk mapping
- Critical assets and functions
- Controls and mitigation measures
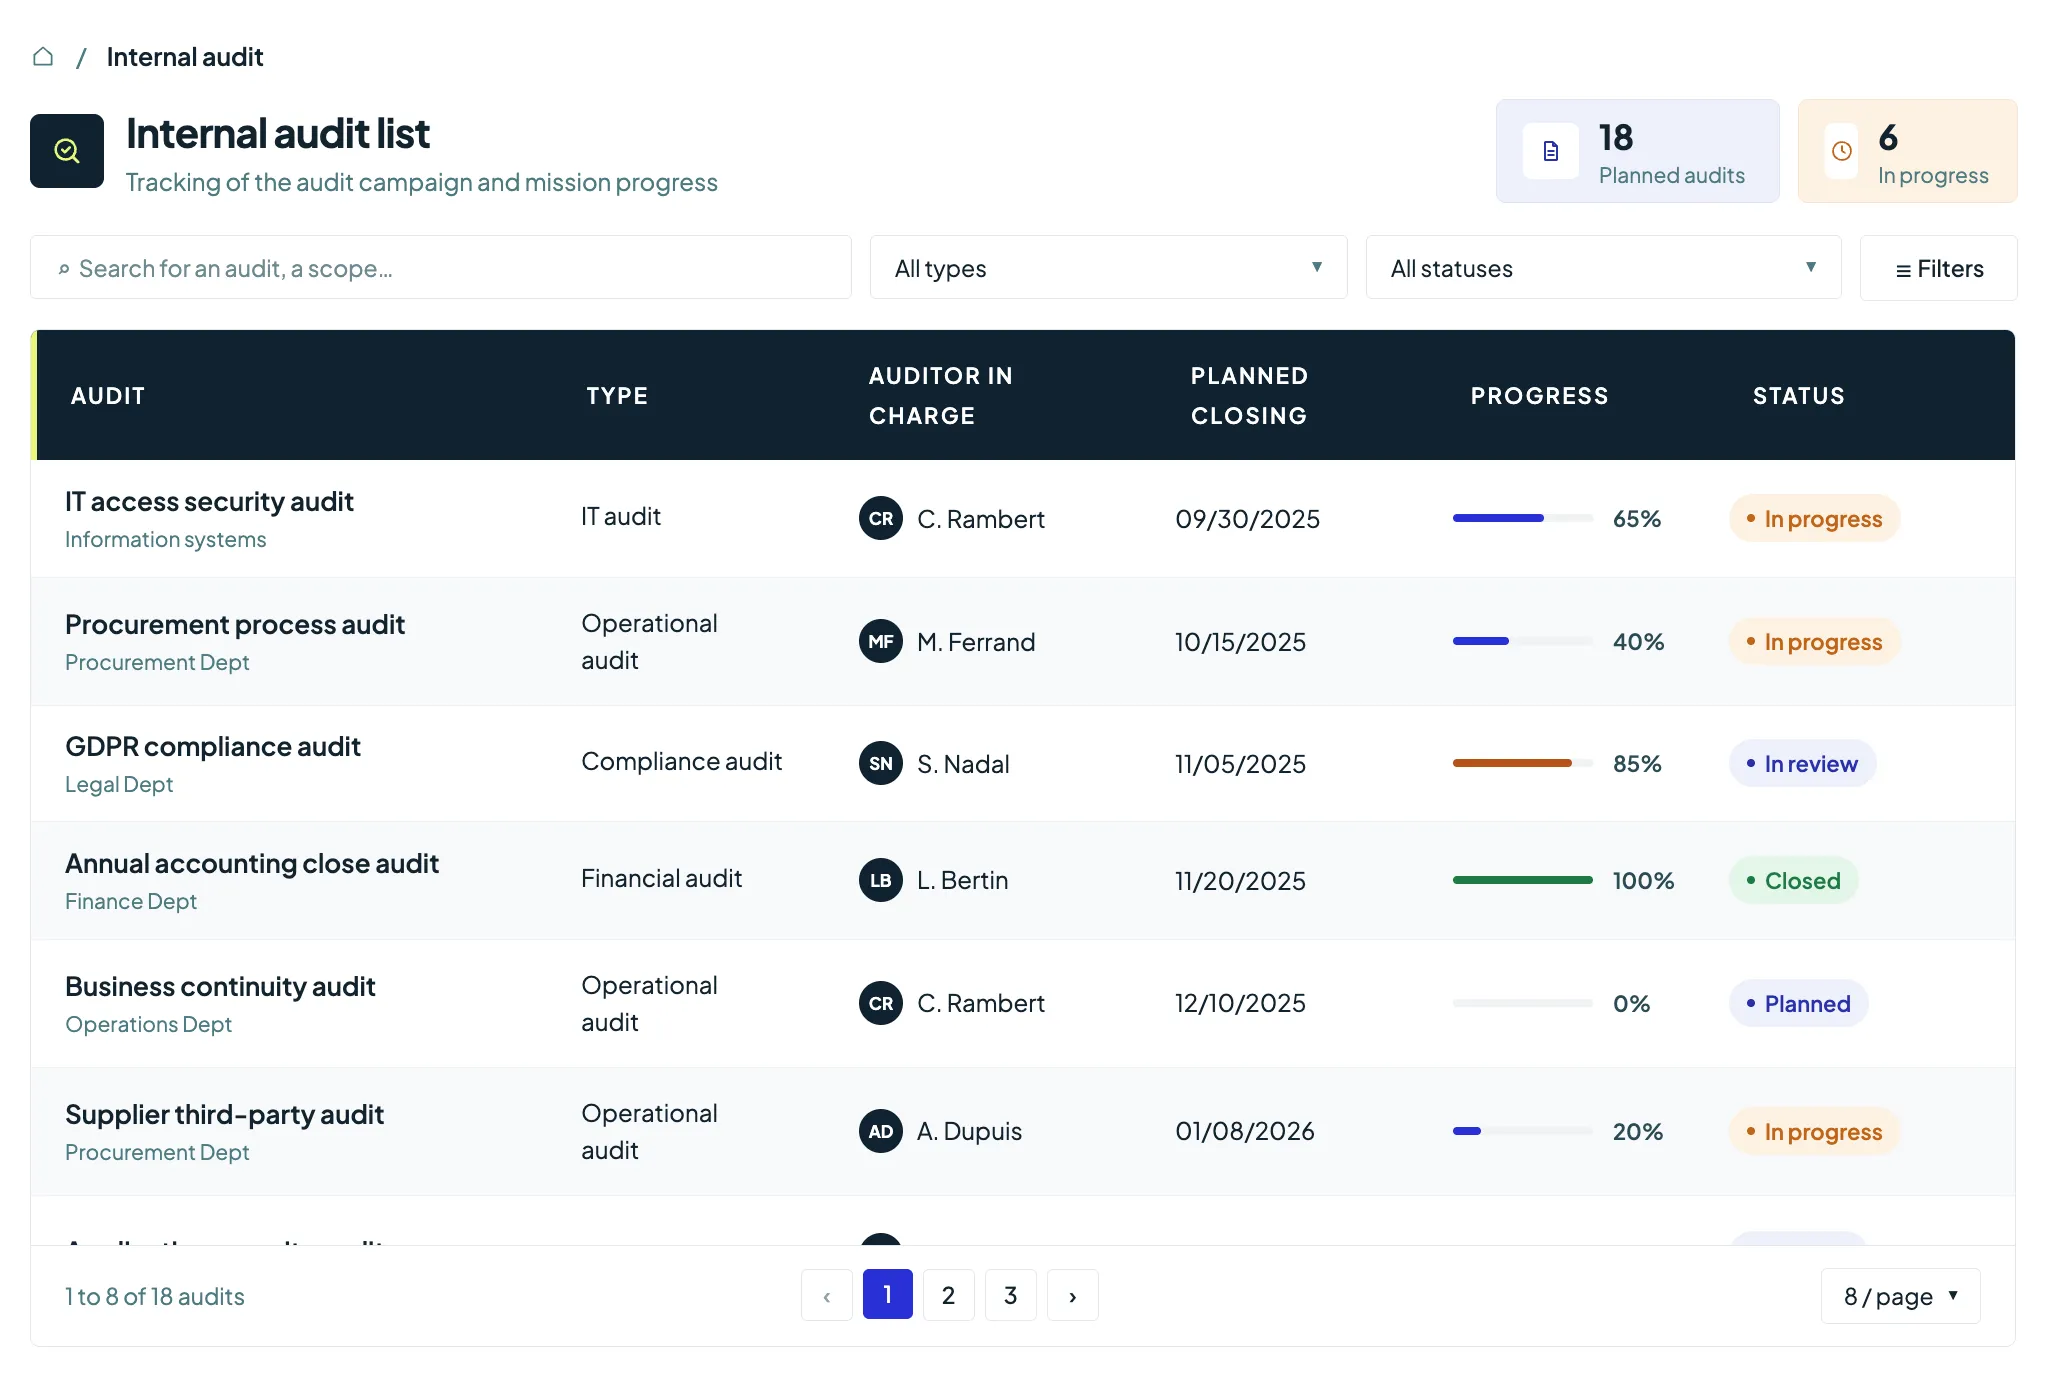
Manage incidents and strengthen resilience
Centralize ICT incidents, document their impacts and track their resolution through to closure.
Link each event to relevant risks and corrective actions to learn from incidents and strengthen resilience.
- Incident reporting and classification
- Response and remediation plans
- History and traceability
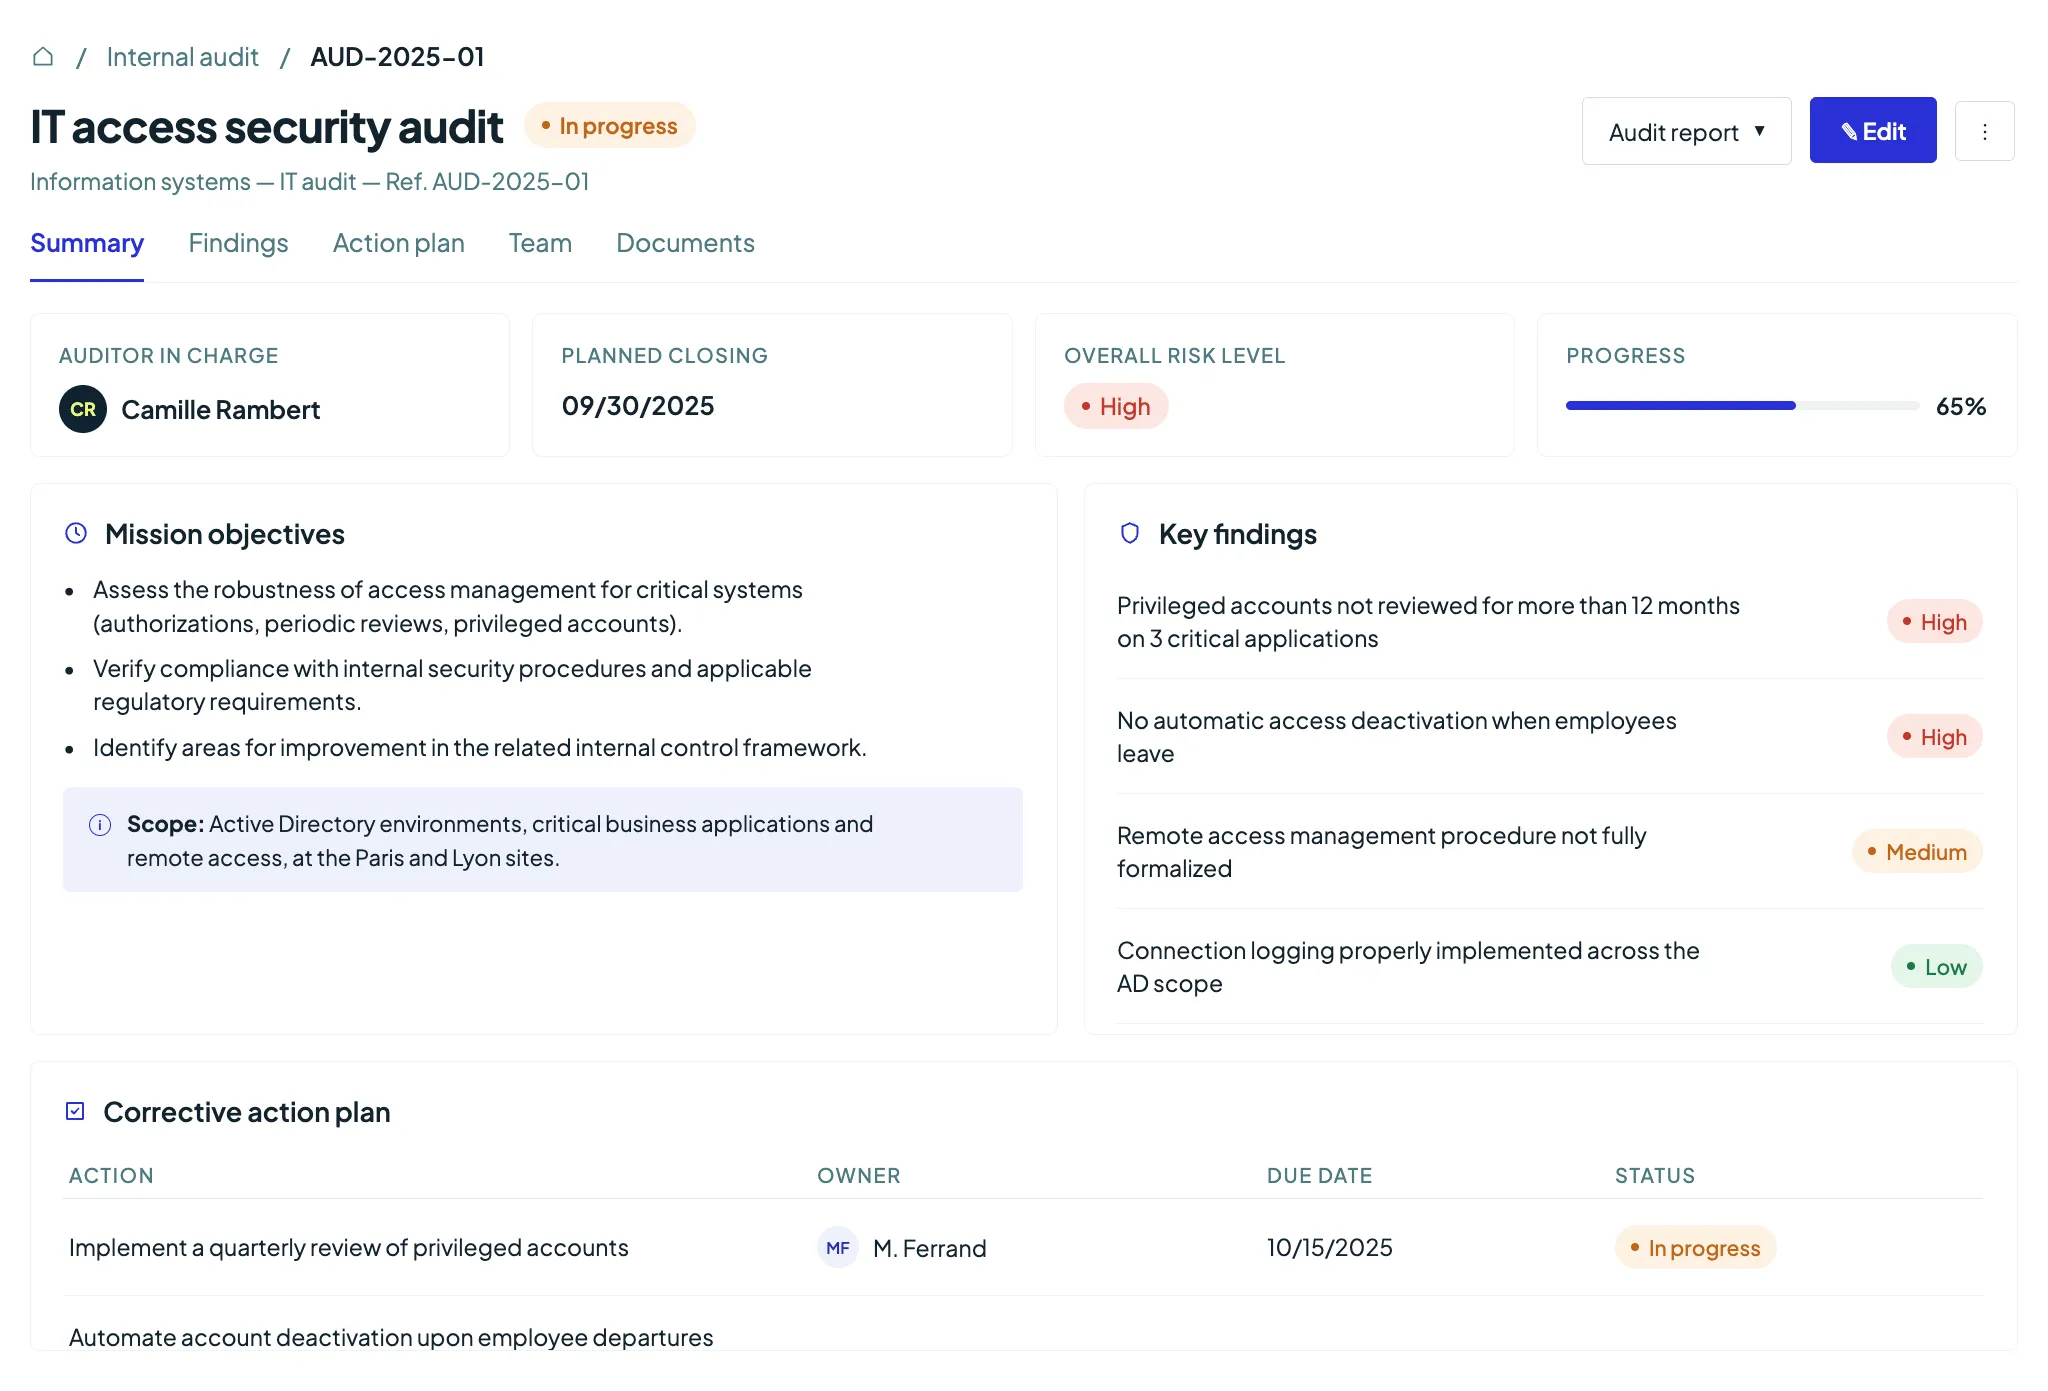
Manage your critical ICT providers
Identify providers your critical functions depend on, assess their risks and centralize the information needed for oversight.
Structure your provider register and maintain an up-to-date view of technology dependencies.
- ICT provider register and contract monitoring
- Identification of critical third parties
- Supplier risk assessment
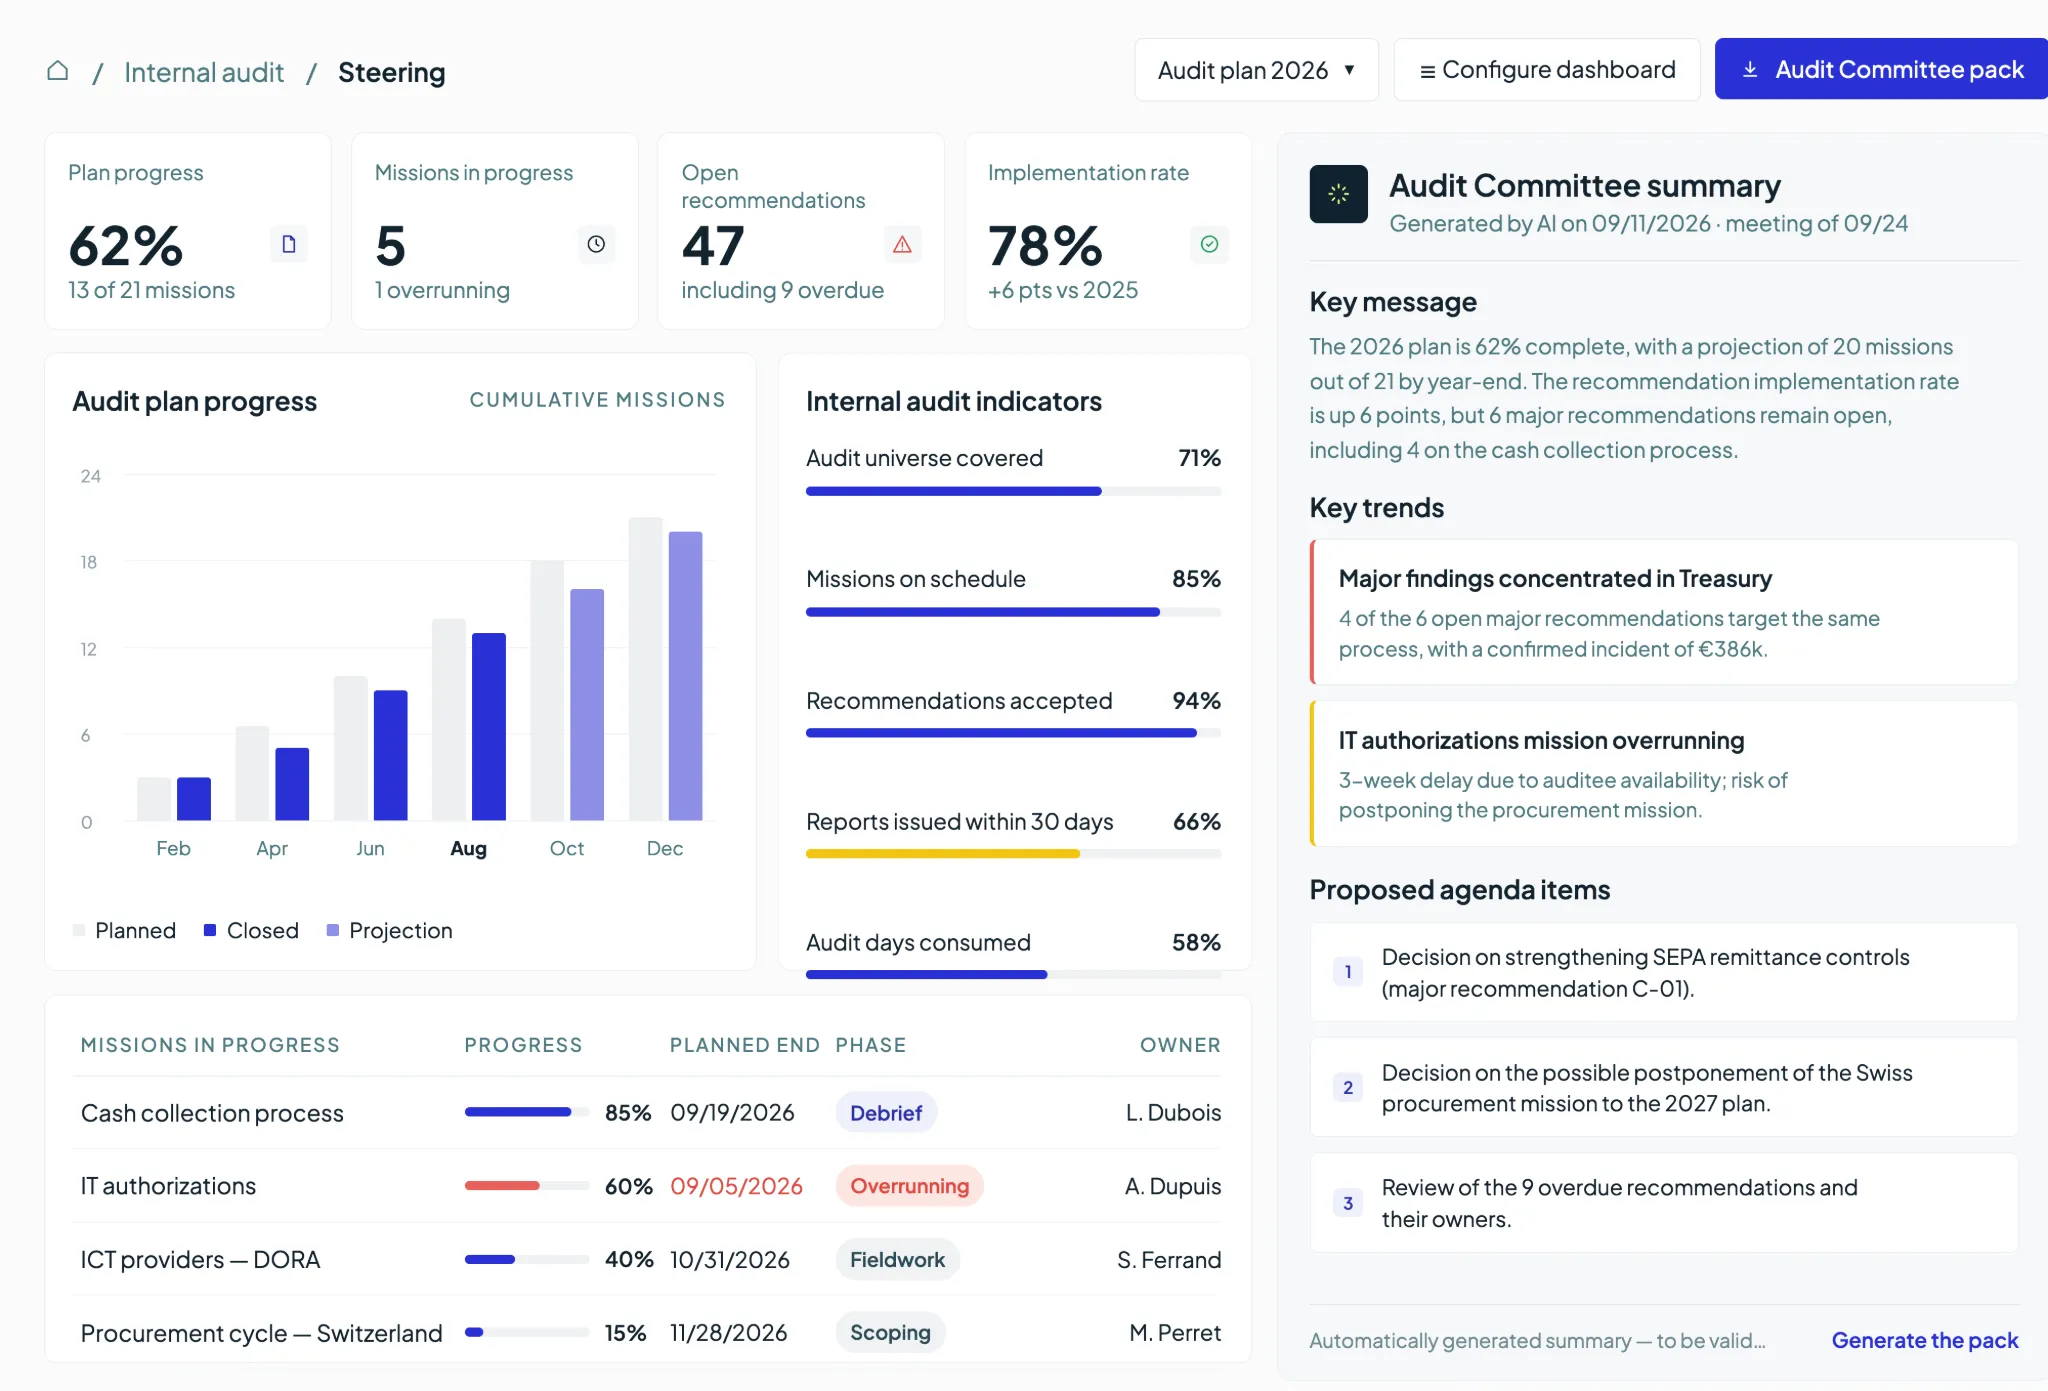
Monitor DORA compliance over time
Bring requirements, controls, tests, incidents, risks and action plans together in shared dashboards.
Identify priority gaps, track remediation and simplify your audits and governance reporting.
- Resilience test monitoring
- Action plans and remediation
- Dashboards and reporting
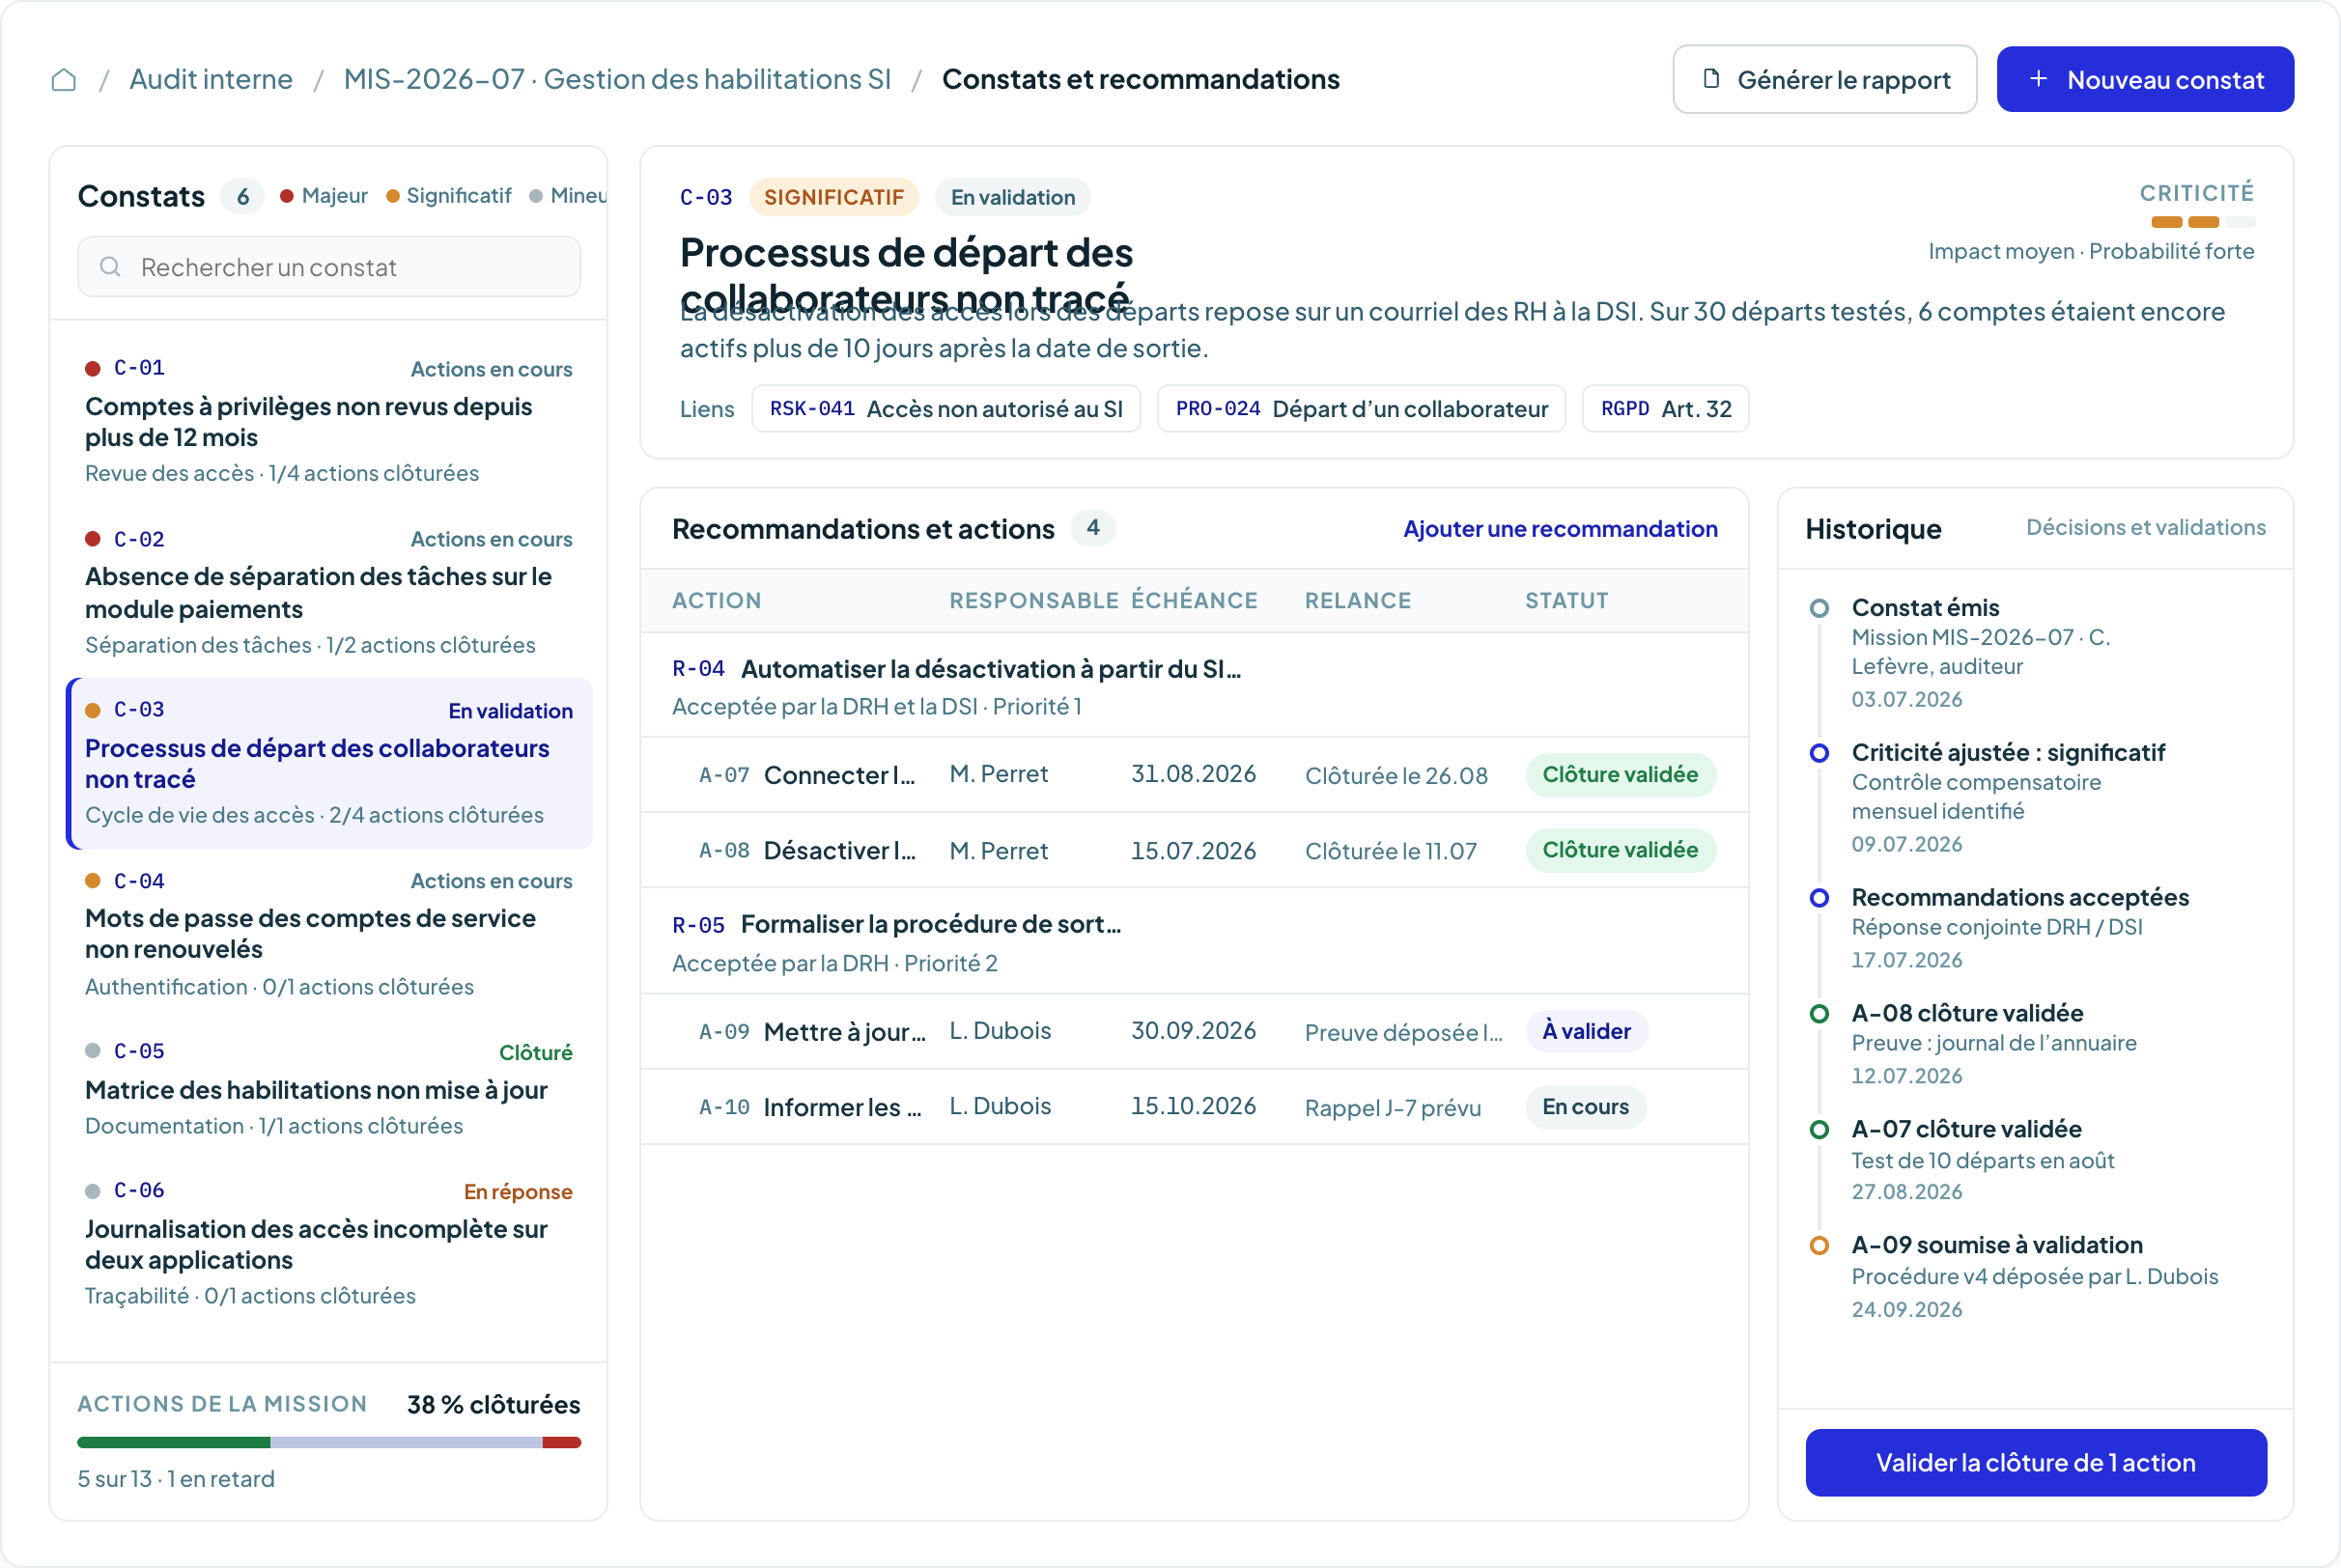
A DORA framework that is clearer, more traceable and easier to manage

100%
of your risks, incidents, third parties, controls and actions brought together in one environment
- 01
Compliance that's easier to demonstrate
Link every DORA requirement to relevant frameworks, controls, documents and evidence to retrieve the information you need quickly.
- 02
A clear view of your ICT risks
Connect risks, assets, processes and critical functions to identify areas of vulnerability requiring attention.
- 03
Better oversight of critical third parties
Centralize ICT provider information and quickly identify dependencies that could affect essential activities.
- 04
Priority actions under control
Bring together gaps from incidents, assessments, audits and resilience tests and track their resolution through to closure.
Build your DORA framework in 3 steps
01
Map your framework
Import existing requirements, ICT risks, assets, critical functions, providers and controls.
Connect them to build a consistent overview of your DORA framework.
02
Assess your level of control
Analyze risks, document controls, identify gaps and centralize findings from audits, incidents and resilience tests.
03
Manage remediation
Prioritize action plans, assign responsibilities, track deadlines and use up-to-date dashboards for operational teams and governance bodies.
Manage your DORA framework effectively
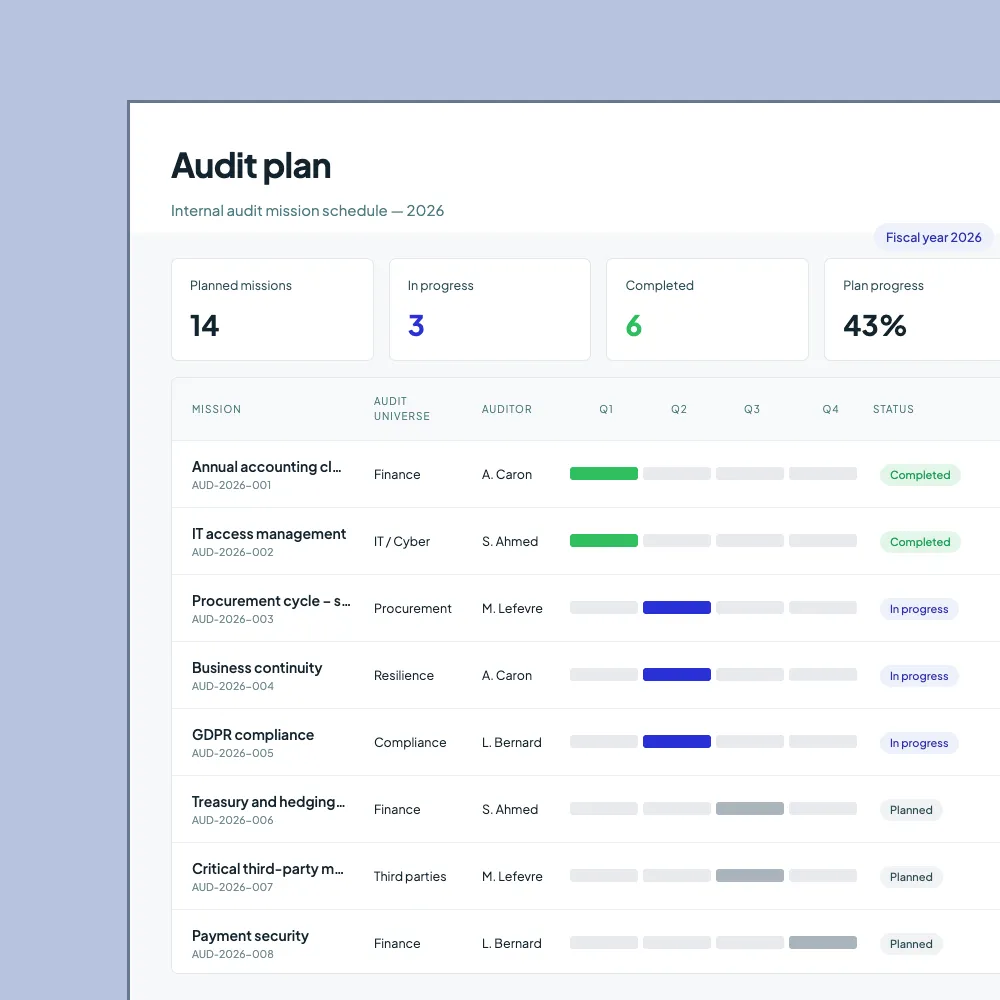
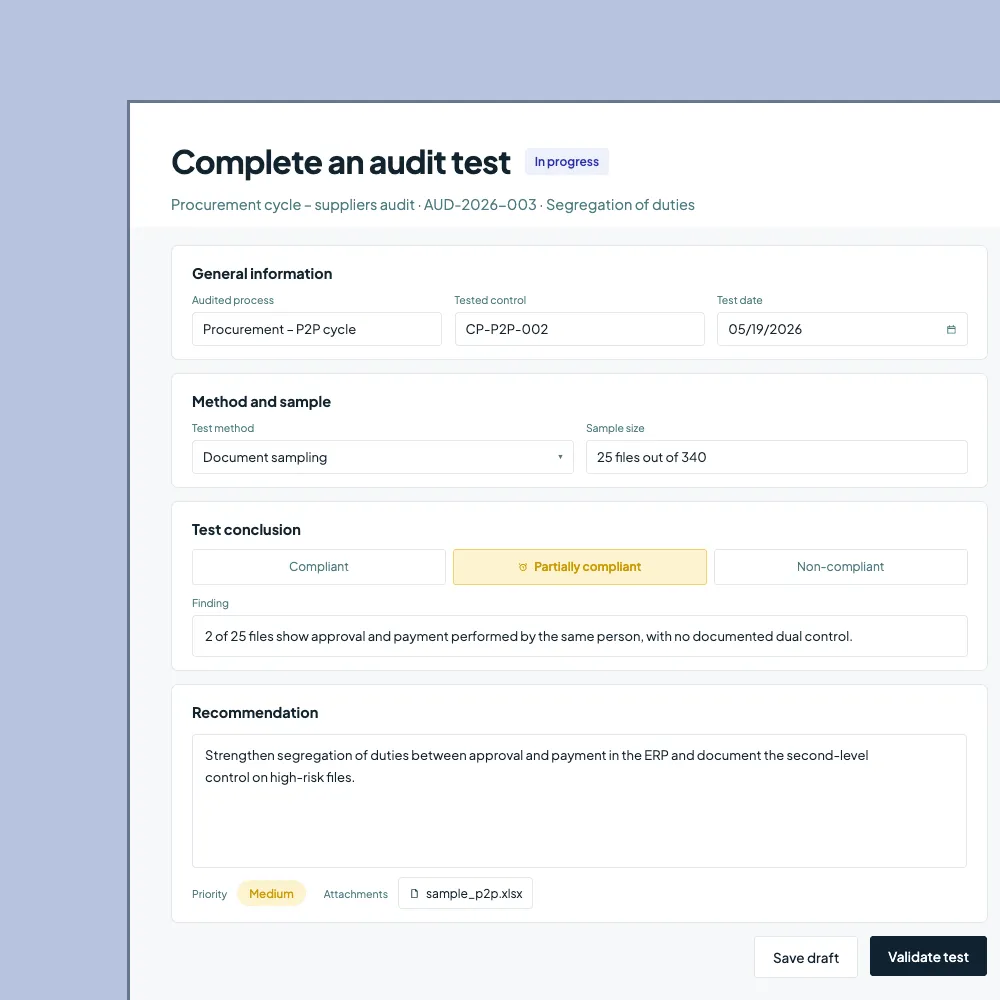
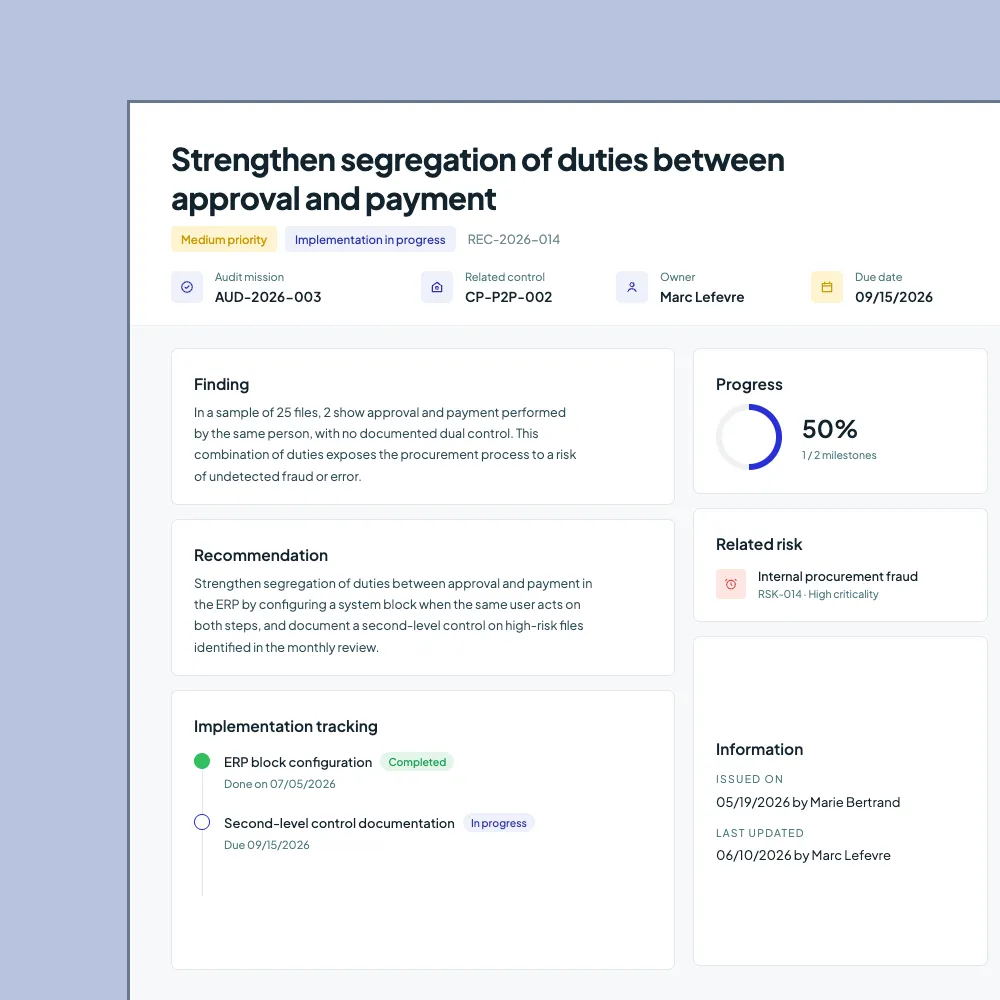
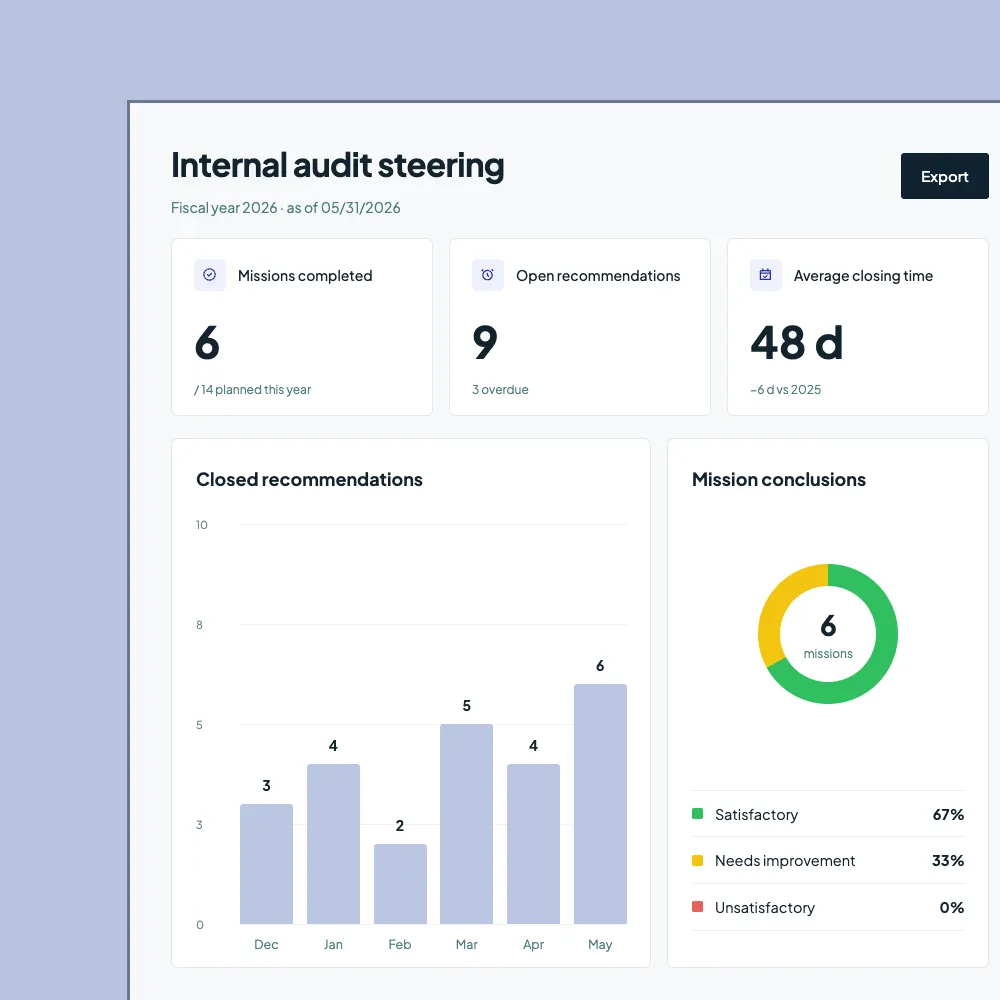
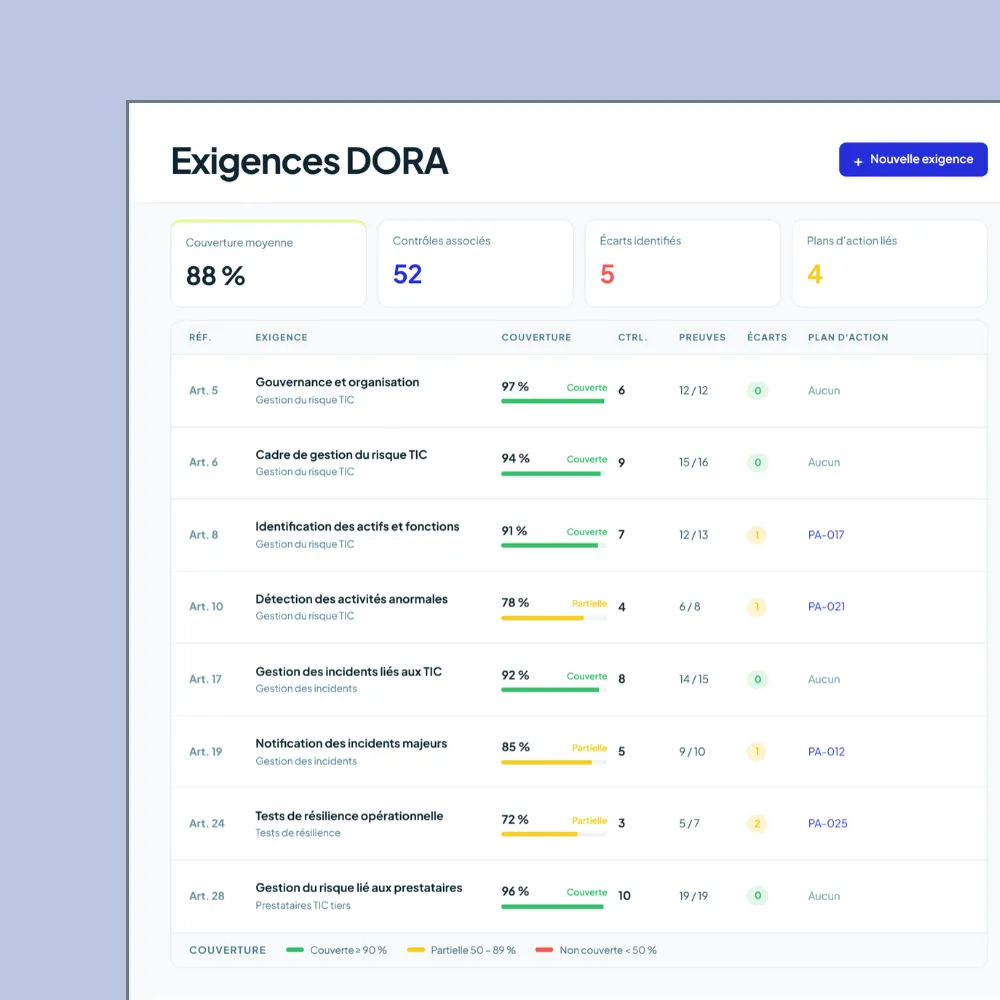
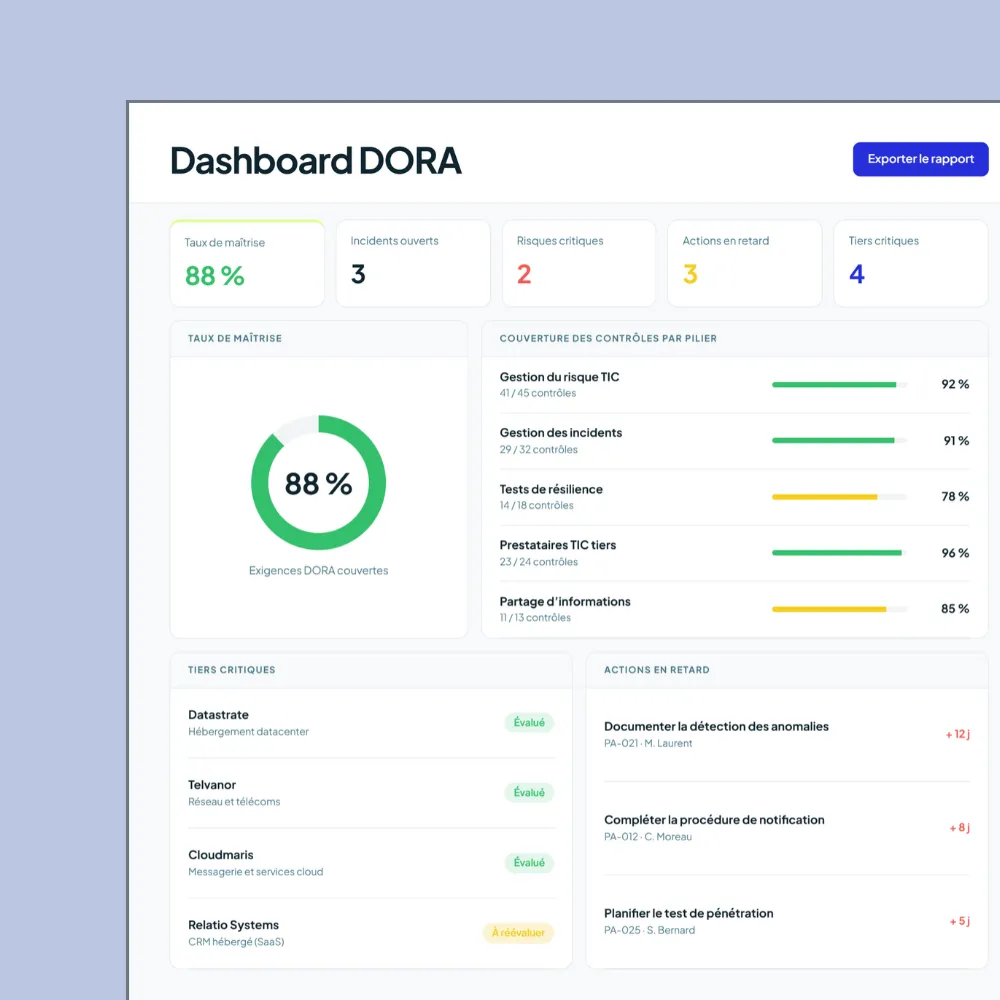
From your current framework to fully operational DORA management
OTHER SOLUTIONS
Connect DORA to your wider governance framework
Operational resilience cannot be managed in silos. Iskera connects your DORA requirements to the frameworks that support compliance.
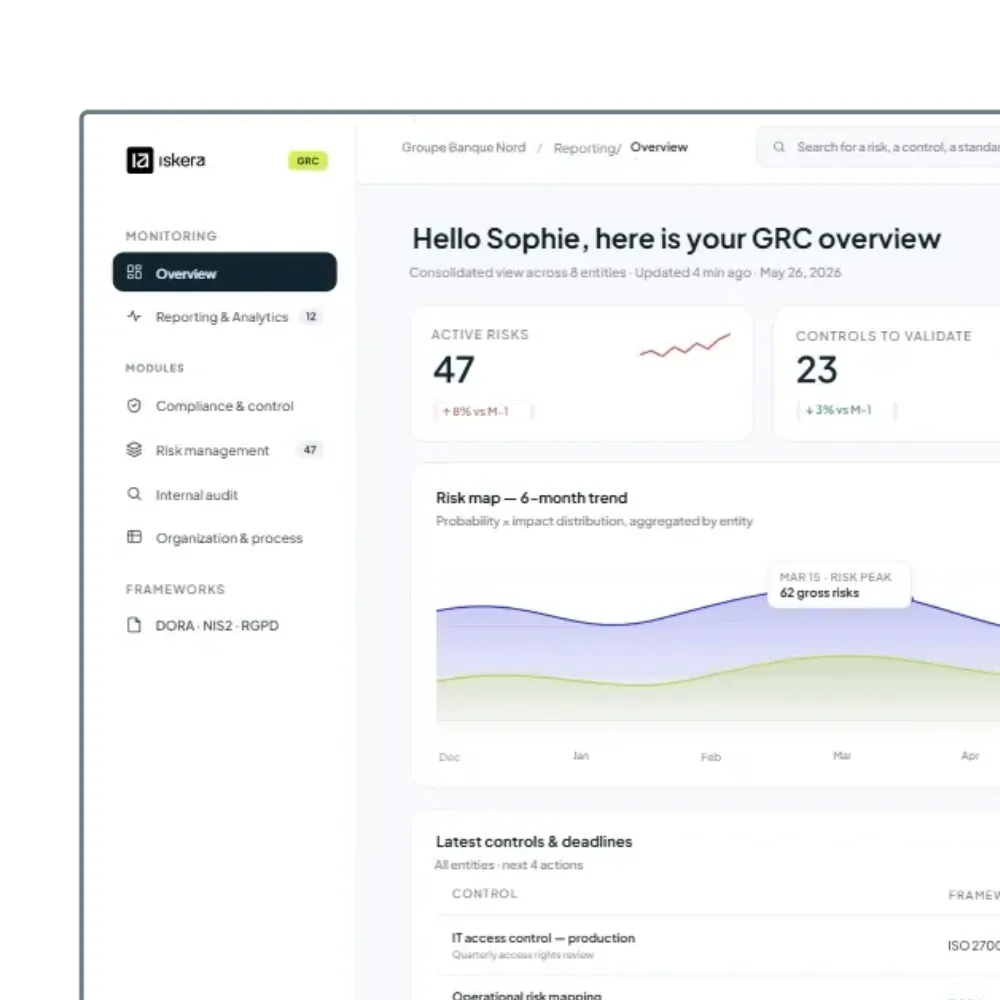
See Iskera in action
See how to centralize requirements, map ICT risks, monitor incidents and critical providers, and manage compliance actions in one platform.
Latest resources
Frequently asked questions
DORA, the Digital Operational Resilience Act, is the EU regulation on digital operational resilience in the financial sector. It sets common requirements covering ICT risk management, incidents, resilience testing and technology third-party risks.
DORA applies to many categories of European financial entities, including credit institutions, insurance and reinsurance undertakings, investment firms, payment institutions and other financial entities, as well as ICT service providers supporting them in certain respects.
Yes. Iskera helps centralize ICT providers and services, assess their criticality and risks, track assessments, contracts, documents and action plans, and structure information needed for oversight.
Iskera helps plan, document and manage resilience testing, centralize results and track remediation actions.
Technical tests themselves, such as certain vulnerability assessments and penetration tests, remain the responsibility of specialized tools and experts appointed by your organization.
Gaps from audits, controls, incidents, supplier assessments or tests can be turned into actions in Iskera.
Each action has an owner, deadline, status and associated evidence.
DORA requires a register of information on contractual arrangements with ICT service providers.
Harmonized templates have been defined to structure this information. Iskera can serve as a central repository for maintaining the data needed for monitoring.