ISO 27001
Manage your information security management system in one platform
Centralize information security risks, assets, requirements, security controls, incidents, audits and action plans.
Iskera makes your ISMS easier to manage, automates follow-up and uses AI to analyze information, find evidence and prepare for ISO 27001 audits.
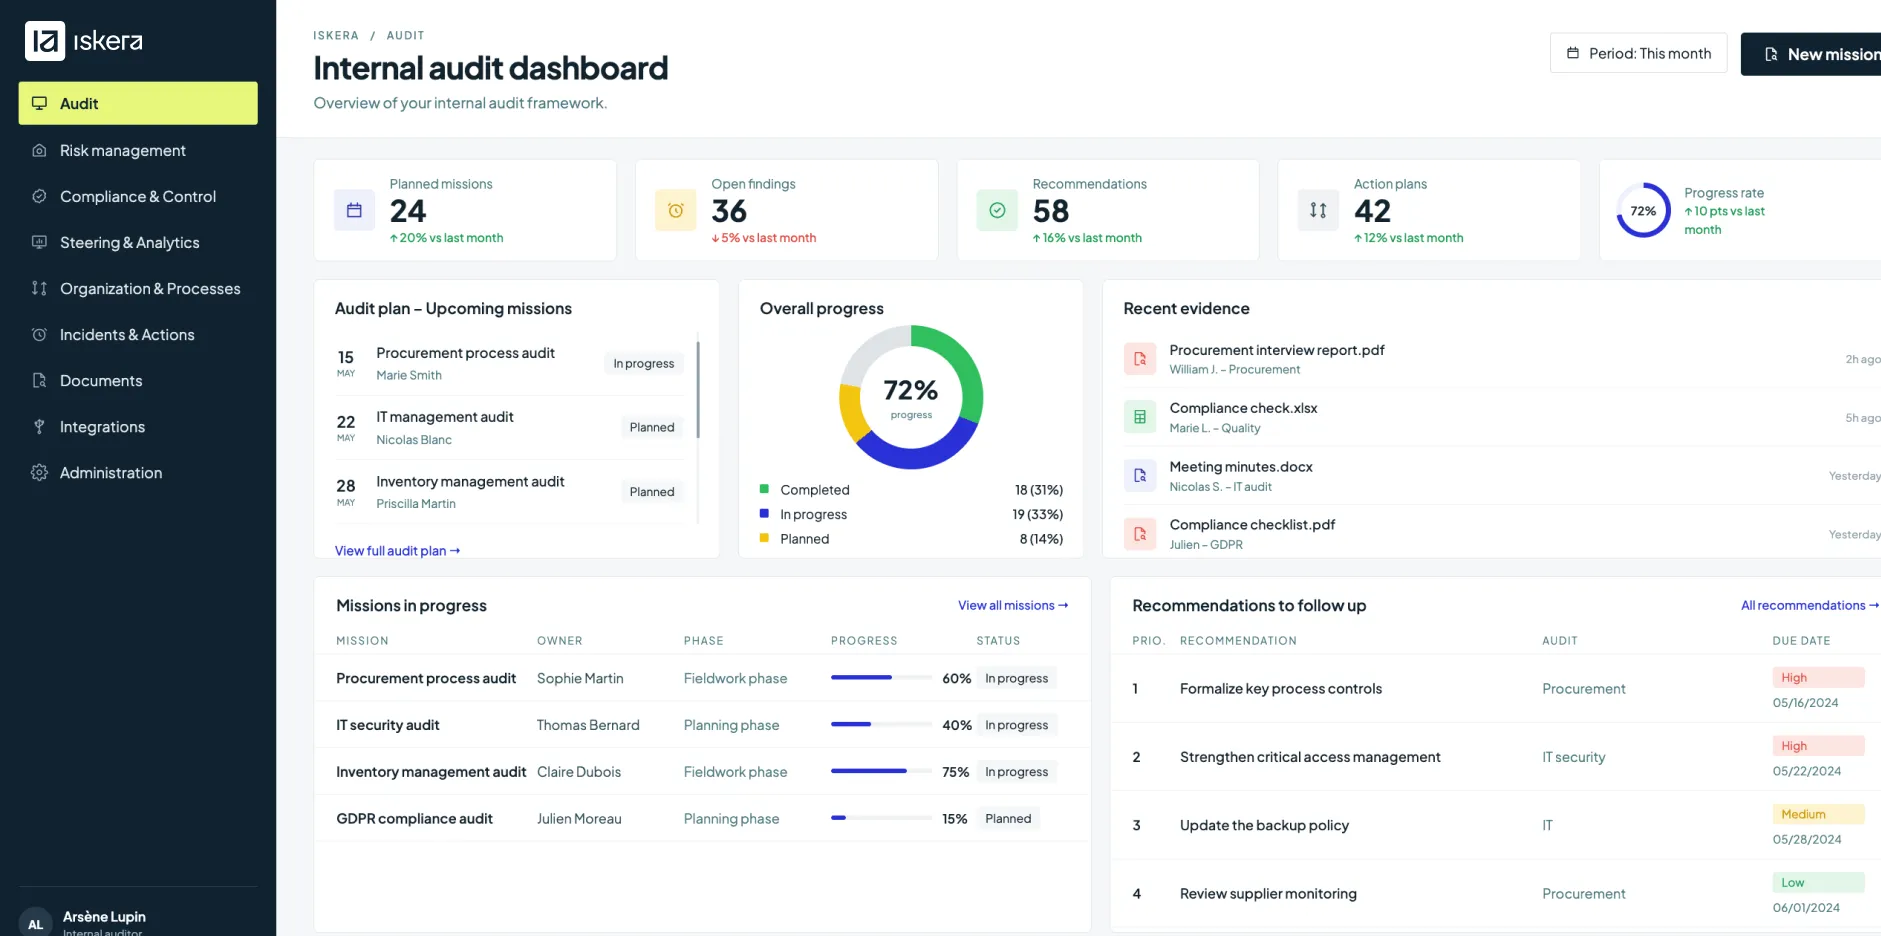
Make information security part of everyday operations
ISO/IEC 27001 sets the requirements for establishing, maintaining and continually improving an information security management system (ISMS). Managing it involves assets, risks, security controls, requirements, responsibilities, incidents, KPIs, audits and action plans. Iskera brings them together in one place, improving oversight, updates and traceability. Automation and AI help teams focus on security analysis and decision-making.
Automation and AI help teams spend more time analyzing risks and managing information security.
Structure your information security management system
Centralize ISMS processes, assets, responsibilities, policies and documentation. Connect assets with their risks, security controls, requirements and owners for a consistent view of your information security environment.
- Centralized assets and processes
- Clearly defined responsibilities
- Connected risks and security controls
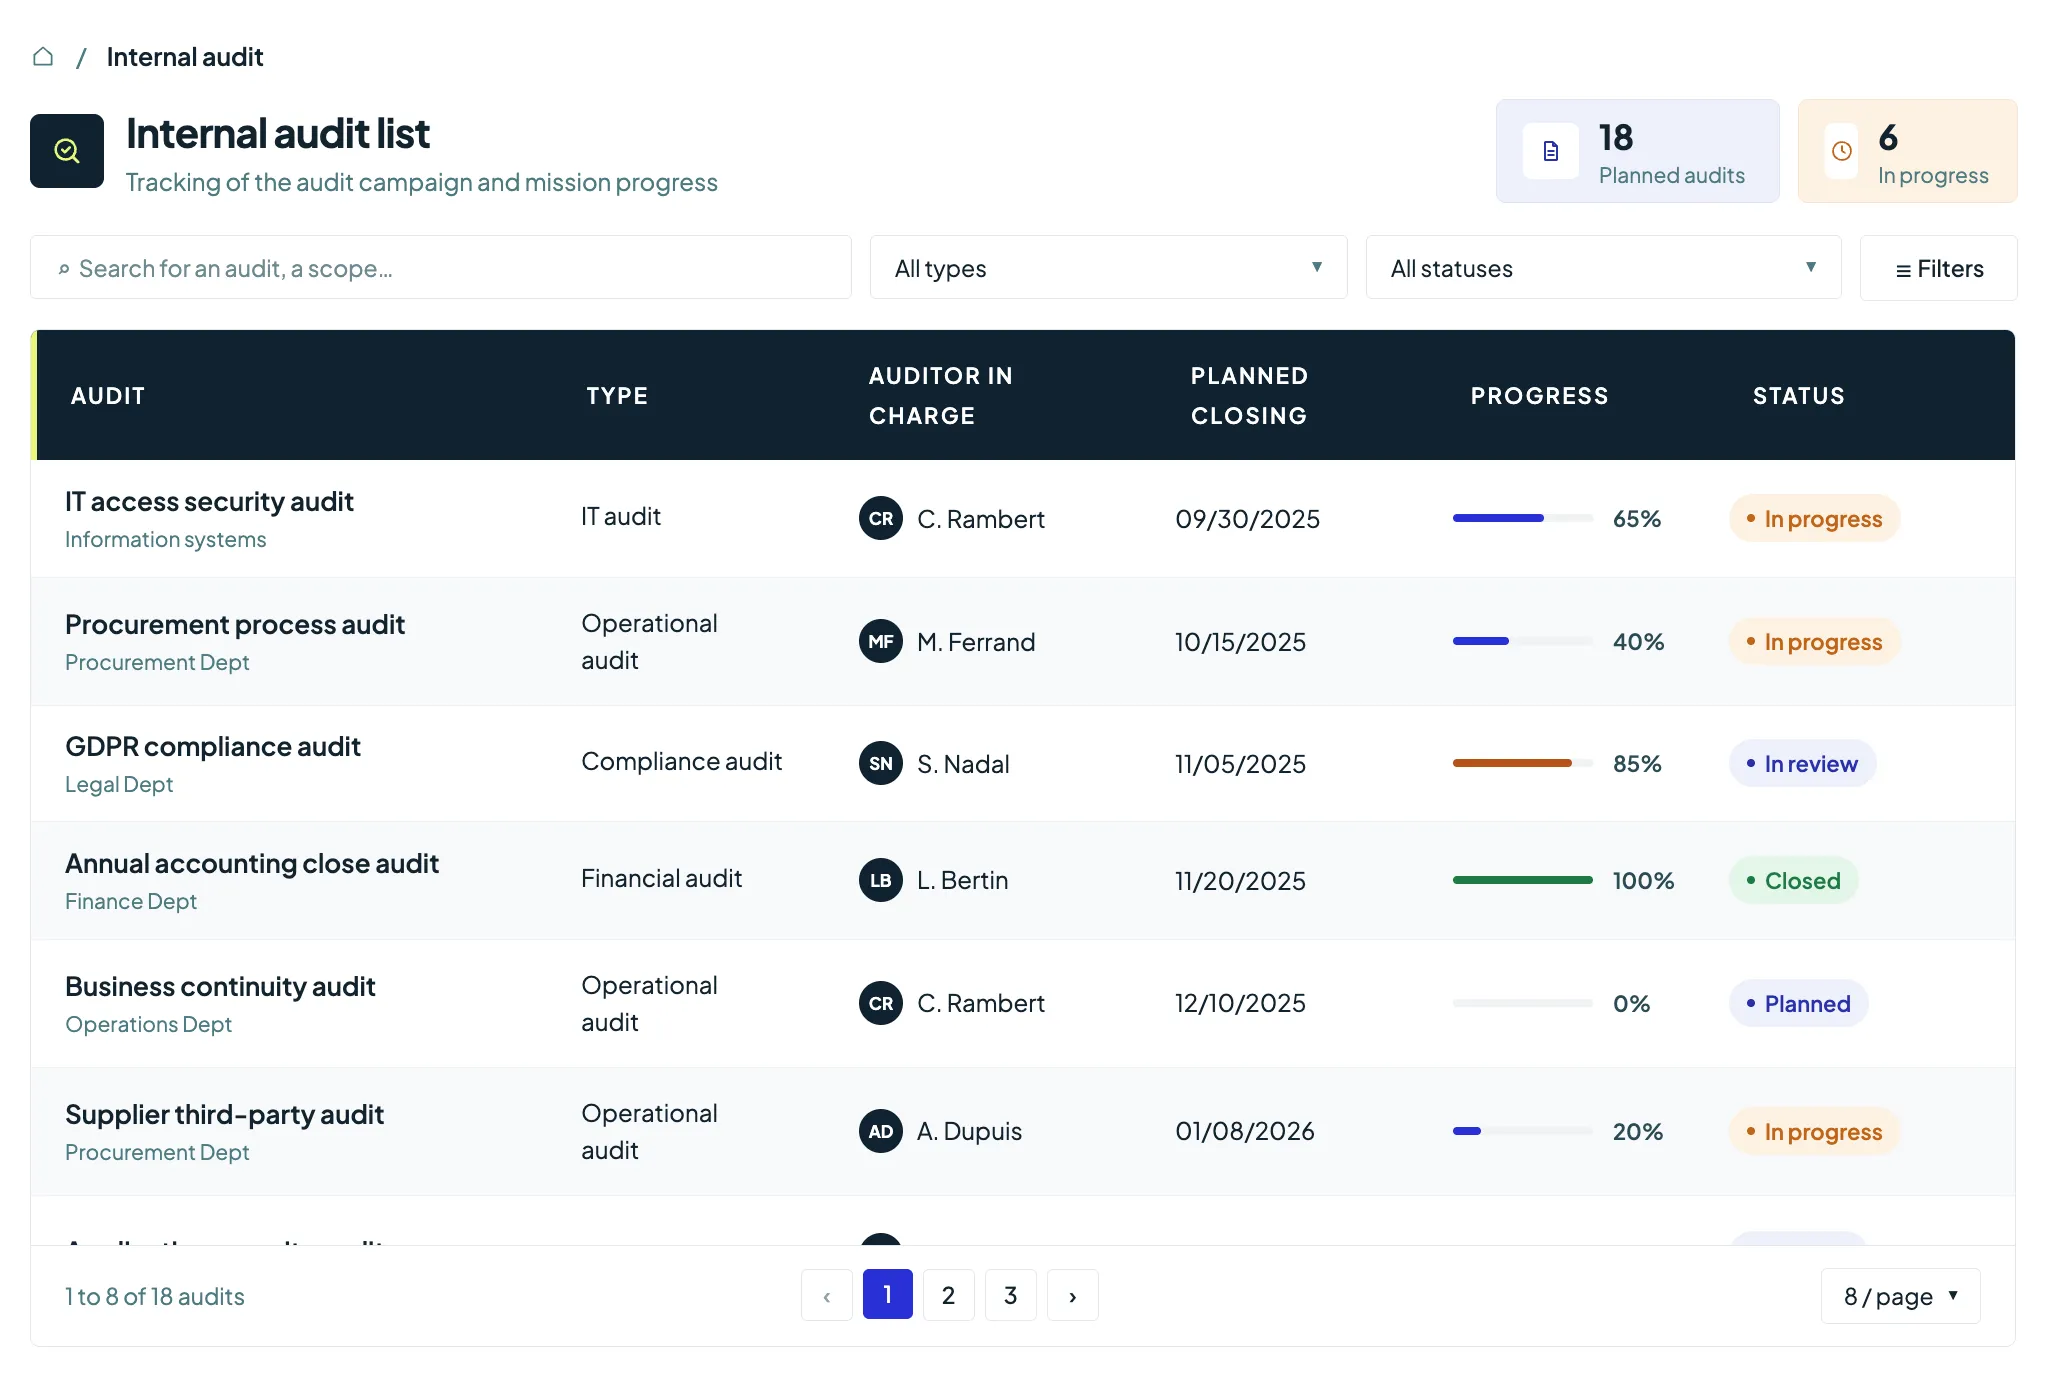
Manage information security risks
Identify risks to the confidentiality, integrity and availability of information and assess their severity. Link each risk to affected assets, existing controls, owners and risk treatment plans. Consolidate information to prioritize risks and track changes.
Link risks to affected assets, existing controls, owners and treatment plans to identify priorities and monitor changing exposure.
- Centralized risk assessments
- Linked security controls
- Tracked risk treatment plans
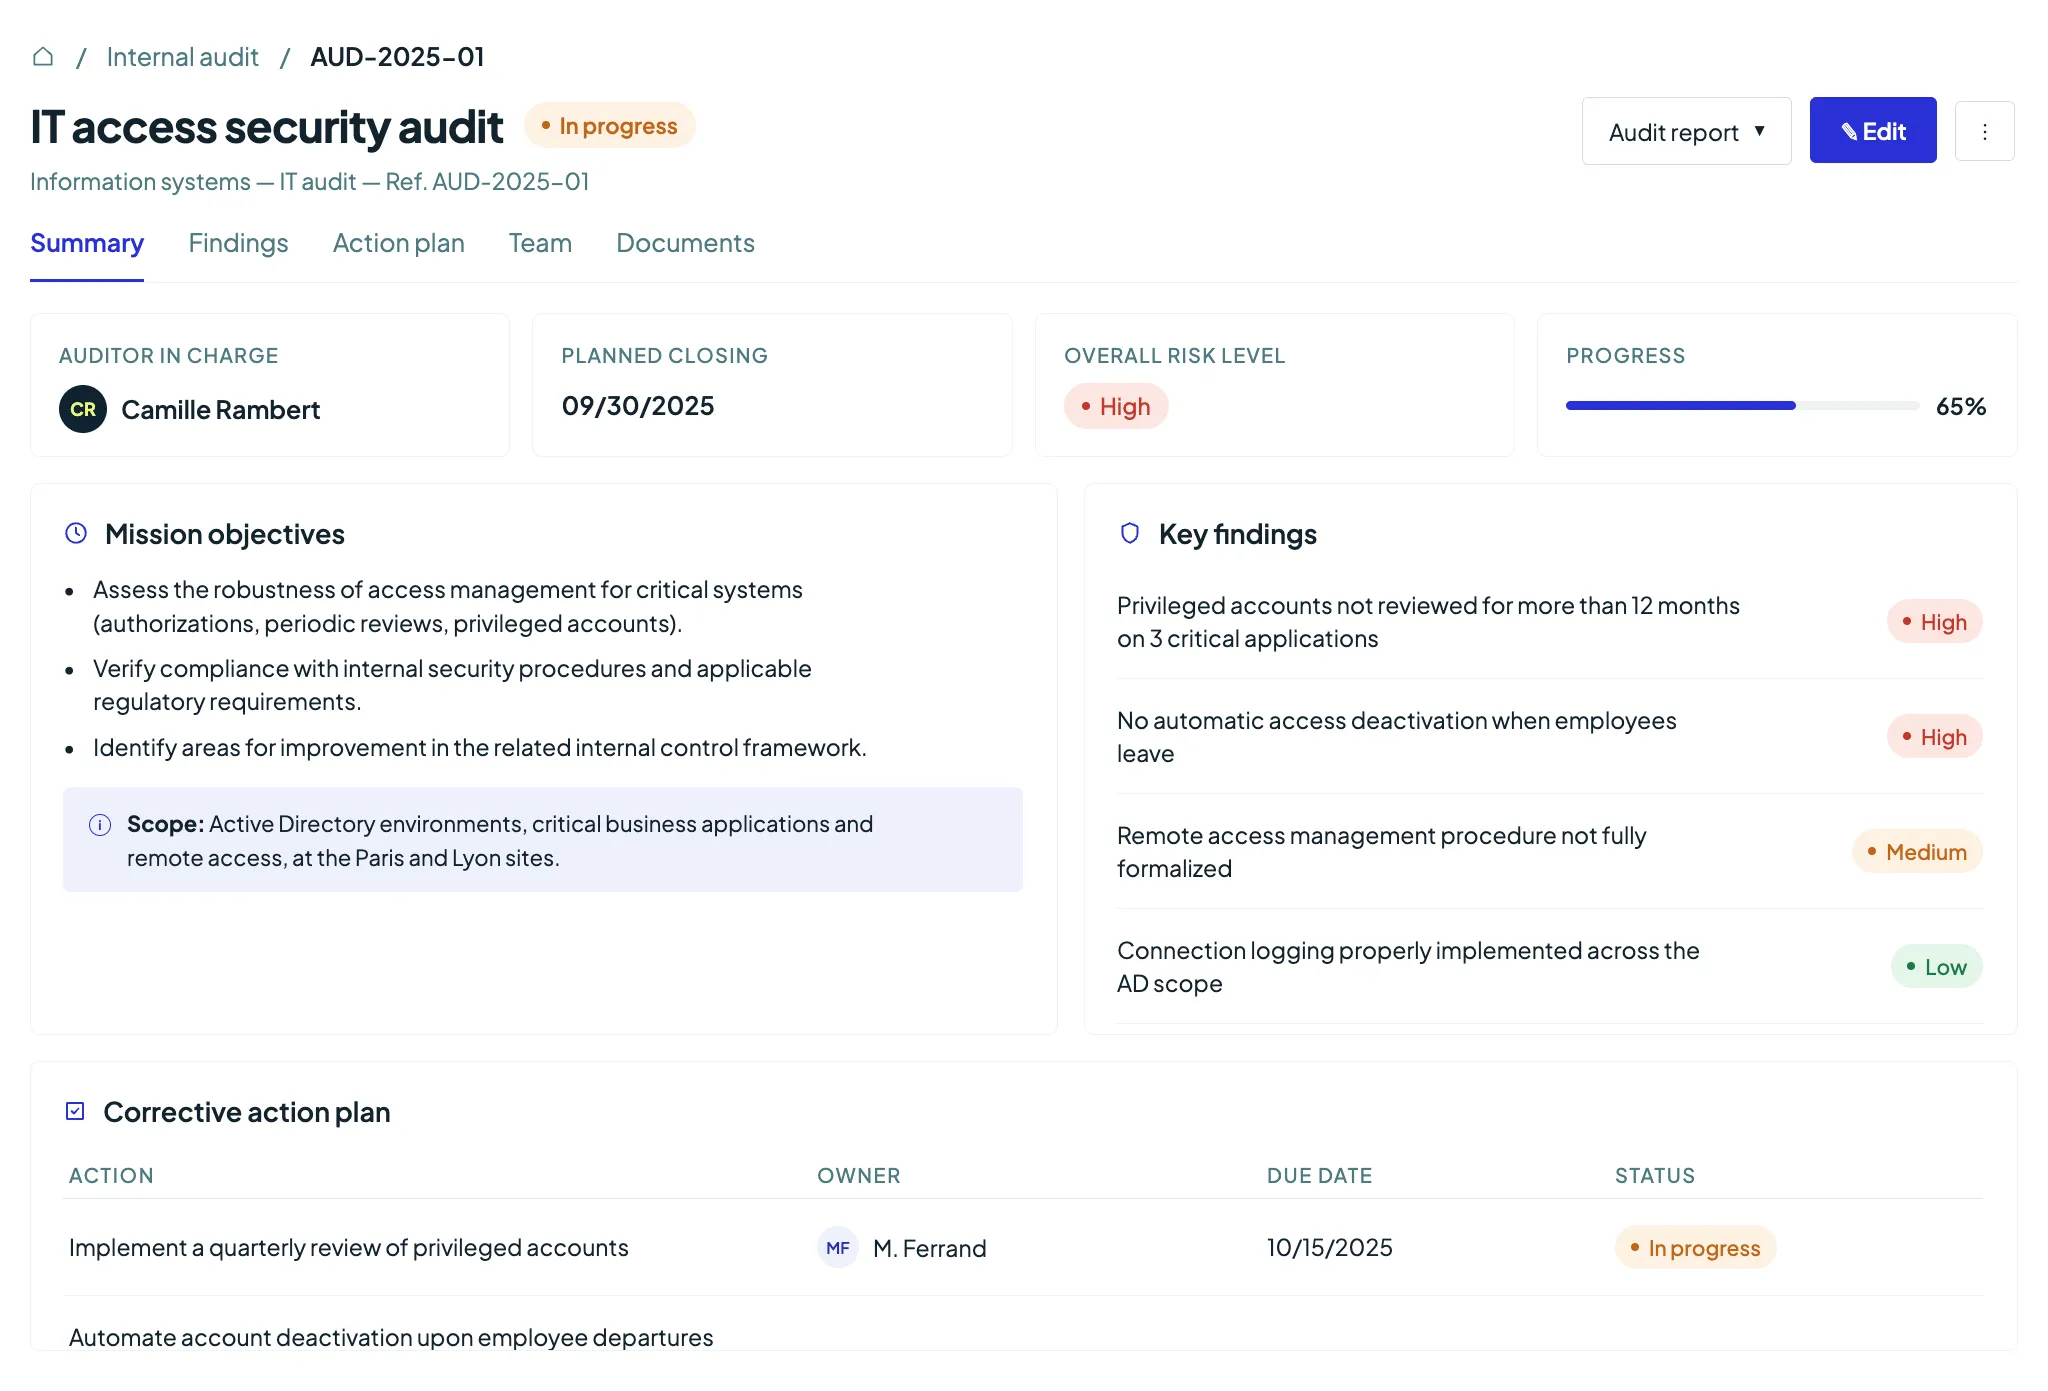
Track security controls and evidence
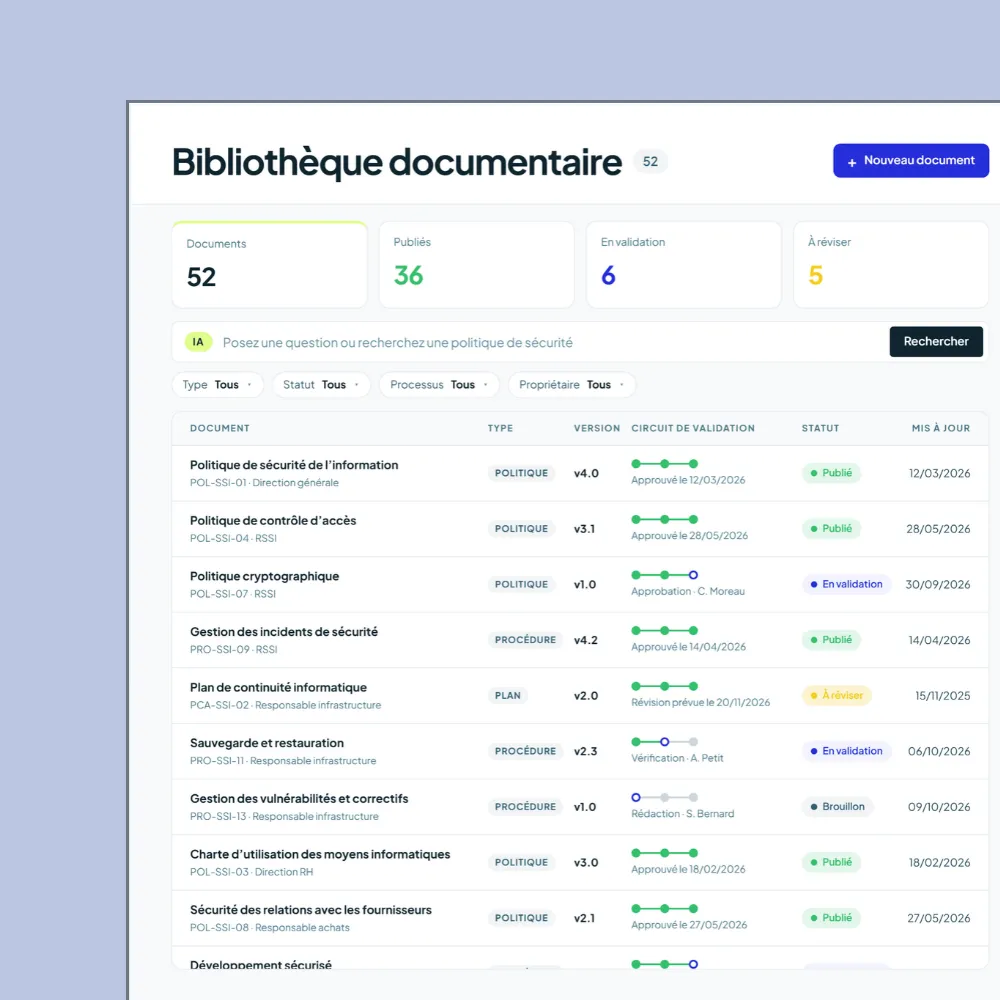
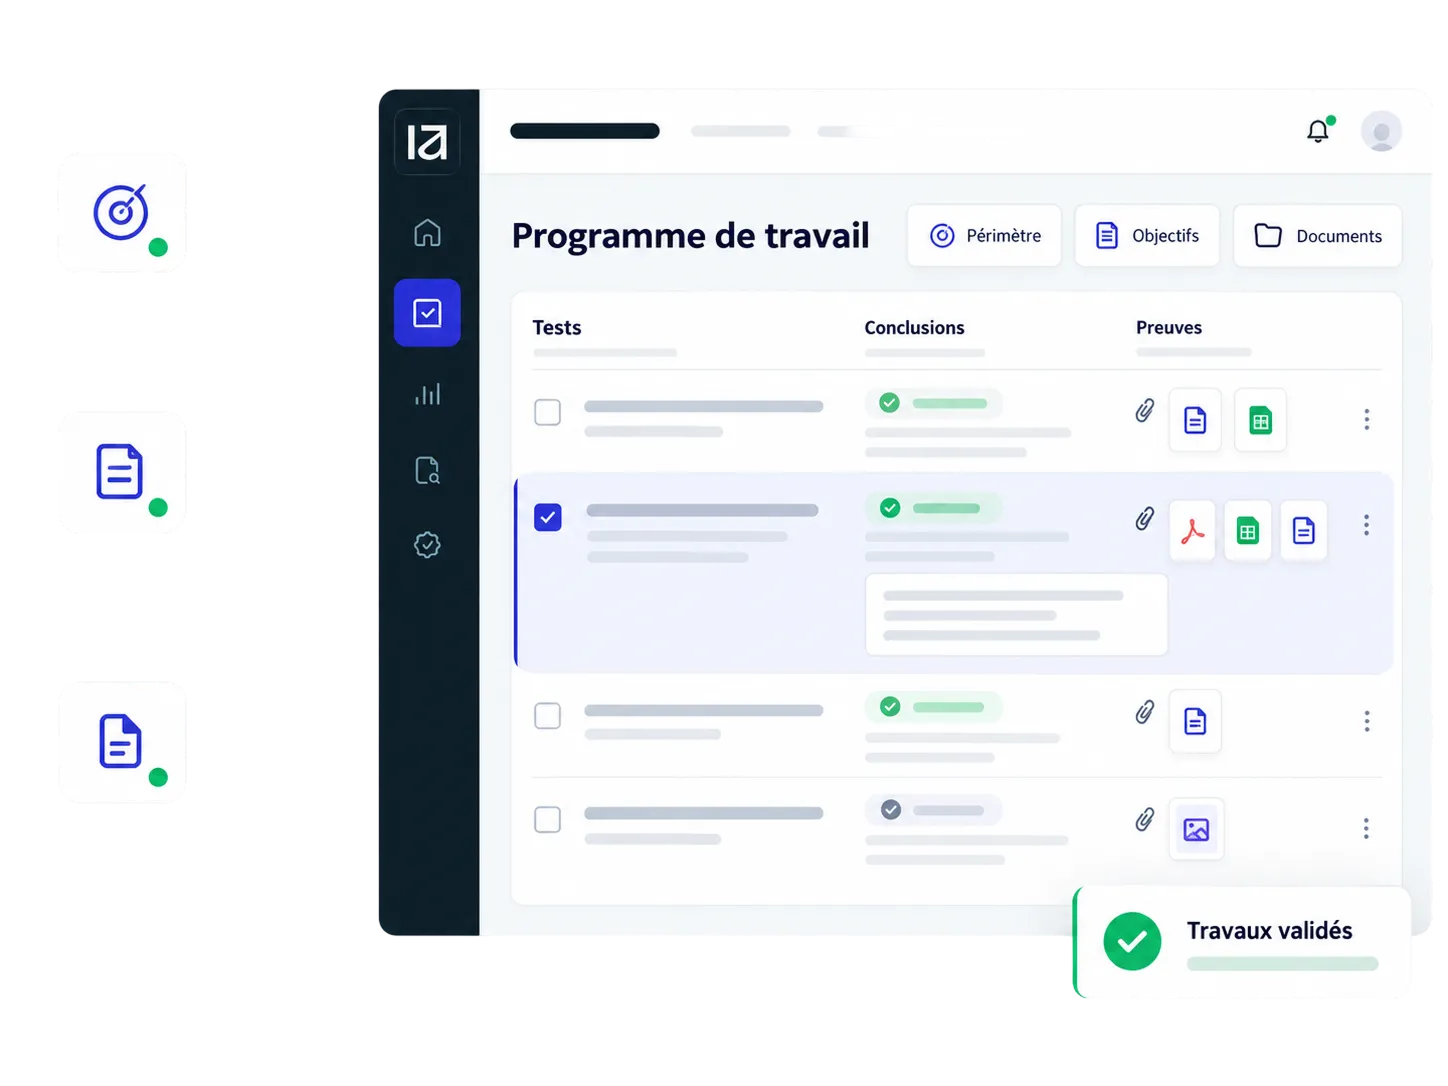
Structure your security controls and monitor their implementation. Link policies, procedures, controls and evidence to relevant requirements. Iskera AI helps find information in your documentation and summarize available evidence.
Iskera AI makes it easier to retrieve relevant documentation and summarize available evidence.
- Centralized security controls
- Linked documents and evidence
- AI-assisted search
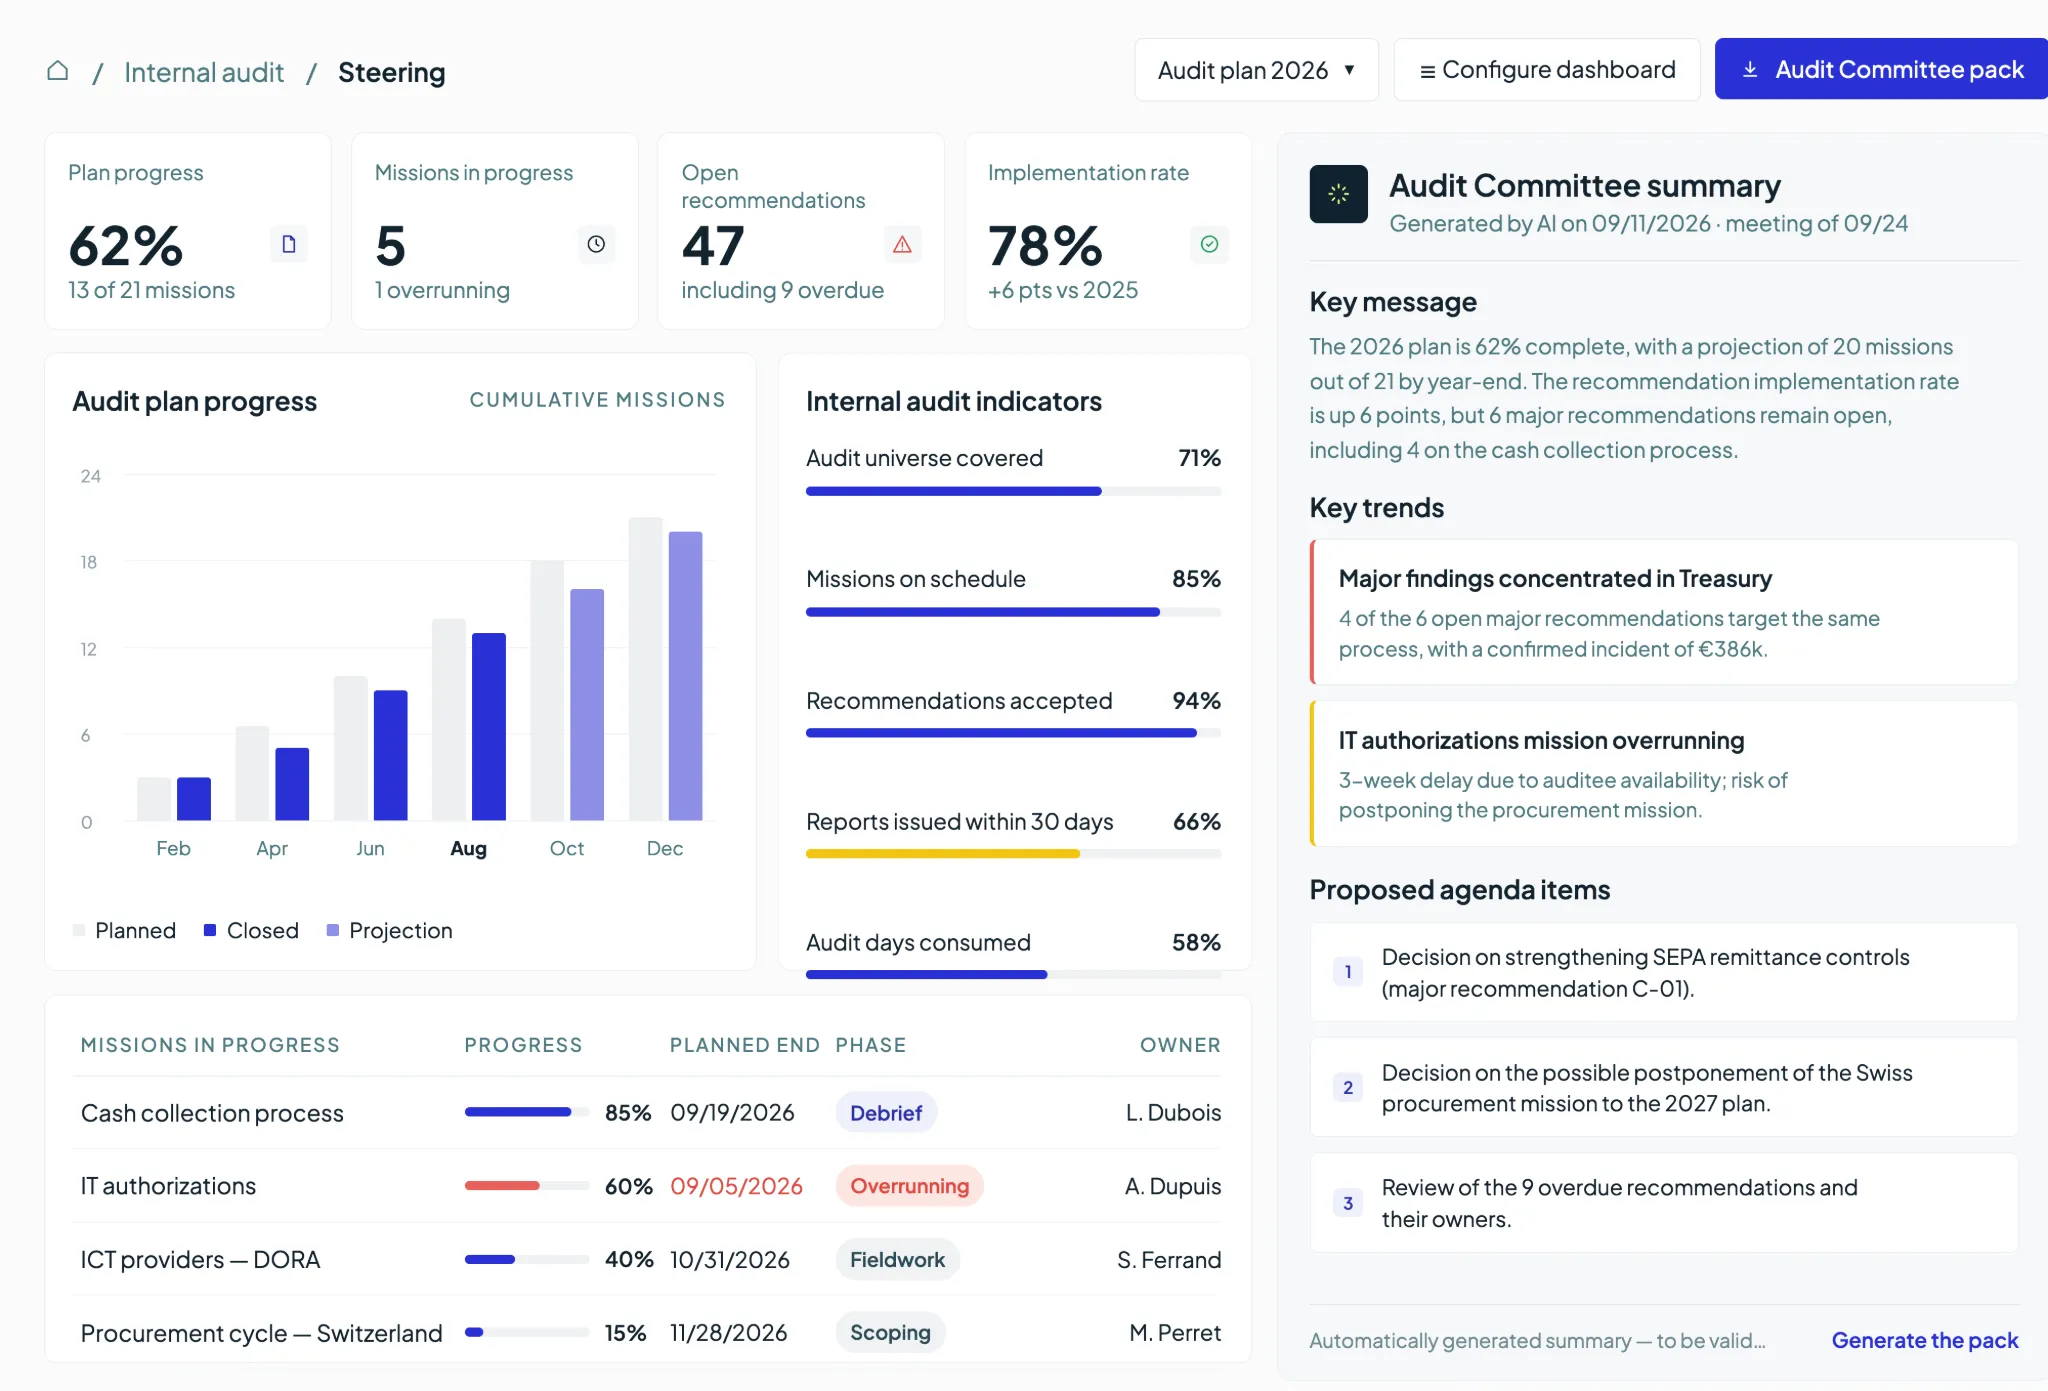
Prepare for ISO 27001 audits with AI
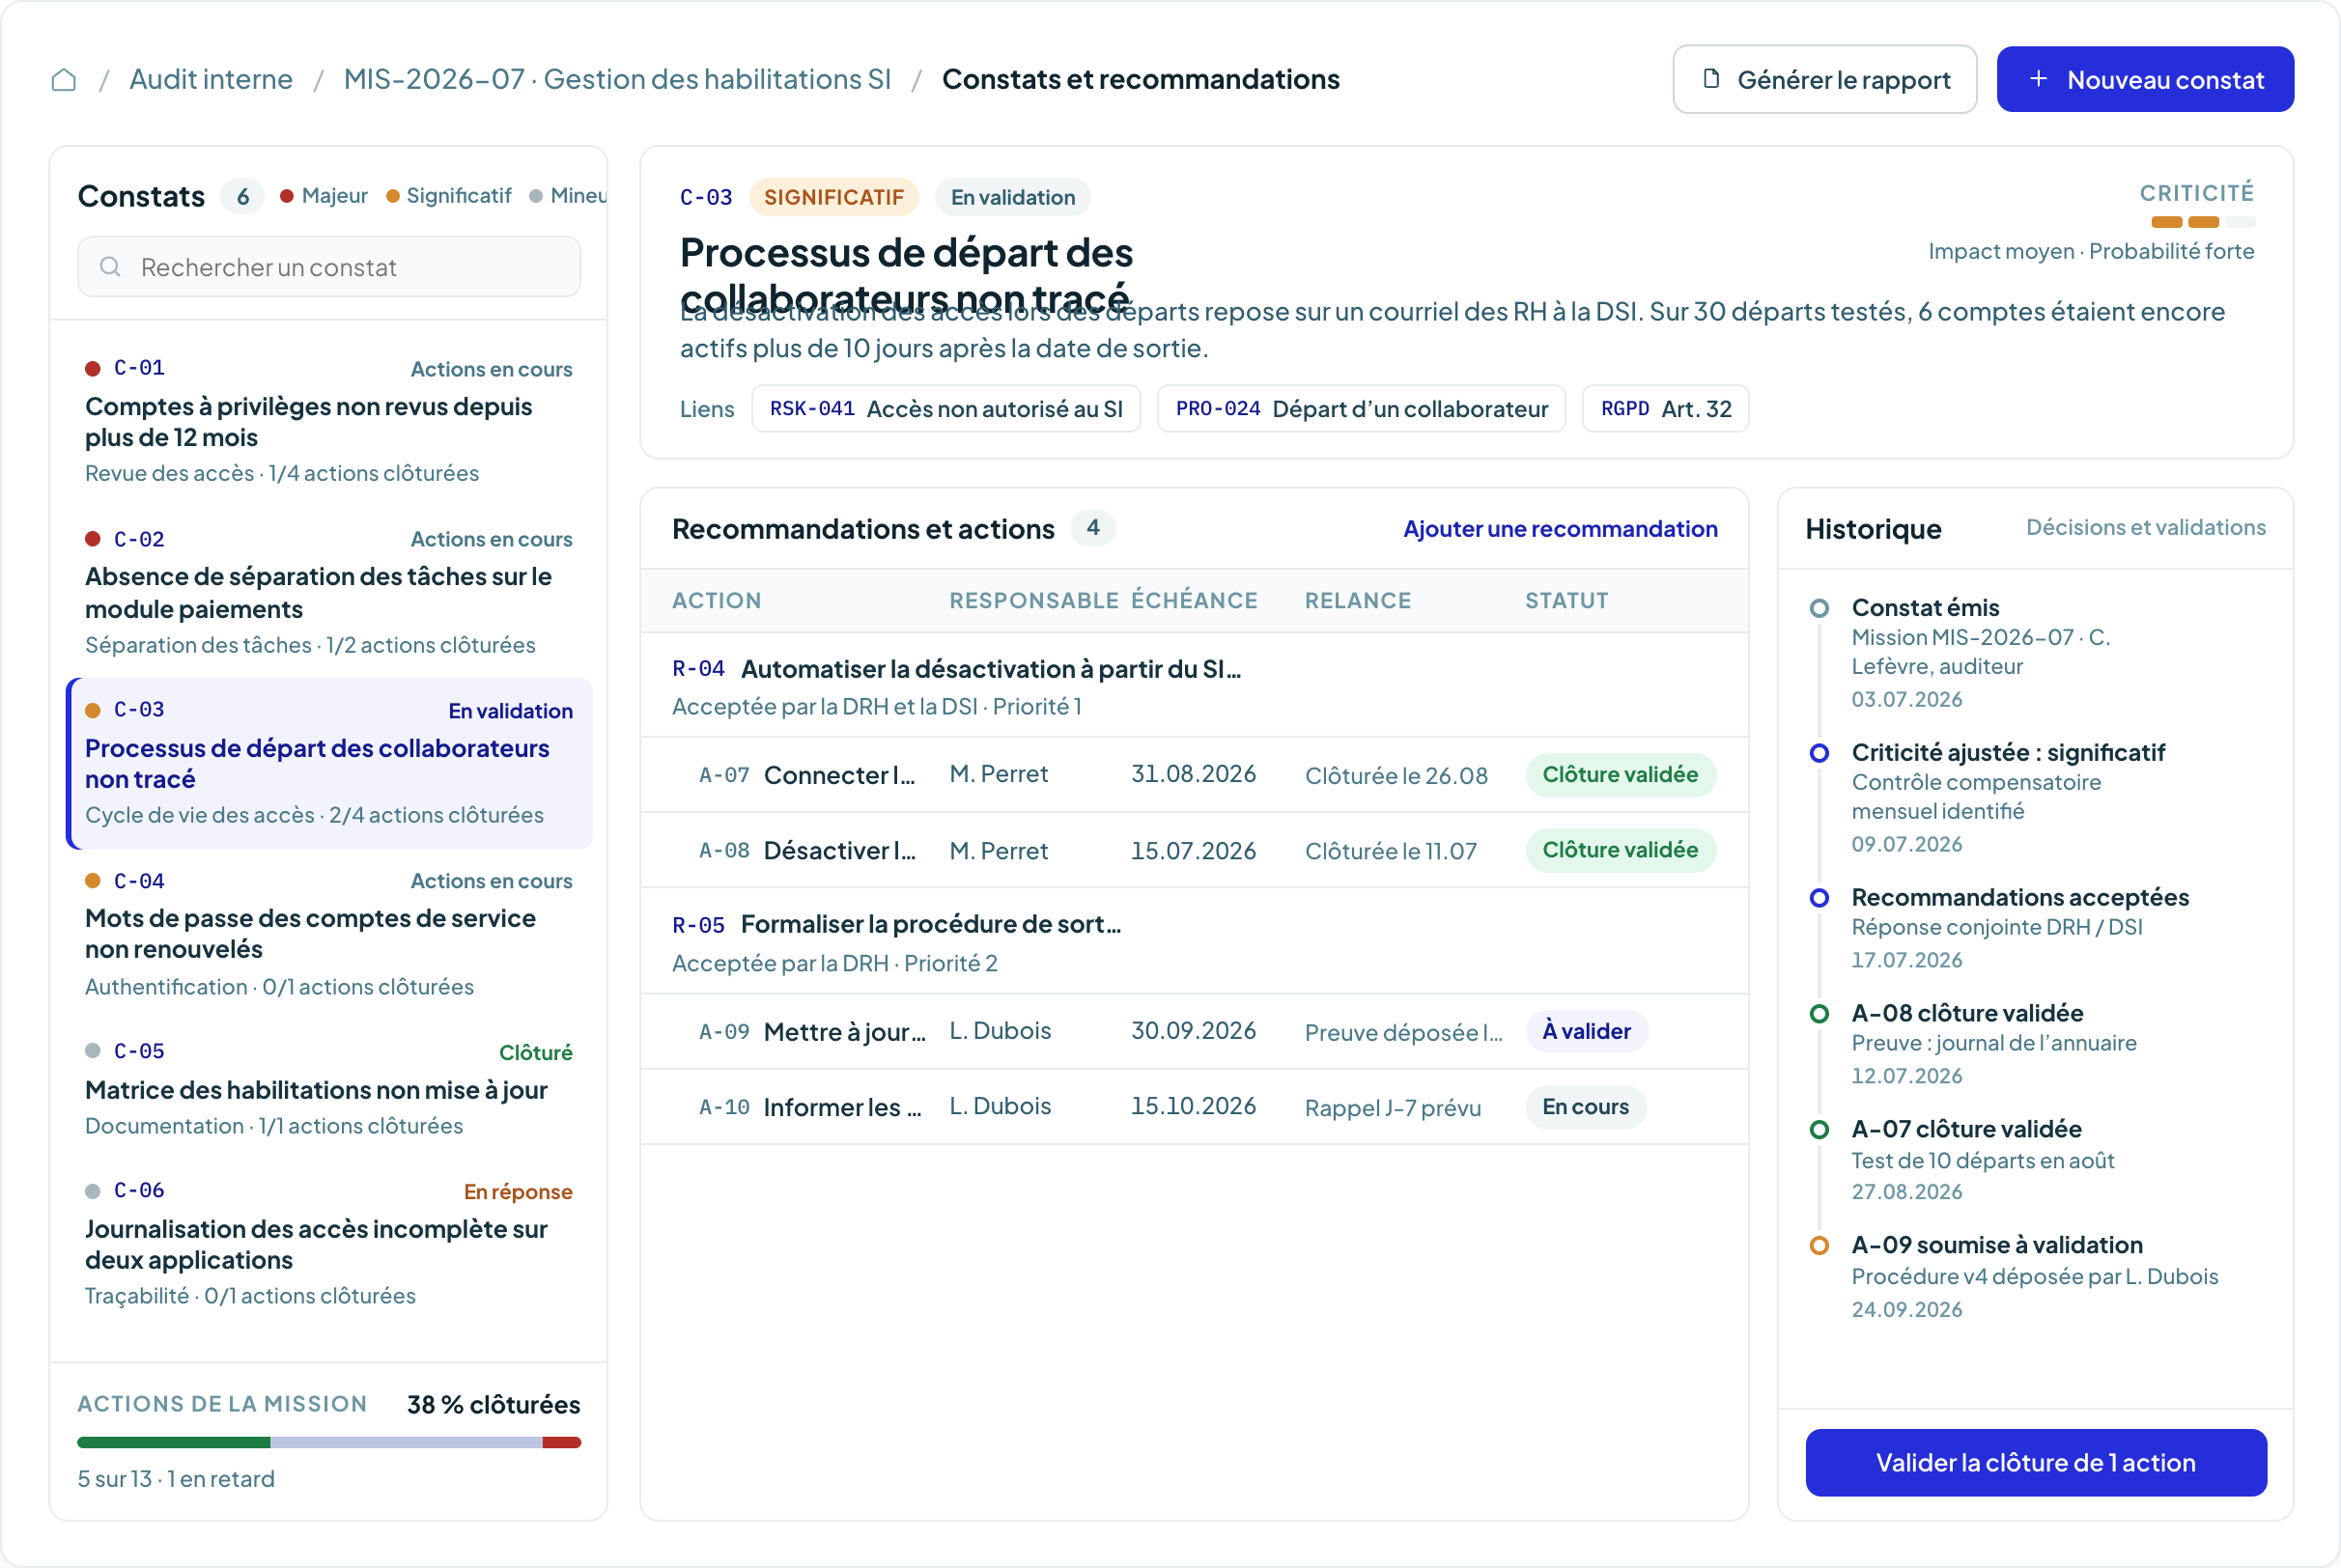
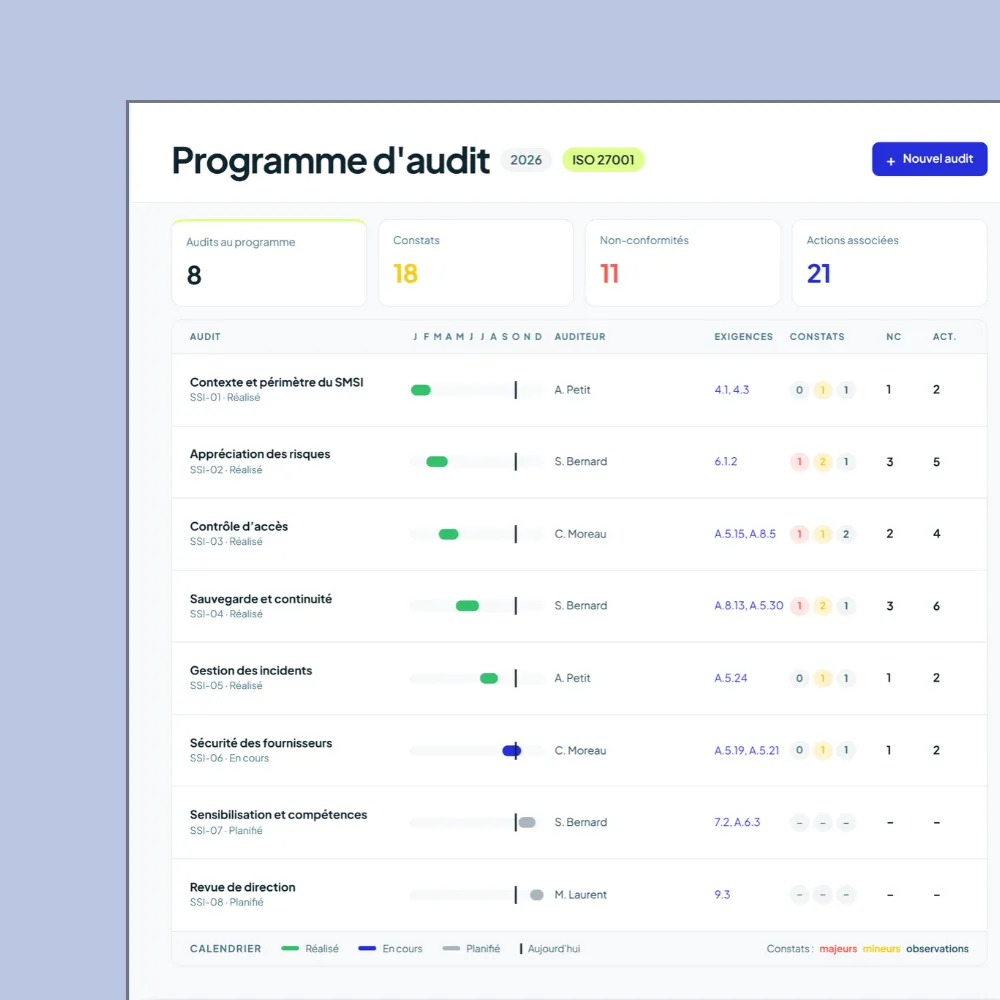
Connect ISO 27001 requirements to risks, assets, security controls, documents, checks and supporting evidence. Iskera AI helps search your ISMS and summarize information before audits. Track findings, nonconformities, recommendations and actions in one place.
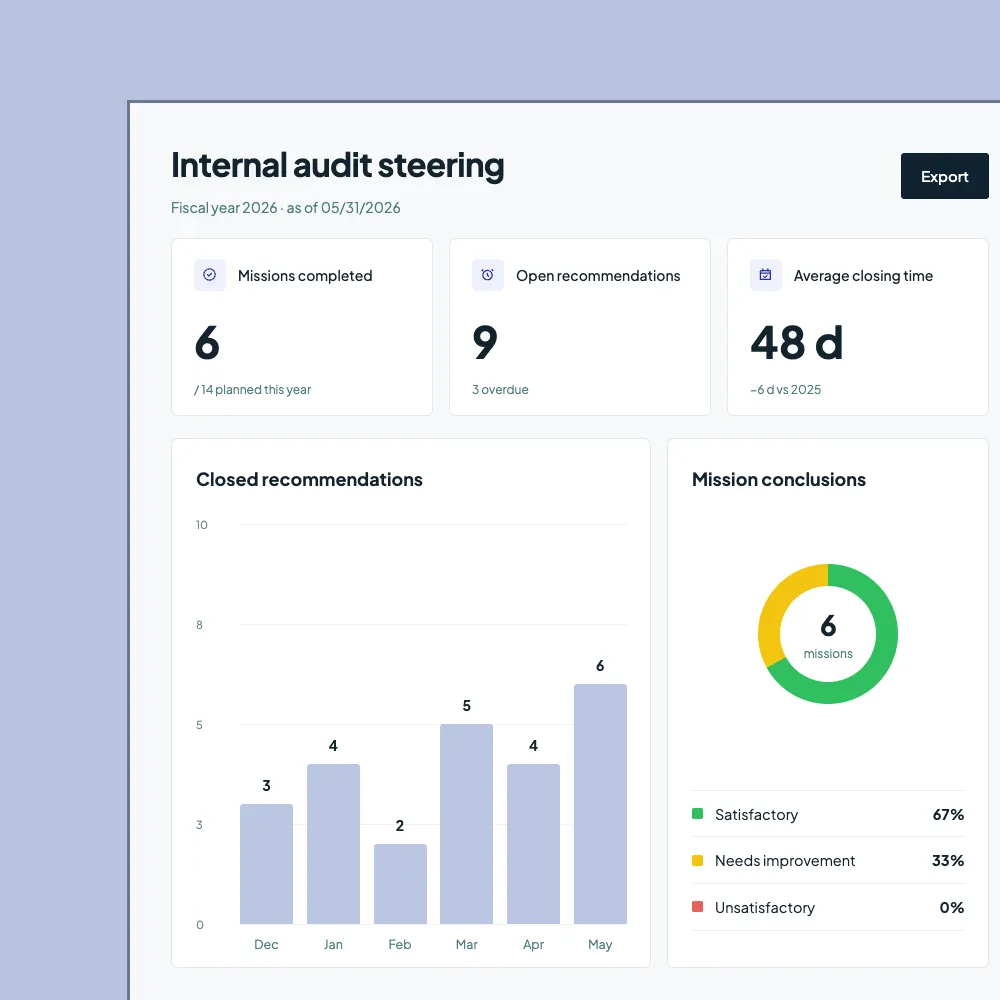
AI-assisted search and summaries simplify audit preparation, while findings, nonconformities and corrective actions stay connected.
- Requirements linked to evidence
- AI-assisted audit preparation
- Centralized findings and actions
An ISMS that's easier to manage

100%
of your ISMS managed in one shared environment
- 01
An up-to-date view of risks
Connect assets, threats, security controls and treatment plans to quickly identify priorities.
- 02
Better traceability
Retain a record of assessments, decisions, controls, incidents and supporting evidence.
- 03
Better action tracking
Centralize risk treatment plans and corrective actions with assigned owners, deadlines and statuses.
- 04
Faster audits with AI
Find relevant documents and evidence faster and prepare summaries from existing information.
Build your ISO 27001 ISMS in 3 steps
Centralize your ISMS, engage your teams and manage information security risks in one shared platform.
01
Centralize your ISMS
Import existing assets, risks, policies, requirements, security controls, incidents, audits and action plans.
Organize information by activity, entity, site, process or information system.
02
Engage your teams
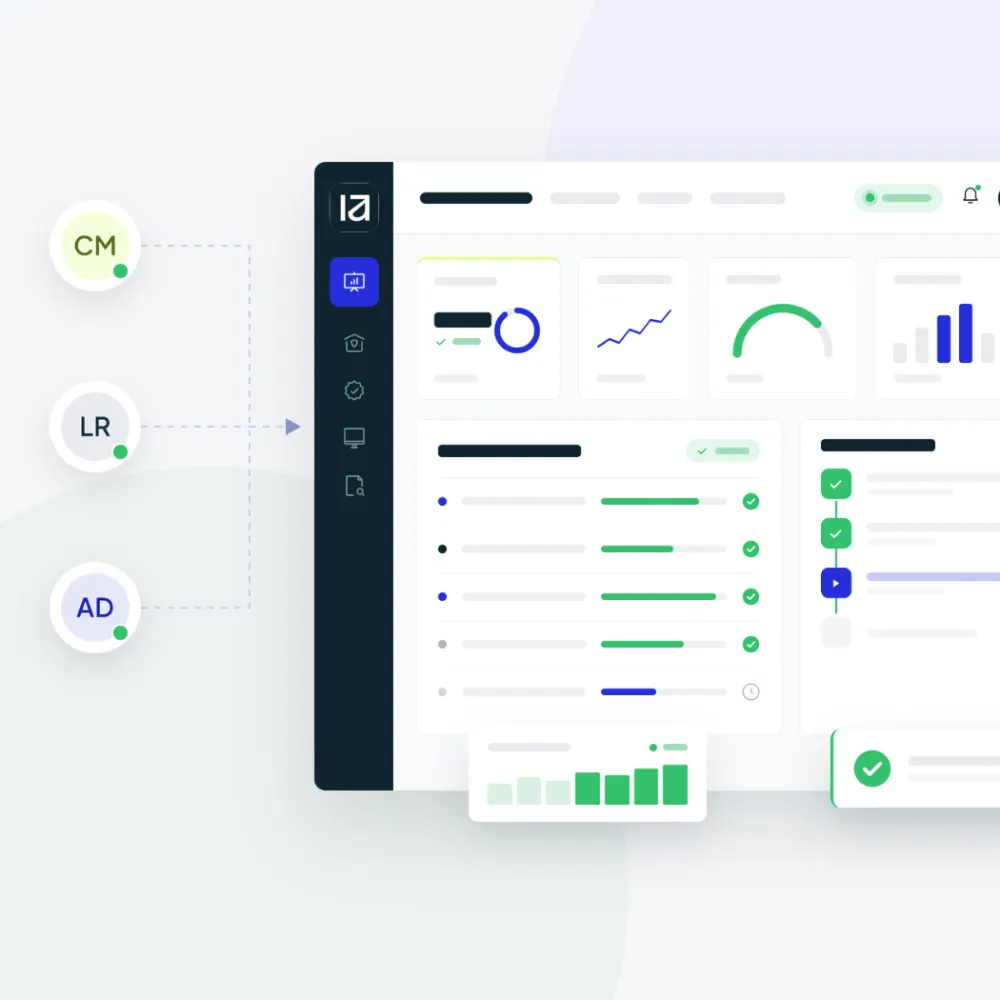
Define asset owners, risk owners, control owners and approval workflows. Give each contributor a clear role in maintaining your ISMS.
03
Manage information security
Track risks, incidents, controls, audits, KPIs and action plans in dashboards. Use AI to search, summarize and highlight areas requiring attention.
Manage your ISO 27001 ISMS day to day
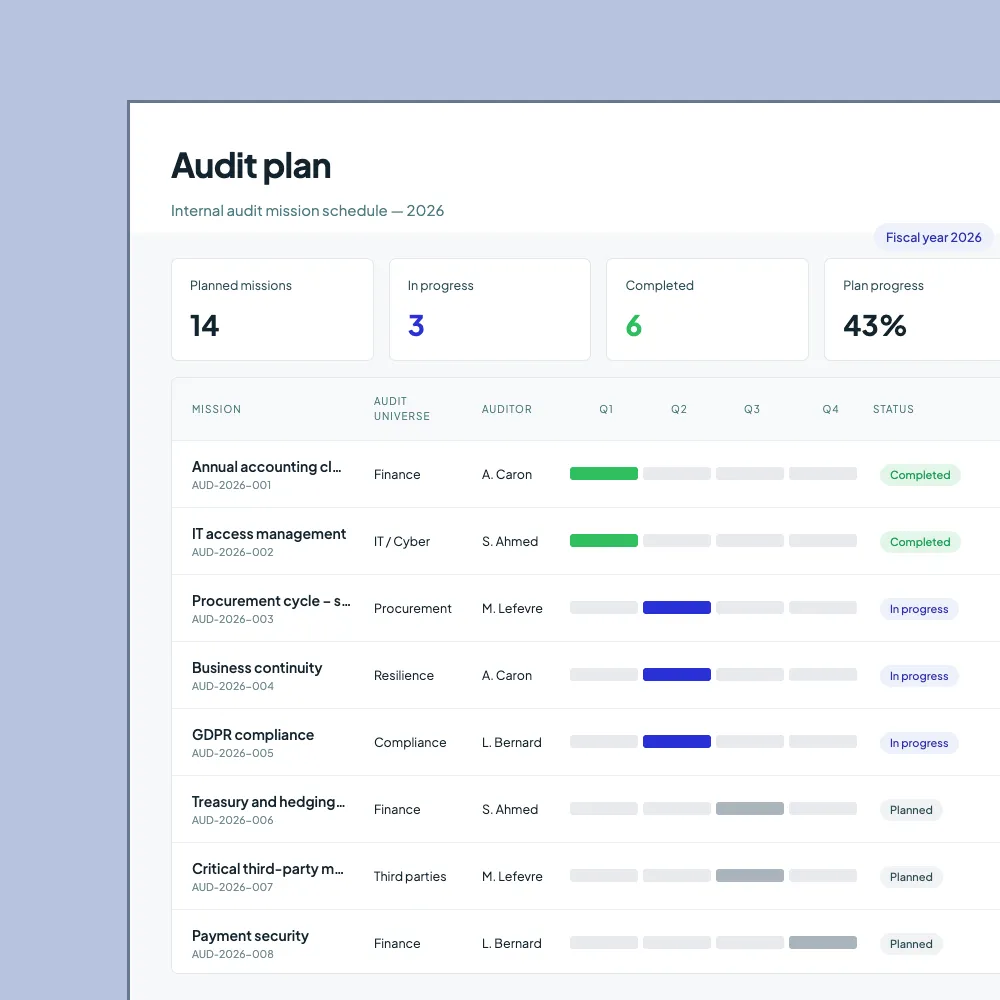
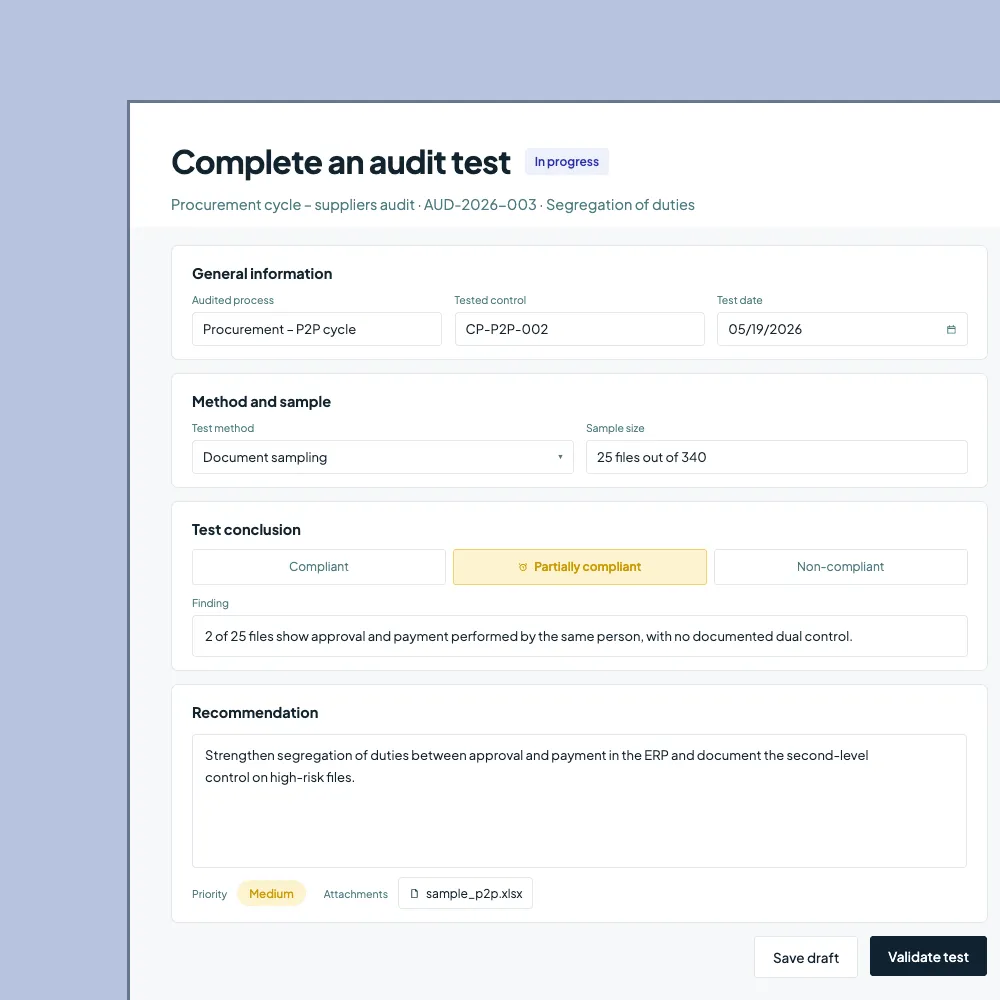
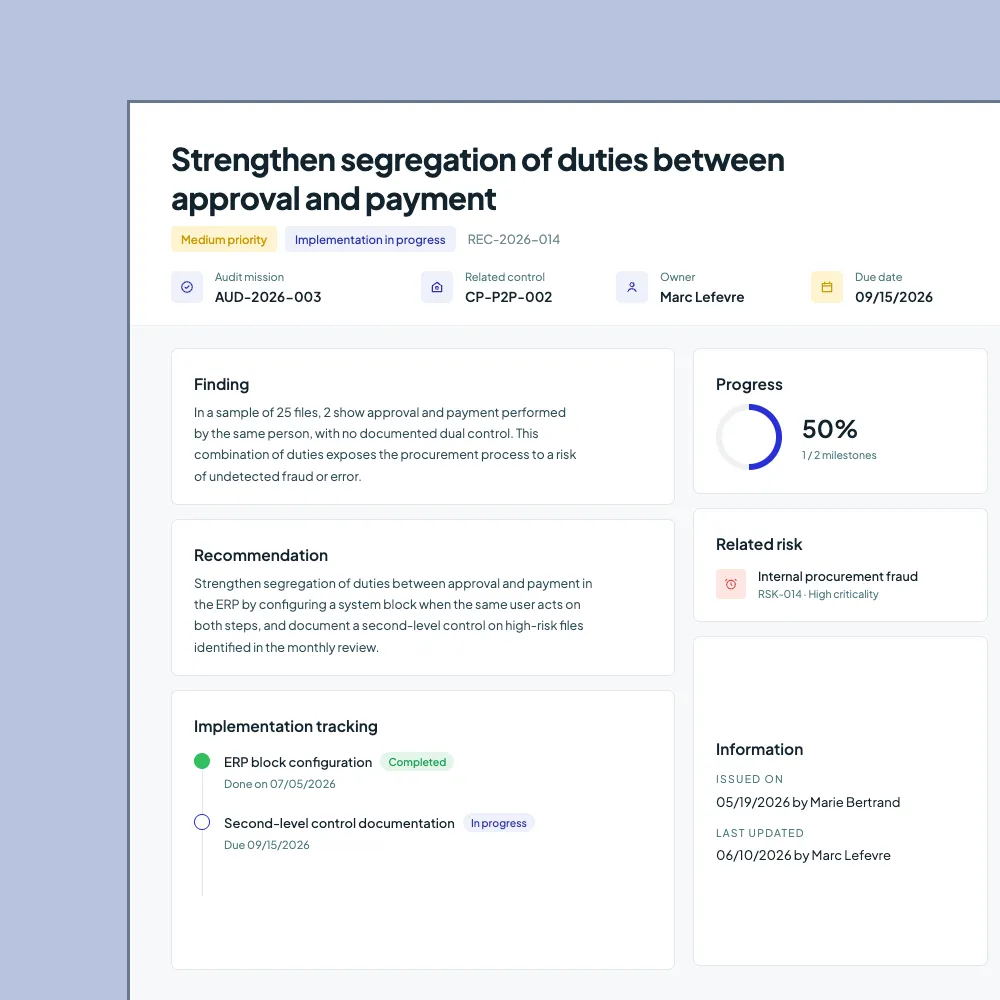
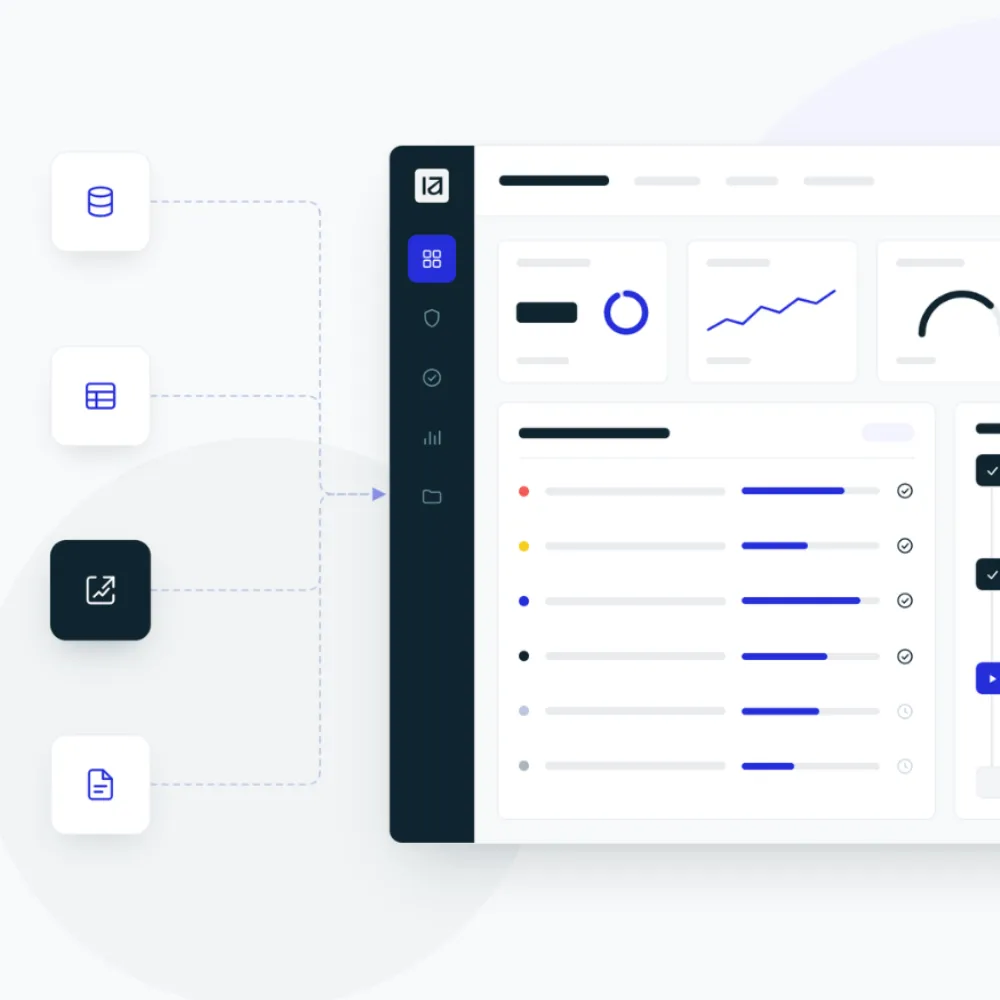
From your existing processes to an operational ISMS
OTHER SOLUTIONS
Connect ISO 27001 to your wider risk management framework
Information security depends on risks, assets, processes, audits, incidents and action plans. Iskera connects them in one shared environment.
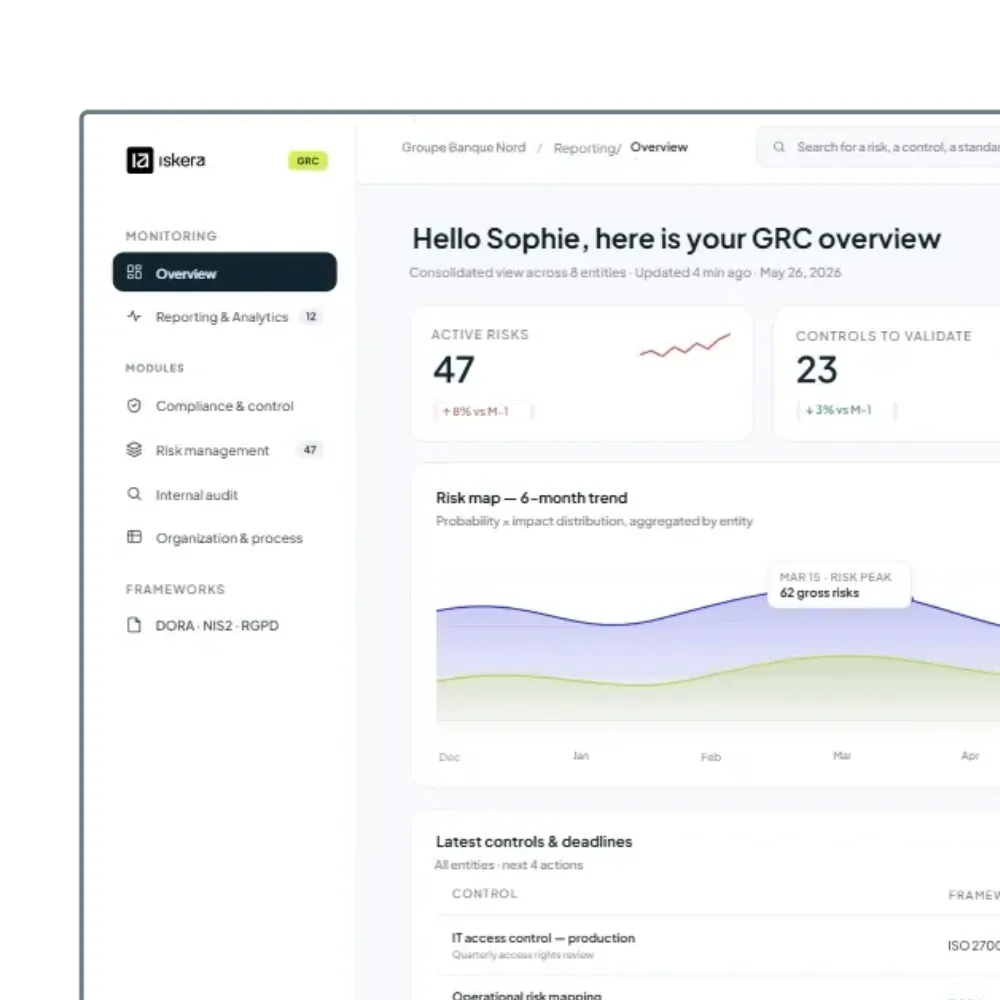
See Iskera in action
See how to centralize your ISMS, manage risks and controls, automate follow-up and use AI for analysis and ISO 27001 audit preparation.
Latest resources
Frequently asked questions
ISO/IEC 27001 is the international standard for information security management systems (ISMS). It provides a framework for identifying security risks, implementing appropriate controls and managing information security over time.
The current edition is ISO/IEC 27001:2022, which replaced the 2013 version and reflects an updated structure of security controls aligned with ISO/IEC 27002.
ISO 27001 applies to organizations of any size or sector, particularly those handling sensitive information or relying heavily on information systems.
An ISMS brings together assets, risks, security controls, requirements, policies, responsibilities, incidents, KPIs, audits and action plans. Iskera helps connect this information.
Identify risks involving assets, activities, threats and vulnerabilities that may affect information security. Assess them, define treatment measures and maintain a record of decisions and actions.
AI helps find documents, summarize scattered information and prepare management reviews and audits. In Iskera, AI supports teams while proposed decisions and actions remain subject to human approval.
Review risks, policies, security controls, responsibilities, incidents, previous audits and available evidence. Iskera links this information to requirements for easier verification.
The Statement of Applicability (SoA) records which security controls have been selected, their implementation status and justifications for exclusions. Iskera helps link controls to risks, owners, evidence and actions.
No. ISO 27001 does not require a particular software product. A dedicated platform can help centralize documentation, improve traceability, monitor risks and controls, and prepare for audits.
Iskera provides tools to structure, document and manage your ISMS. Certification depends on your organization's actual conformity and effectiveness, as assessed by an independent certification body.